TfL Notifies 265,000 Photocard Customers of Potential Data Exposure

Share
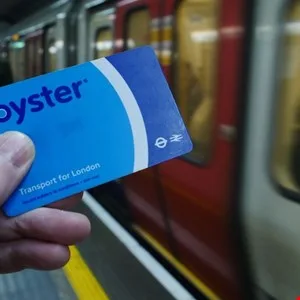
Transport for London (TfL) has confirmed a cyber incident that may have exposed the personal information of approximately 265,000 photocard customers. The breach was identified after unauthorized individuals used TfL’s internal systems to send fraudulent emails to account holders.
The incident occurred on 16 November 2026, when customers began receiving communications generated by the compromised system. These emails instructed Oyster Photocard users to create a new account, even if they already possessed a functioning profile. In response, TfL immediately took the photocard website offline to investigate and contain the intrusion.
Shashi Verma, TfL’s director of technology strategy and revenue, stated that while the organisation acted quickly, it believes account details for roughly 265,000 customers were compromised. The affected group includes users of Zip Oyster cards (issued to children aged 5-18), 18+ Student cards, 60+ London photocards, Apprentice, Veterans, and 18-25 Care Leaver photocards.
Scope of Exposed Data
TfL’s current assessment suggests that highly sensitive information, such as passwords, bank details, and payment card numbers, was not accessed. Furthermore, the organization does not believe that journey history or the names and dates of birth of children using Zip Oyster cards were compromised in the attack.
Despite the limited nature of the data believed to be stolen, TfL has informed the Information Commissioner’s Office (ICO), the UK’s data protection regulator, of the development. The transport body is currently contacting all affected customers to provide guidance on securing their accounts.
Security Recommendations for Customers
While there is no immediate evidence that the compromised data has been exploited for fraud, TfL is advising all photocard customers to update their security credentials. This includes changing passwords as well as security questions and answers on the official TfL website.
Security experts warn that the exposed contact details could be used to facilitate highly targeted phishing campaigns. Users are urged to remain vigilant against unexpected text messages or emails claiming to be from TfL and to avoid clicking on links that do not originate from verified official channels.
The TfL photocard portal remains offline at the time of writing as the investigation continues. However, the transport body confirmed that existing Oyster photocards remain valid for travel, and customers requiring renewals or journey history assistance can contact TfL Customer Services directly.
This incident follows a previous major cyberattack on TfL in September 2024, which led to the breach of bank account details for 5,000 customers. In July 2026, two individuals were sentenced to over five years in prison for their roles in that earlier breach, highlighting the persistent threat facing London’s critical infrastructure.