



Qilin Ransomware Administrator Unmasked as St. Petersburg Man

Share
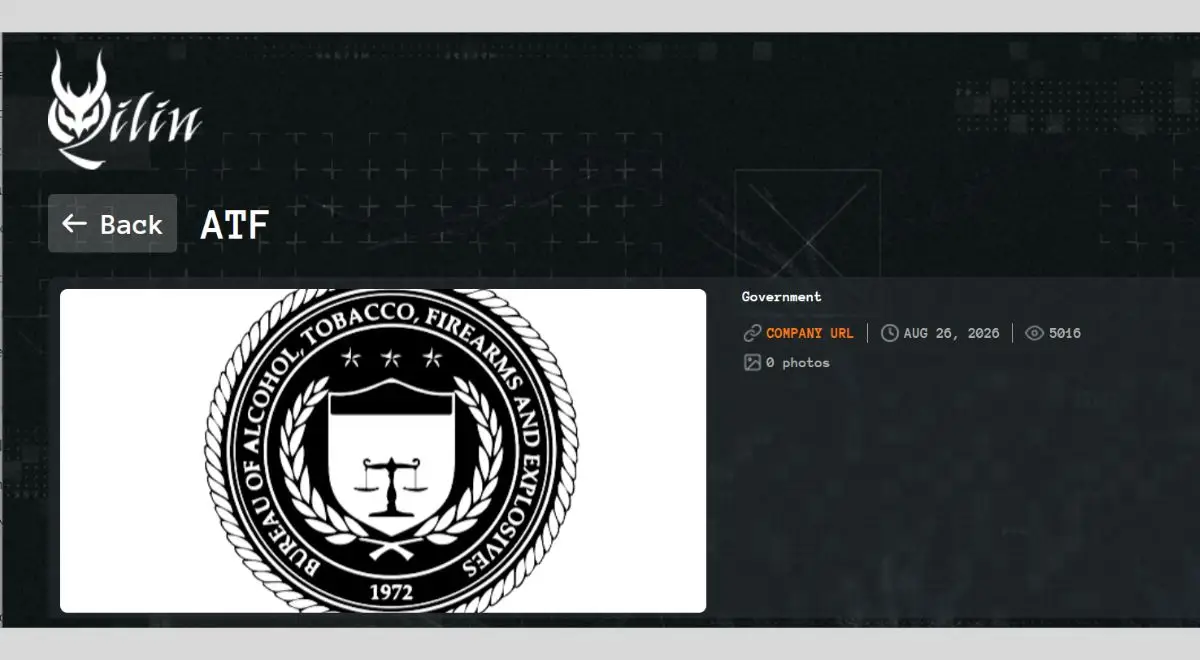
Cybersecurity professionals have reportedly identified an alleged administrator of the Qilin ransomware group, unmasking an individual based in St. Petersburg, Russia. The development represents a significant step in global efforts to track and attribute those behind sophisticated cybercrime operations.
The Qilin ransomware group operates a ransomware-as-a-service (RaaS) model, enabling affiliates to deploy its malicious software against targeted organisations. This often involves a double extortion strategy, where sensitive data is exfiltrated before systems are encrypted, with attackers demanding payment for data recovery and to prevent public release of the stolen information.
While the specific details of the unmasking, including the individual’s full identity and the precise methods used for attribution, were not immediately available, the announcement highlights ongoing successes in identifying key figures within major cybercriminal networks.
Law enforcement agencies and threat intelligence firms worldwide continue to collaborate on investigations into ransomware groups, aiming to disrupt their operations and bring perpetrators to justice. Such identifications are crucial in dismantling the infrastructure and leadership of these illicit organisations.












Leave a Reply