

Security researchers have demonstrated how AI coding assistants can be manipulated by malicious Markdown files to install malware and expose sensitive authentication tokens.
Kali Linux 2026.3 has been released, featuring six new offensive security tools, a kernel upgrade to version 7.1.5, and significant improvements to the KDE Plasma desktop environment.
A new industry coalition has launched the Maritime Vulnerabilities Repository, a database dedicated to tracking IT and operational technology (OT) security flaws specific to the global shipping sector.
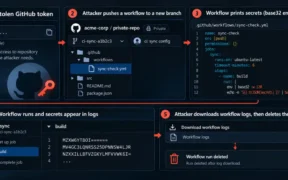
A new automated campaign named Gheist is using stolen access tokens to exfiltrate sensitive data from private GitHub repositories by abusing GitHub Actions logs.

A widespread cybersecurity campaign has leveraged adversary-in-the-middle (AitM) techniques to bypass multi-factor authentication and compromise nearly 100 Microsoft 365 accounts across 79 different organisations.












