



CISA Adds Actively Exploited WordPress Core Vulnerability to KEV Catalogue

Share
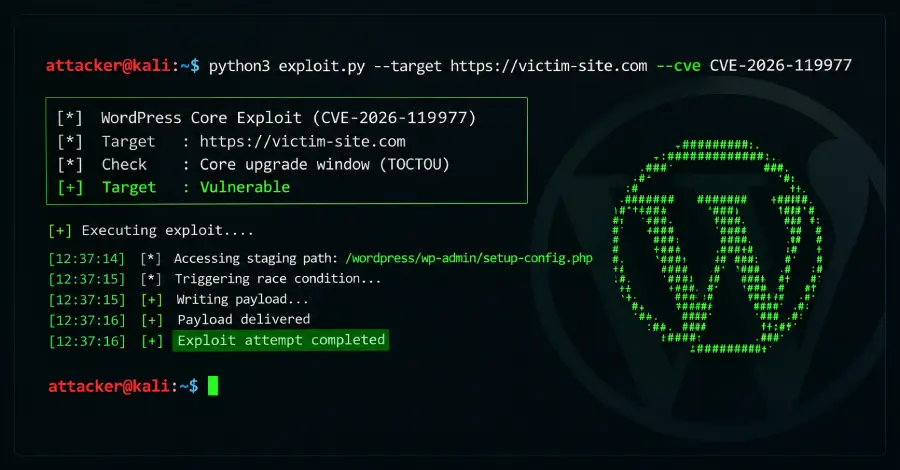
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added a high-severity vulnerability in WordPress Core to its Known Exploited Vulnerabilities (KEV) catalogue following evidence of active exploitation in the wild.
The flaw, tracked as CVE-2026-119977, carries a CVSS severity score of 8.1. It involves a Time-of-check Time-of-use (TOCTOU) race condition that can be triggered during software upgrade processes.
Successful exploitation of this race condition could allow a threat actor to achieve arbitrary code execution on an affected server. This level of access potentially grants attackers the ability to run unauthorised commands and compromise the host system.
CISA’s decision to include the vulnerability in the KEV catalogue indicates that the agency has confirmed threat actors are currently using this specific flaw to target systems. This designation is typically used to alert organisations that a vulnerability is no longer theoretical and is being actively leveraged by attackers.
Website administrators and developers using WordPress are advised to update their software to the latest patched version immediately to prevent exploitation during the update cycle.












Leave a Reply