



How Privacy Policy Changes Affect Insurance Companies

Share
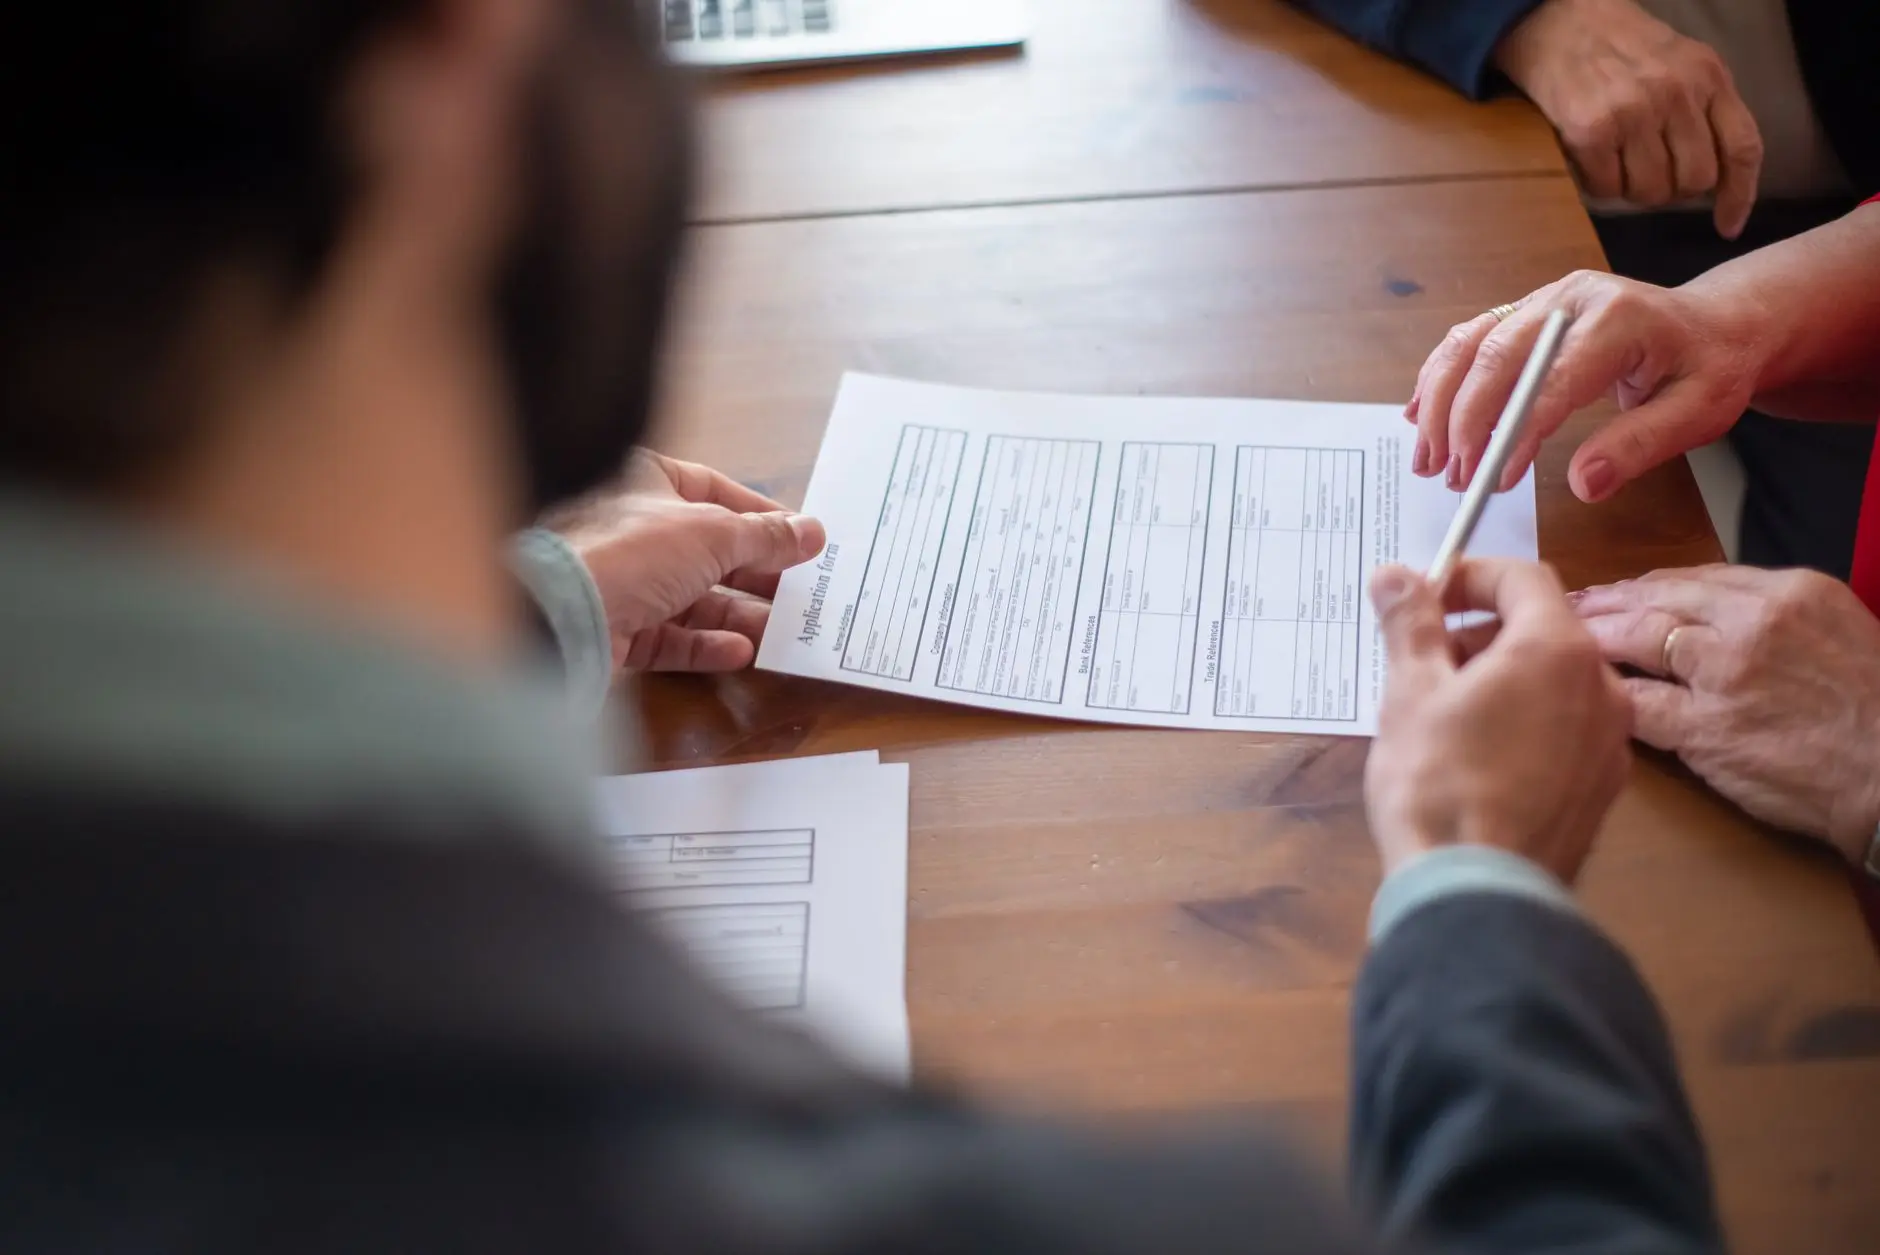
Insurance carriers rely heavily on data to evaluate risk, set premium rates, and process claims. When new data protection laws emerge or existing regulations are updated, operational models must adapt rapidly. Understanding how Policy Changes Affect insurance operations is vital for executives, underwriters, and compliance officers navigating today’s complex legal landscape.
The Intersection of Data Privacy and Risk Assessment
Modern insurance companies ingest vast quantities of personal information. This includes health records, driving history, financial statements, and real-time behavioral data collected through telematics and mobile applications. As global privacy frameworks strengthen, legislators are tightening rules around how this information is collected, processed, and shared.
When regulatory bodies introduce new compliance obligations, insurers face immediate pressure to audit their data pipelines. According to recent insights from the International Association of Privacy Professionals, regulatory alignment remains a top operational expense for financial and insurance institutions worldwide. Data minimization principles mean insurers can no longer hoard consumer data indefinitely just in case it might prove useful for future underwriting models.
Key Operational Impacts on Insurance Carriers
Legislative shifts do not just alter legal documents; they reshape day-to-day business processes across underwriting, claims, and marketing. Here is how policy changes directly alter the insurance sector:
- Underwriting Constraints: Restrictions on profiling and automated decision-making limit how algorithms evaluate risk scores.
- Consent Management: Insurers must secure explicit, granular consent before pulling third-party data or sharing policyholder records with reinsurers and partners.
- Data Subject Rights Fulfillment: Consumers now demand swift fulfillment of access and deletion requests, forcing insurers to upgrade legacy database architectures.
- Increased Exposure to Fines: Non-compliance with modern privacy acts exposes underwriting firms to substantial regulatory penalties and private right-of-action lawsuits.
Comparative Impact of Privacy Frameworks
Different regions enforce unique regulatory mandates that shape carrier behavior differently across global markets. The table below outlines how specific policy focuses impact insurance workflows.
| Privacy Regulation Focus | Primary Impact on Insurance Operations | Action Required by Compliance Teams |
|---|---|---|
| EU GDPR | Strict limits on automated profiling and mandatory data protection impact assessments. | Deploy human oversight loops in automated underwriting algorithms. |
| State-Level US Privacy Laws | Opt-out rights for targeted advertising and sale of sensitive personal data. | Implement clear consent banners and global privacy control signals. |
| Sector-Specific Privacy Acts | Stringent rules on medical and financial data sharing between subsidiaries. | Isolate data silos and enforce strict role-based access controls. |
Real-Life Scenario: The Telematics Dilemma
Consider a national auto insurance provider that offers discounted rates to drivers who install a mobile tracking app. The app monitors speed, braking habits, and daily mileage. Under older regulatory regimes, the company retained this telemetry data indefinitely to refine its predictive risk models. Following recent privacy policy updates restricting data retention and secondary use, the firm had to re-architect its entire cloud environment.
The company was forced to anonymize driving metrics after thirty days and give users an explicit dashboard to revoke telemetry tracking instantly without losing their base policy. While this required significant software engineering investment, it ultimately protected the carrier from regulatory scrutiny and built greater consumer trust.
Actionable Steps for Insurance Compliance Teams
To stay ahead of evolving legal standards, insurance executives and risk managers should implement the following strategic steps:
- Conduct Comprehensive Data Mapping: Identify every touchpoint where customer data enters the enterprise, including third-party data brokers and legacy systems.
- Review Automated Decision Systems: Audit algorithms used for claims adjudication and pricing to ensure compliance with anti-profiling provisions.
- Update Privacy Notices: Ensure public-facing privacy policies clearly communicate what data is collected, why it is needed, and how long it is stored.
- Train Frontline Staff: Educate customer service and claims representatives on handling data subject access requests securely and efficiently.
Frequently Asked Questions
How do privacy policy changes affect insurance pricing?
Restrictions on using certain behavioral or demographic data points can force insurers to rely on broader risk categories, which may flatten pricing structures or require new ways of assessing individual risk accurately.
Can insurance companies still use telematics data?
Yes, but typically only with explicit, informed consent from the policyholder, clear limitations on retention periods, and strict adherence to data minimization principles.
Conclusion
Navigating the complex ways Policy Changes Affect insurance requires proactive adaptation rather than reactive compliance. By treating data privacy as a core component of risk management rather than a mere legal hurdle, insurance companies can protect their balance sheets, secure customer trust, and maintain a competitive edge in a highly regulated digital economy.












Leave a Reply