



The Invisible Tower: Why Nigerians Need to Know About Rogue Base Stations

Share
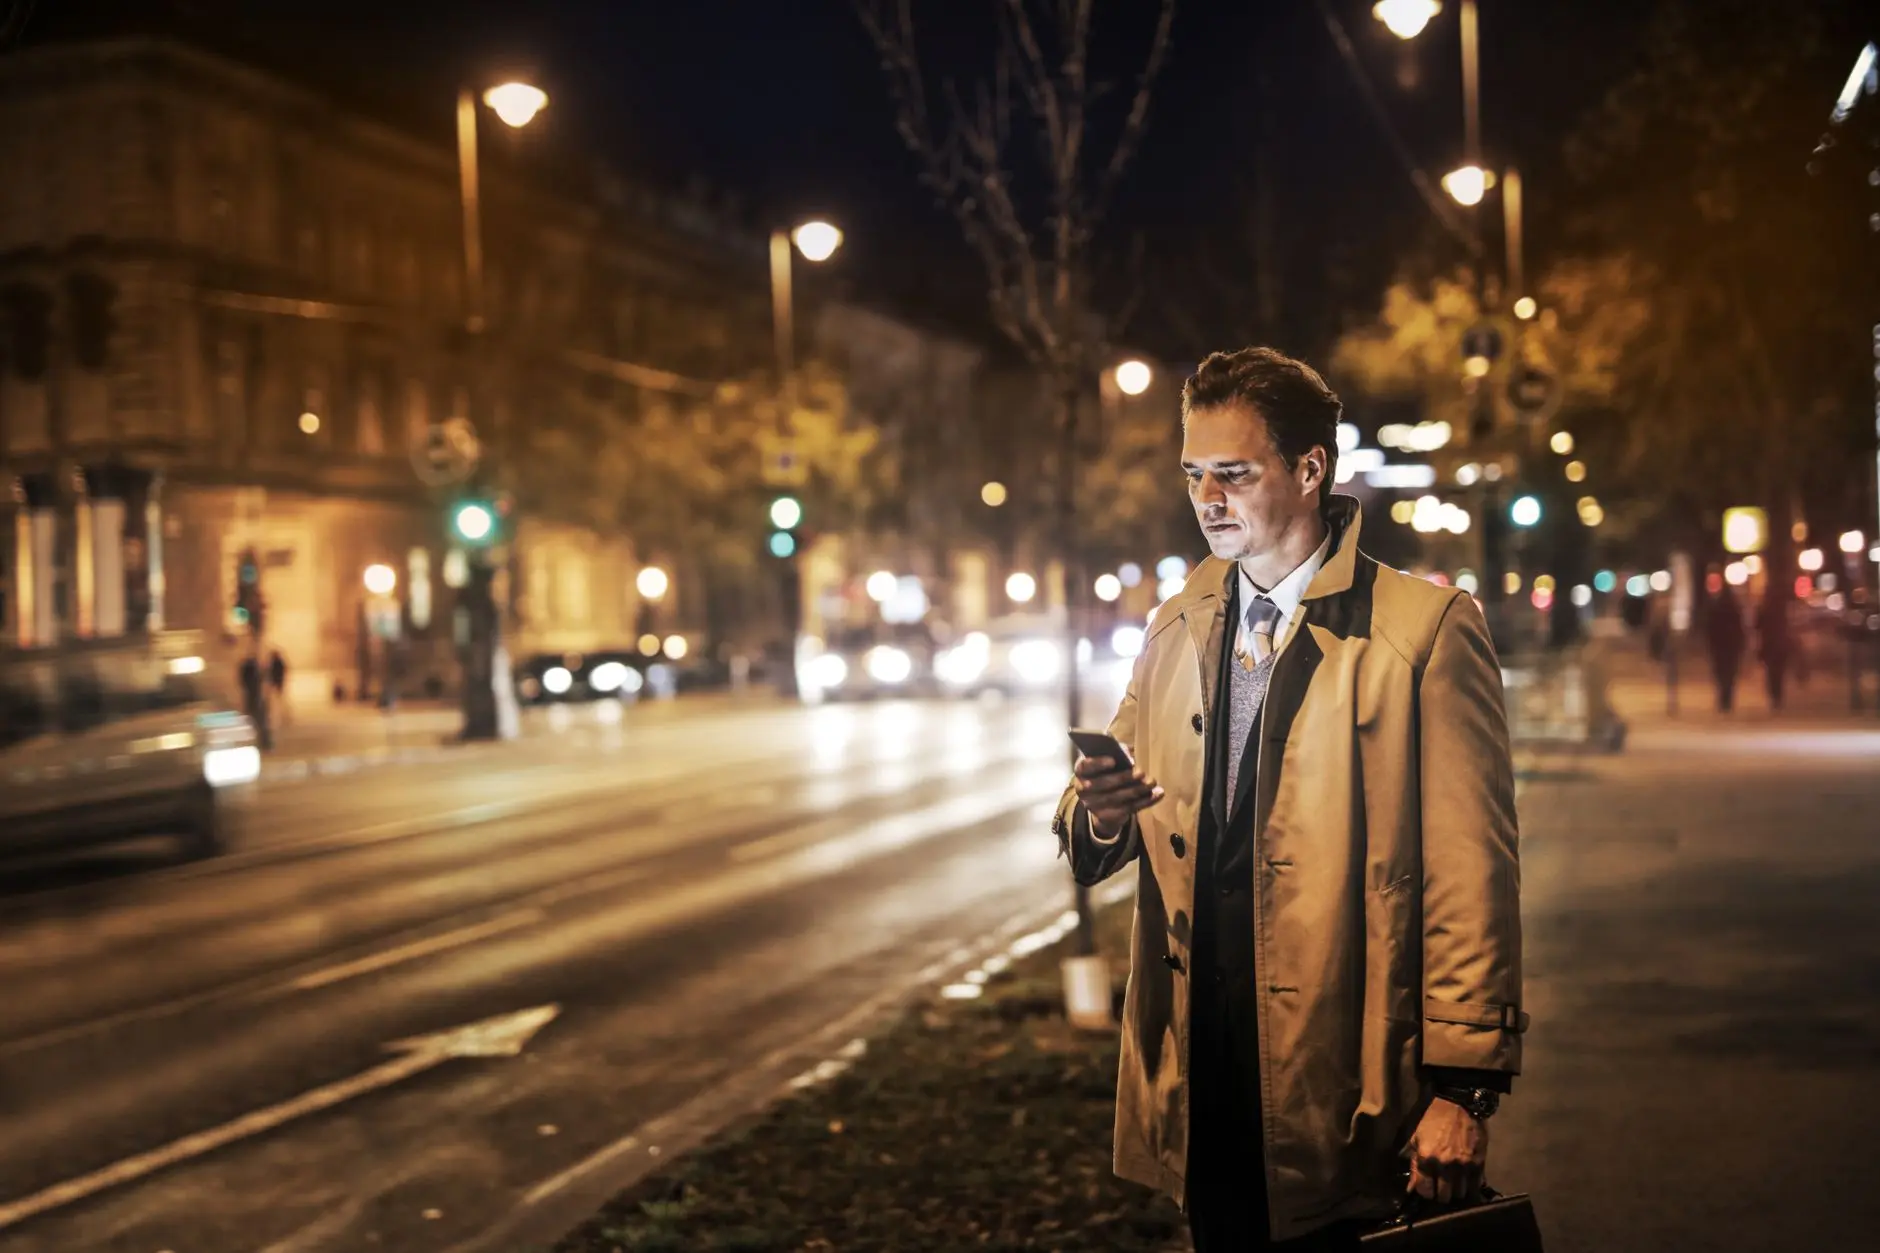
In cities like Lagos, Abuja, and Kano, the smartphone is more than a communication tool; it is a mobile bank, a digital identity, and a primary gateway to the economy. For millions, the ability to transact via USSD codes or receive SMS-based One-Time Passwords (OTPs) is the backbone of daily life. However, this heavy reliance on cellular networks creates a specific vulnerability that most users never see coming: the rogue base station.
Often referred to as IMSI catchers or “Stingrays,” rogue base stations are fraudulent cellular towers that mimic legitimate network providers. They trick nearby mobile devices into connecting to them instead of the actual service provider. For the average user, the transition is often seamless and undetectable, but for an attacker, it provides a golden opportunity to intercept sensitive information.
What is a Rogue Base Station?
A legitimate base station is a cell tower operated by a licensed telecommunications provider. It uses encrypted protocols to ensure that your phone and the network can verify each other’s identity. A rogue base station breaks this trust. It broadcasts a signal that is stronger or more “attractive” than the legitimate tower, prompting your phone to perform a handoff to the malicious device.
Once a device is connected to a rogue station, the attacker can perform several high-impact actions. They can capture your International Mobile Subscriber Identity (IMSI), which is a unique number tied to your SIM card. More dangerously, they can perform a “downgrade attack,” forcing your phone to move from secure 4G or 5G networks down to older, less secure 2G protocols that lack robust mutual authentication.
The Critical Threat to Nigeria’s Mobile Economy
Understanding why nigerians need know rogue base station mechanics is not just a technical exercise; it is a financial necessity. Nigeria has one of the highest mobile penetration rates in Africa, and a significant portion of the population relies on Unstructured Supplementary Service Data (USSD) for banking.
When an attacker controls a rogue base station, they sit in the middle of your communication (a “Man-in-the-Middle” attack). If you attempt to perform a bank transfer via USSD or receive an OTP via SMS, that data travels through the attacker’s equipment. They can intercept the code, intercept your credentials, or even redirect your transaction requests in real-time.
Comparing Legitimate and Rogue Base Stations
| Feature | Legitimate Base Station | Rogue Base Station |
|---|---|---|
| Authentication | Mutual authentication between device and network. | Often bypasses or disables authentication. |
| Network Protocol | Prioritizes secure 4G, 5G, or LTE. | Forces downgrade to insecure 2G or 3G. |
| Signal Behavior | Consistent and follows network patterns. | May show sudden, unexplained signal jumps. |
| Data Security | End-to-end encryption is standard. | Attempts to strip encryption from traffic. |
Real-World Scenario: The Lagos Commuter
Imagine a business professional commuting through a high-traffic area in Victoria Island. As they enter a crowded bus terminal, their phone signal suddenly jumps from full 4G to a single bar of 2G. They don’t think much of it, assuming it is just poor coverage. During this time, they receive a notification to authorize a high-value business payment via an SMS OTP.
What they don’t know is that a small, portable rogue base station is hidden in a nearby vehicle. The device has forced their phone onto a 2G connection, allowing the attacker to intercept the incoming SMS in plain text. The attacker captures the OTP, enters it into a fraudulent transaction on their own device, and drains the professional’s account before the victim even realizes their signal was compromised.
Risks for Businesses and Compliance Teams
While individual users are at risk of theft, businesses face different, more systemic dangers. For companies operating in Nigeria, the risk of rogue base stations extends to corporate espionage and data breaches. If executives travel frequently, their mobile devices could be used to harvest contact lists, intercept corporate emails sent over cellular data, or map the location of key personnel.
For compliance teams, this highlights a gap in the traditional perimeter defense model. Even if your office Wi-Fi is secure, the cellular network your employees use to stay connected while on the move might not be. Organizations must consider these mobile-layer threats when conducting risk assessments and developing data protection policies.
“The inherent weaknesses in older cellular protocols allow attackers to bypass modern security layers by simply forcing a device to communicate using outdated standards,” says a leading cybersecurity researcher.
How to Protect Yourself and Your Organization
It is important to note that while no technology offers zero risk, you can significantly reduce your vulnerability by following these practical steps:
- Use Encrypted Messaging Apps: Rely on apps like Signal or WhatsApp for sensitive communications. These use end-to-end encryption that remains intact even if the cellular connection itself is intercepted.
- Be Wary of Signal Changes: If your phone suddenly drops from 4G/5G to 2G in an area where coverage is usually excellent, be cautious about performing financial transactions.
- Avoid Public USSD for High-Value Tasks: Whenever possible, use a dedicated banking app over a secure, trusted Wi-Fi or a verified 4G/5G connection rather than relying solely on SMS-based communication.
- Enable Two-Factor Authentication (2FA) via Apps: Move away from SMS-based 2FA. Use authenticator apps (like Google Authenticator or Microsoft Authenticator) which are not susceptible to IMSI catcher interception.
- Update Your Device Regularly: Software updates often include patches for cellular protocol vulnerabilities.
Frequently Asked Questions
Can a rogue base station steal my photos?
Generally, no. They primarily target communication protocols like SMS, voice calls, and unencrypted data. However, if you are browsing unencrypted websites over a rogue connection, some data could be exposed.
Is it illegal to use these devices?
Yes. The use of IMSI catchers by unauthorized individuals is illegal in almost every jurisdiction globally, including Nigeria, as they interfere with licensed telecommunications infrastructure.
How can I tell if I am being targeted?
There is no single “alert” on a smartphone, but suspicious behavior like sudden battery drain, unexpected signal drops, or being unable to access 4G/5G can be warning signs.
Conclusion
As Nigeria continues its rapid digital transformation, the surface area for cyberattacks expands. Rogue base stations represent a sophisticated, invisible threat that targets the very foundation of our mobile connectivity. By understanding that nigerians need know rogue base station risks, individuals and businesses can move from a state of passive vulnerability to one of active defense. Prioritizing encrypted communication and moving away from SMS-dependent security is the most effective way to safeguard your digital life in an increasingly connected world.











Leave a Reply