



Claude Code Credential Exposure Found in 1,122 GitHub Repositories

Share
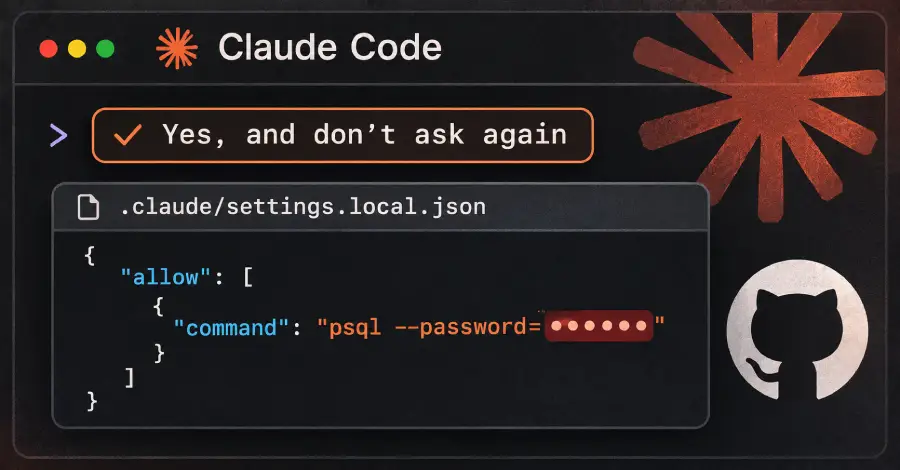
At least 1,122 public GitHub repositories have been found exposing passwords and API keys due to a configuration feature in Anthropic’s Claude Code AI assistant.
Security firm Apiiro identified the exposure, noting that the leaks occur when developers use the “Yes, and don’t ask again” option when prompted by the tool. Selecting this option instructs Claude Code to save the command exactly as it was typed into a project settings file.
If a developer includes sensitive credentials, such as an API key or a password, directly within a command, that information is recorded in plain text. When these projects are subsequently pushed to public repositories on GitHub, the credentials become visible to anyone.
This issue highlights the security risks associated with AI coding agents that automate command execution and preference logging. To mitigate this risk, developers should avoid passing secrets as command-line arguments and instead use secure methods such as environment variables or dedicated secret management systems.











Leave a Reply