



What to Do If a Bank Alert Arrives During an Unexpected Network Drop

Share
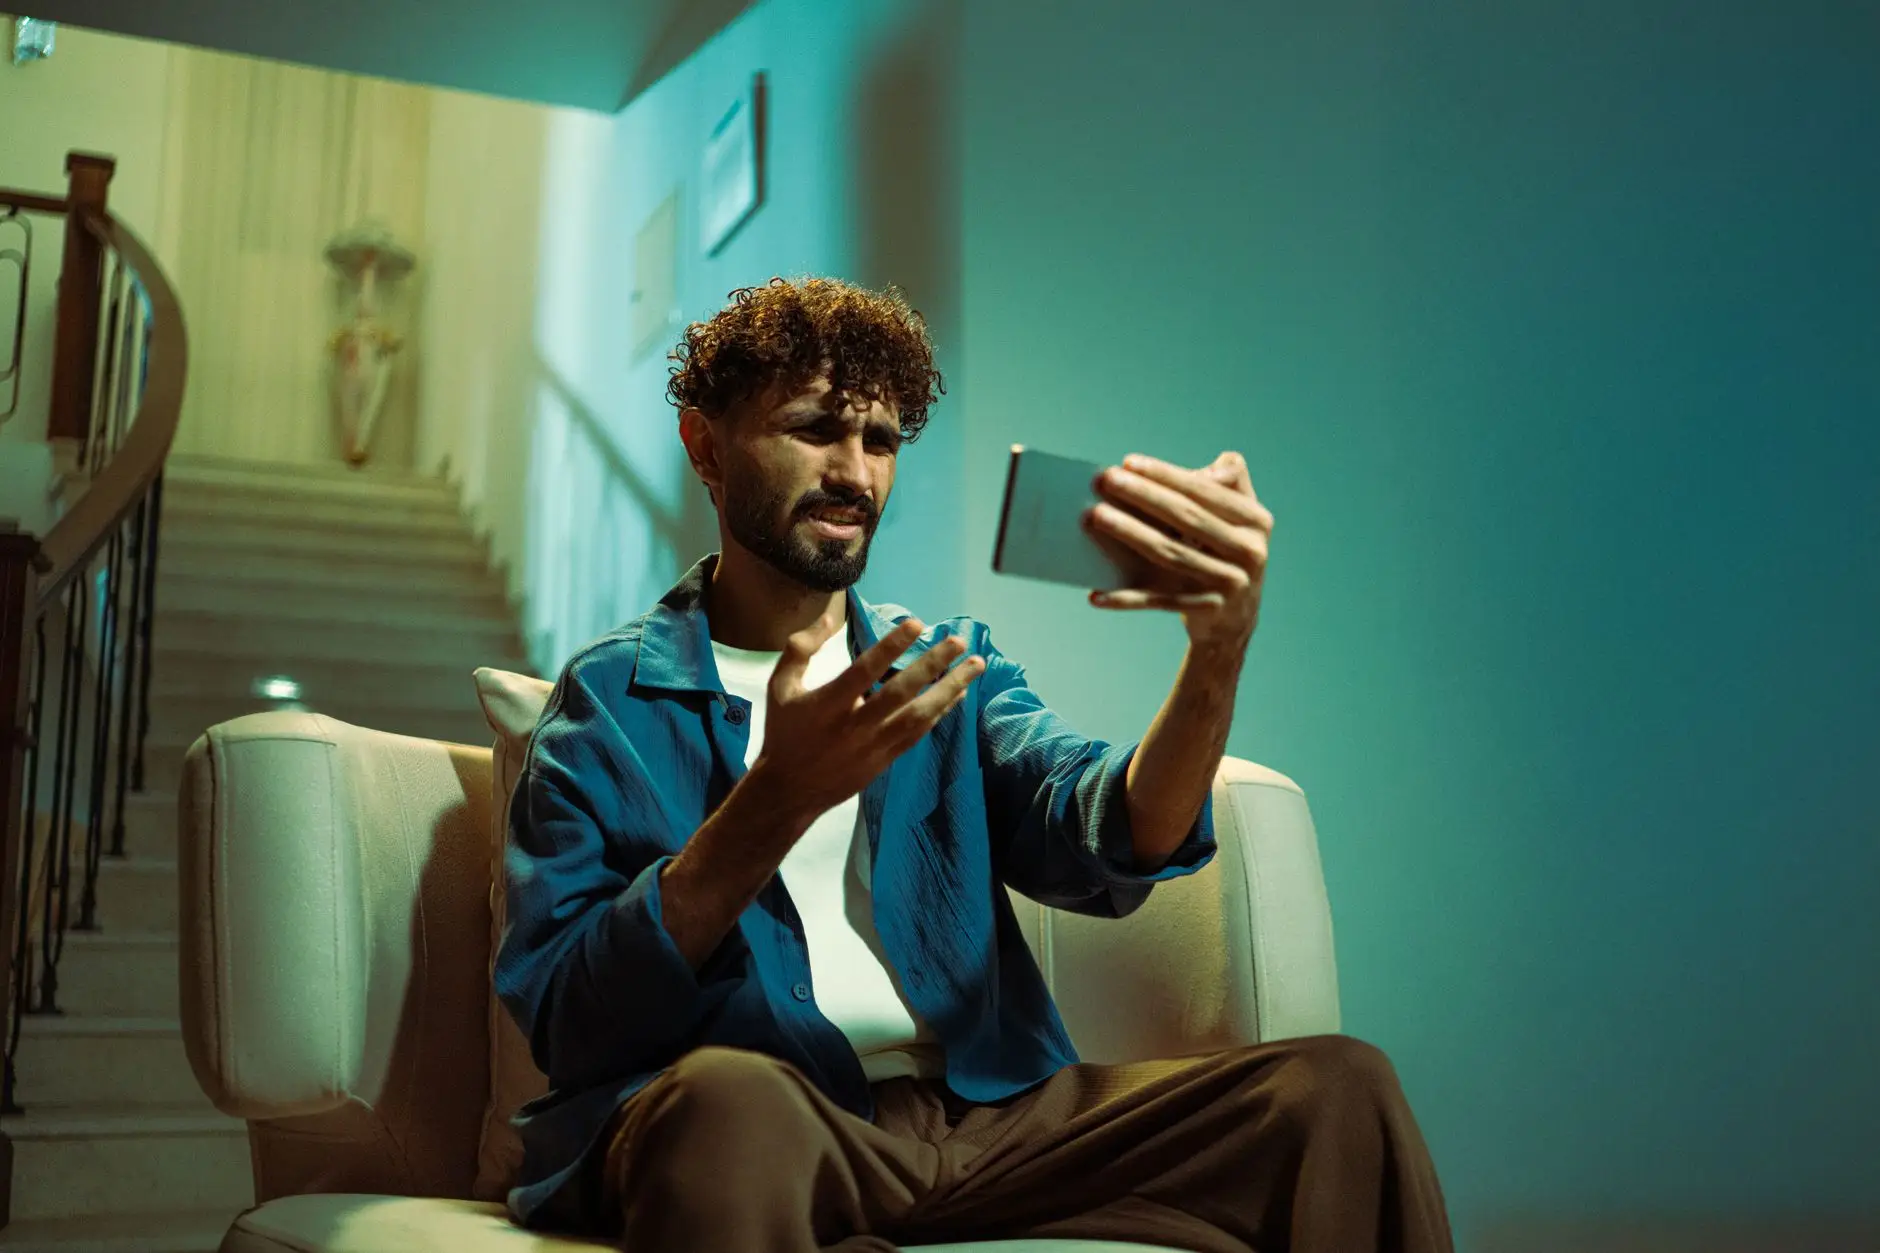
Imagine you are in the middle of a busy market in Lagos or navigating a commute in Nairobi. Your phone pings with a notification: a credit alert for a significant sum of money. Moments later, your signal bar vanishes. You have no data, no Wi-Fi, and no way to refresh your banking app to verify the transaction. In this moment of digital isolation, the psychological pressure is immense. This is not just a coincidence of poor connectivity; it is a tactical window that scammers exploit with precision.
When a bank alert arrives during unexpected network instability, the victim is placed in a state of ‘information asymmetry.’ The attacker knows something you do not, and the lack of connectivity prevents you from performing the one thing that would save you: real-time verification. This article examines how this tactic works, the psychological triggers involved, and the critical steps you must take to protect your assets.
The Convergence of Connectivity Issues and Financial Fraud
In the realm of cybersecurity, we often focus on sophisticated malware or complex breaches. However, some of the most effective attacks are rooted in social engineering—the art of manipulating human psychology. The intersection of a technical failure (the network drop) and a financial event (the alert) creates a perfect storm for fraud.
There are two ways this scenario typically manifests. In the first, the network drop is purely coincidental, but the scammer capitalizes on it. In the second, more advanced scenario, attackers may use localized signal interference or exploit known periods of network congestion to time their messages. Regardless of the cause, the goal is the same: to create a sense of urgency while removing your ability to fact-check.
As a matter of data protection, understanding that technical glitches can be weaponized is the first step toward digital resilience.
The ‘Blind Spot’ Tactic: How Scammers Exploit Network Drops
The primary objective of this tactic is to induce panic. When you receive a fake alert, the scammer’s next move is often an immediate follow-up. You might receive a call from someone claiming to be a bank official, stating that the alert was a mistake or that an unauthorized transaction is currently being processed. They will urge you to ‘reverse’ the transaction or provide an OTP (One-Time Password) to ‘stop’ the error.
Because your internet is down, you cannot log in to your official banking app to see your actual balance. This ‘blind spot’ makes you incredibly vulnerable to suggestion. You are forced to rely on the word of the person on the phone, which is exactly what the attacker wants.
A Practical Scenario: The ‘Mistaken Credit’ Trap
Consider the case of Amara, a small business owner. While processing orders, her mobile data suddenly cuts out. Simultaneously, she receives an SMS: ‘Acc: XXXX1234 Credited NGN 50,000.00.’ Before she can troubleshoot her connection, her phone rings. A man claiming to be from her bank’s fraud department says, ‘Ma’am, we sent that money to you by mistake. It was meant for another client. Please, to avoid your account being frozen, follow these steps to return it immediately.’
Amara, unable to check her app due to the network drop, feels a surge of anxiety. She fears her account will be flagged for fraud. In her haste to resolve the perceived error, she follows the instructions provided, eventually authorizing a transfer that empties her actual savings. This is a classic example of how social engineering thrives on the absence of verifiable data.
Red Flags: Distinguishing Legitimate Alerts from Scams
To protect yourself, you must learn to recognize the structural differences between a genuine communication and a fraudulent one. Even when a bank alert arrives during unexpected outages, the alert itself usually leaves clues.
| Feature | Legitimate Alert | Scam Alert |
|---|---|---|
| Sender Identity | Recognizable bank shortcode (e.g., ‘GTBank’, ‘Access’) | Random mobile number or unknown sender ID |
| Call to Action | Informational only; no immediate action required | High urgency; demands you click a link or call back |
| Request for Data | Never asks for OTP, PIN, or passwords | Frequently asks for OTPs or sensitive details |
| Link Integrity | Rarely contains clickable links in SMS | Often includes shortened or suspicious URLs |
If you encounter an alert that matches the ‘Scam Alert’ column, do not engage. Even if the network issues persist, do not let the pressure of the situation dictate your actions.
Immediate Action Steps for Individuals and Businesses
If you find yourself in this situation, follow this protocol to ensure your financial security. These steps are designed to move you from a state of reactive panic to proactive verification.
- Do Not Panic and Do Not Respond: The most important rule is to pause. Do not reply to the SMS, do not click any links, and do not provide any information to anyone calling you.
- Seek Alternative Connectivity: If your mobile data has dropped, try to find a stable Wi-Fi connection or switch to a different service provider. Your goal is to regain the ability to access your official banking channel.
- Use Official Channels Only: Once you have connectivity, do not use any phone numbers provided in the suspicious message. Instead, log in to your banking app directly or call the official customer service number found on the back of your debit card or the bank’s verified website.
- Verify via ‘Out-of-Band’ Methods: If you are a business leader managing company funds, ensure your team uses ‘out-of-band’ verification. This means confirming a transaction through a second, independent communication channel (e.g., calling a known contact via a landline if their mobile is acting strangely).
For organizations, this highlights the need for robust compliance frameworks that mandate multi-person authorization for large transfers, reducing the risk that a single panicked employee can cause a significant loss.
“The convergence of technical instability and financial urgency is a hallmark of sophisticated social engineering. Scammers don’t just hack systems; they hack the human tendency to seek resolution during chaos.”
Frequently Asked Questions
What if the bank calls me immediately after the alert?
Treat any unsolicited call following a suspicious alert with extreme caution. Even if the Caller ID looks legitimate (a tactic known as ‘spoofing’), hang up and call the bank back using the number on your official card.
Can a network drop be caused by a hacker?
While rare for an individual, targeted attacks can involve signal jamming. However, in most cases, it is a coincidental technical failure that the scammer is simply exploiting to increase your vulnerability.
Is it safe to use my bank’s mobile app during a network drop?
If your connection is intermittent, your app may fail to load or show outdated information. It is safer to wait for a stable connection before attempting to verify high-value transactions.
Conclusion
The moment a bank alert arrives during unexpected network failure, your defensive shield is at its weakest. Scammers rely on this vulnerability to bypass your logical reasoning and trigger your emotional response. By understanding the mechanics of this ‘blind spot’ tactic and adhering to a strict verification protocol, you can turn a high-risk moment into a controlled, secure interaction. Always remember: a legitimate bank will never pressure you to act urgently via an unverified channel, especially when your connectivity is compromised.
For more guidance on staying safe in the digital age, consult official resources from your local financial regulator, such as the Central Bank of Nigeria or your regional equivalent.












Leave a Reply