



Researchers Discover Log-Evading Backdoor in Control Web Panel

Share
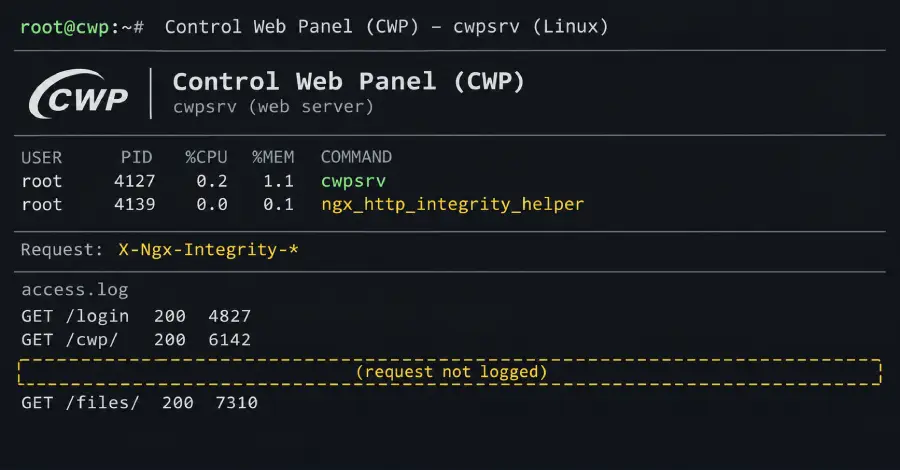
Researchers at QiAnXin’s XLab have discovered a backdoor hidden within the web server component of Control Web Panel (CWP), a management tool used for Linux hosting servers.
The backdoor enables attackers to execute remote commands by sending specifically crafted web requests. Crucially, these requests do not appear in the server’s access logs, allowing the malicious activity to remain undetected during standard log audits.
Stealthy Command Execution
Control Web Panel is a widely used free software suite that allows administrators to manage various aspects of a Linux-based hosting environment. Because the backdoor resides in the web server layer, it provides a stealthy method for maintaining persistence on a compromised host.
The findings from QiAnXin’s XLab indicate that the installation of this backdoor requires root access. This suggests that the threat actors must have already gained administrative control over the target system before they could successfully deploy the malware to facilitate further command execution.
Administrators using CWP are advised to implement rigorous monitoring for suspicious system-level changes and to ensure that root access is strictly guarded through multi-factor authentication and the principle of least privilege.












Leave a Reply