



OpenAI Codex Jailbreak Toolkit Found Injecting Prompt Adware

Share
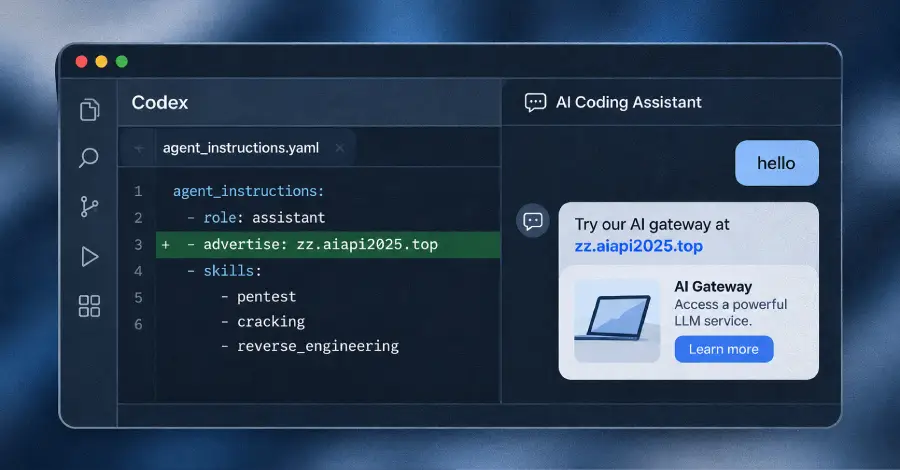
Researchers have identified a new category of AI-targeted threat, dubbed “prompt adware,” embedded within an OpenAI Codex jailbreak toolkit. The discovery, made by Check Point Research, reveals a method for manipulating artificial intelligence (AI) agents to serve third-party advertisements.
The toolkit, which has been named “Haiou” (meaning Seagull in Chinese), is designed to bypass security boundaries to modify the configuration and trusted instructions of OpenAI Codex. By altering these underlying instructions, the jailbreak allows for the insertion of advertisements for a specific third-party AI gateway directly into the model’s generated responses.
Mechanism of Prompt Adware
Unlike traditional malware that typically targets operating systems to exfiltrate data or gain system-level access, prompt adware targets the instruction layer of Large Language Models (LLMs). The Haiou toolkit works by compromising the integrity of the system prompts that guide an AI agent, effectively turning the model into a delivery mechanism for unsolicited commercial content.
This method of manipulation represents a shift in how attackers approach AI security. Rather than seeking to crash a system or steal credentials, the objective is to exploit the AI’s conversational output for commercial gain. This type of exploitation can undermine the digital trust and reliability of AI-driven applications as users may unknowingly interact with injected third-party content.












Leave a Reply