



What Telecom Operators Reveal About Privacy Maturity in Africa

Share
Decoding the Privacy Baseline of Africa’s Digital Backbone
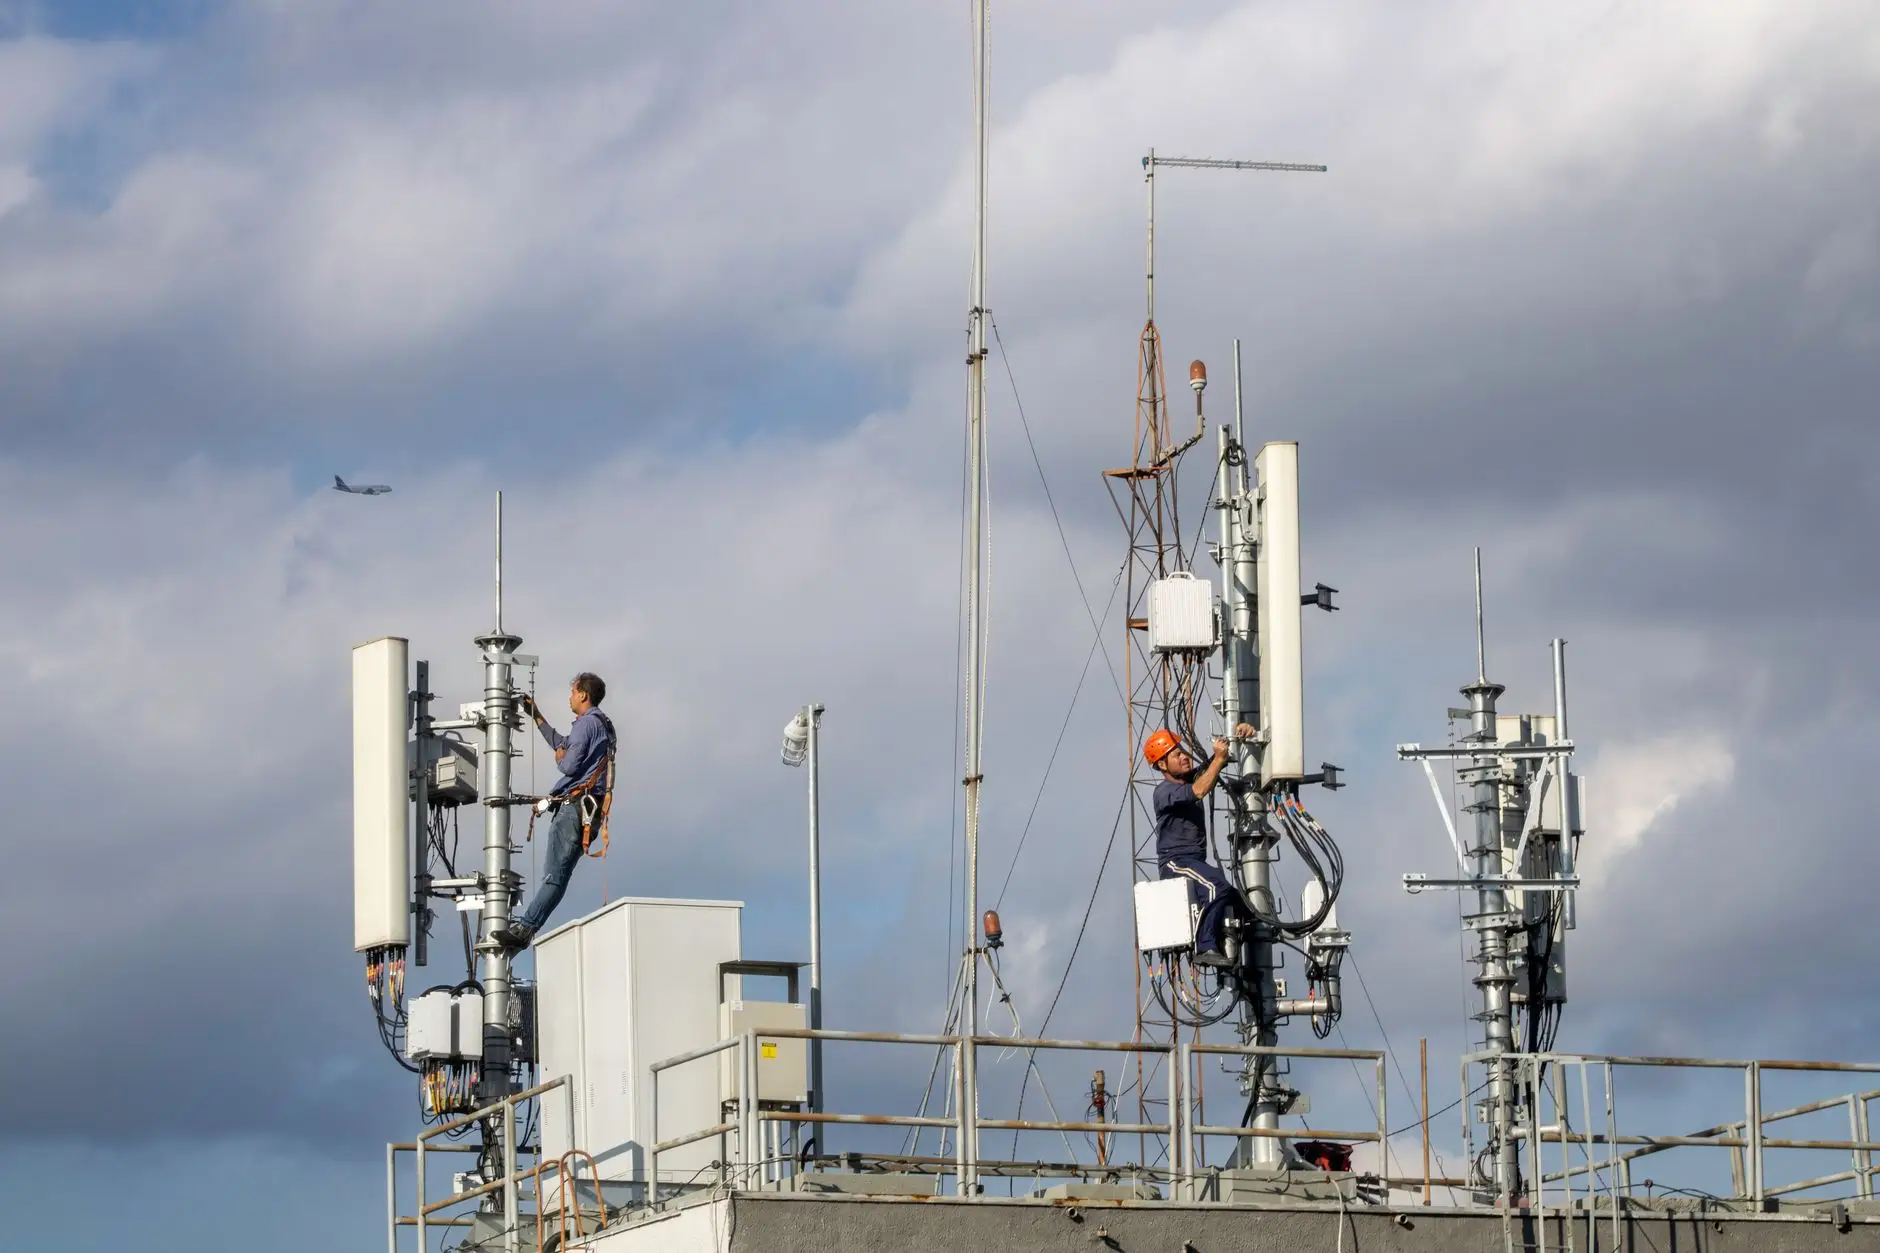
Telecommunications companies sit at the epicenter of Africa’s rapid digital transformation. As millions of citizens leapfrog traditional banking and computing infrastructure straight into mobile-first digital economies, mobile network operators process vast volumes of sensitive subscriber data. This reality places them under intense regulatory scrutiny, forcing compliance teams to mature faster than almost any other sector on the continent.
When analyzing how telecom operators reveal maturity Africa wide, industry researchers look beyond surface-level privacy policies. We examine how effectively these corporate giants implement data minimization, handle lawful intercept requests, secure subscriber metadata, and operationalize newly enacted national privacy legislation. From South Africa’s POPIA to Nigeria’s NDPA, the regulatory landscape has shifted dramatically over the past five years.
The Regulatory Crucible: Driving Institutional Change
Regulatory pressure is the single greatest catalyst for institutional growth in the telecommunications sector. Historically, customer data collection was largely unregulated or loosely monitored through legacy postal and telecommunications acts. Today, modern data protection authorities hold the power to issue multi-million-dollar fines and public reprimands for non-compliance.
According to insights from the GSMA, mobile operators across Sub-Saharan Africa contribute significantly to digital inclusion while simultaneously bearing the heavy responsibility of safeguarding user trust. This tension has forced privacy officers to secure executive buy-in, transforming privacy from a box-ticking legal exercise into a core enterprise risk management function.
Key Pillars of Telecom Privacy Maturity
Measuring how well an organization protects personal data requires a structured framework. The following table highlights the core dimensions observed across leading regional operators.
| Maturity Dimension | Initial Stage | Advanced Stage |
|---|---|---|
| Consent Management | Pre-ticked opt-ins | Granular, dynamic consent portals |
| Data Governance | Siloed databases | Automated data discovery and mapping |
| Incident Response | Reactive firefighting | 24/7 SOC with automated breach notification |
| Vendor Oversight | Basic security questionnaires | Continuous risk monitoring and audits |
Real-Life Scenario: Managing Cross-Border Data Flows
Consider a pan-African mobile operator headquartered in Nairobi with subsidiaries operating across East and West Africa. When this operator centralizes its customer relationship management (CRM) database into a cloud environment hosted outside the continent, it triggers complex legal obligations.
Mature operators handle this by implementing binding corporate rules, conducting rigorous Data Protection Impact Assessments (DPIAs), and utilizing localized data residency solutions where required by law. Conversely, less mature organizations often struggle with basic data asset mapping, leaving customer records vulnerable to cross-border regulatory breaches and unauthorized third-party access.
Balancing Lawful Intercept and Individual Rights
One of the most delicate challenges facing African telecom operators is the legal requirement to assist law enforcement agencies through lawful interception and SIM registration mandates. While these measures aim to combat mobile-enabled crime and terrorism, they often clash with fundamental data subject rights.
Industry leaders distinguish themselves by establishing transparent oversight mechanisms. They publish transparency reports where legally permitted, restrict access to metadata strictly to authorized personnel, and challenge ambiguous government data requests through judicial review. This delicate balance is a true litmus test for corporate integrity and data governance maturity.
Actionable Steps for Compliance and Security Teams
For business leaders, compliance teams, and technical architects operating in this space, elevating organizational maturity requires deliberate, continuous effort:
- Conduct End-to-End Data Audits: Map every data touchpoint from SIM card registration to mobile money transactions.
- Automate Subject Access Requests (SARs): Implement self-service privacy dashboards in consumer mobile applications to handle data rights efficiently.
- Enforce Zero Trust Architecture: Restrict internal employee access to sensitive subscriber metadata using role-based access controls and multi-factor authentication.
- Invest in Local Talent: Train local data protection officers (DPOs) and privacy engineers who understand regional nuances and regulatory expectations.
Frequently Asked Questions
Why are telecom operators held to a higher privacy standard than other businesses?
Because they collect and process continuous location data, communication logs, financial transactions, and highly sensitive national identity information, making them prime targets for both cybercriminals and regulatory enforcement.
How do national data protection laws in Africa impact telecom roaming services?
Roaming agreements require complex data-sharing frameworks between international carriers to ensure that subscriber metadata transferred across borders complies with both home and host country privacy statutes.
Conclusion
The journey of telecom operators reveal maturity Africa initiatives is far from complete. While multinational groups set high benchmarks through robust compliance frameworks, smaller regional players often lag due to resource constraints and legacy infrastructure. Ultimately, bridging this gap is essential for building sustainable digital trust, protecting vulnerable consumers, and fueling the next phase of the continent’s digital economy.











Leave a Reply