



How Policy Changes Affect Public Agencies and Citizen Trust

Share
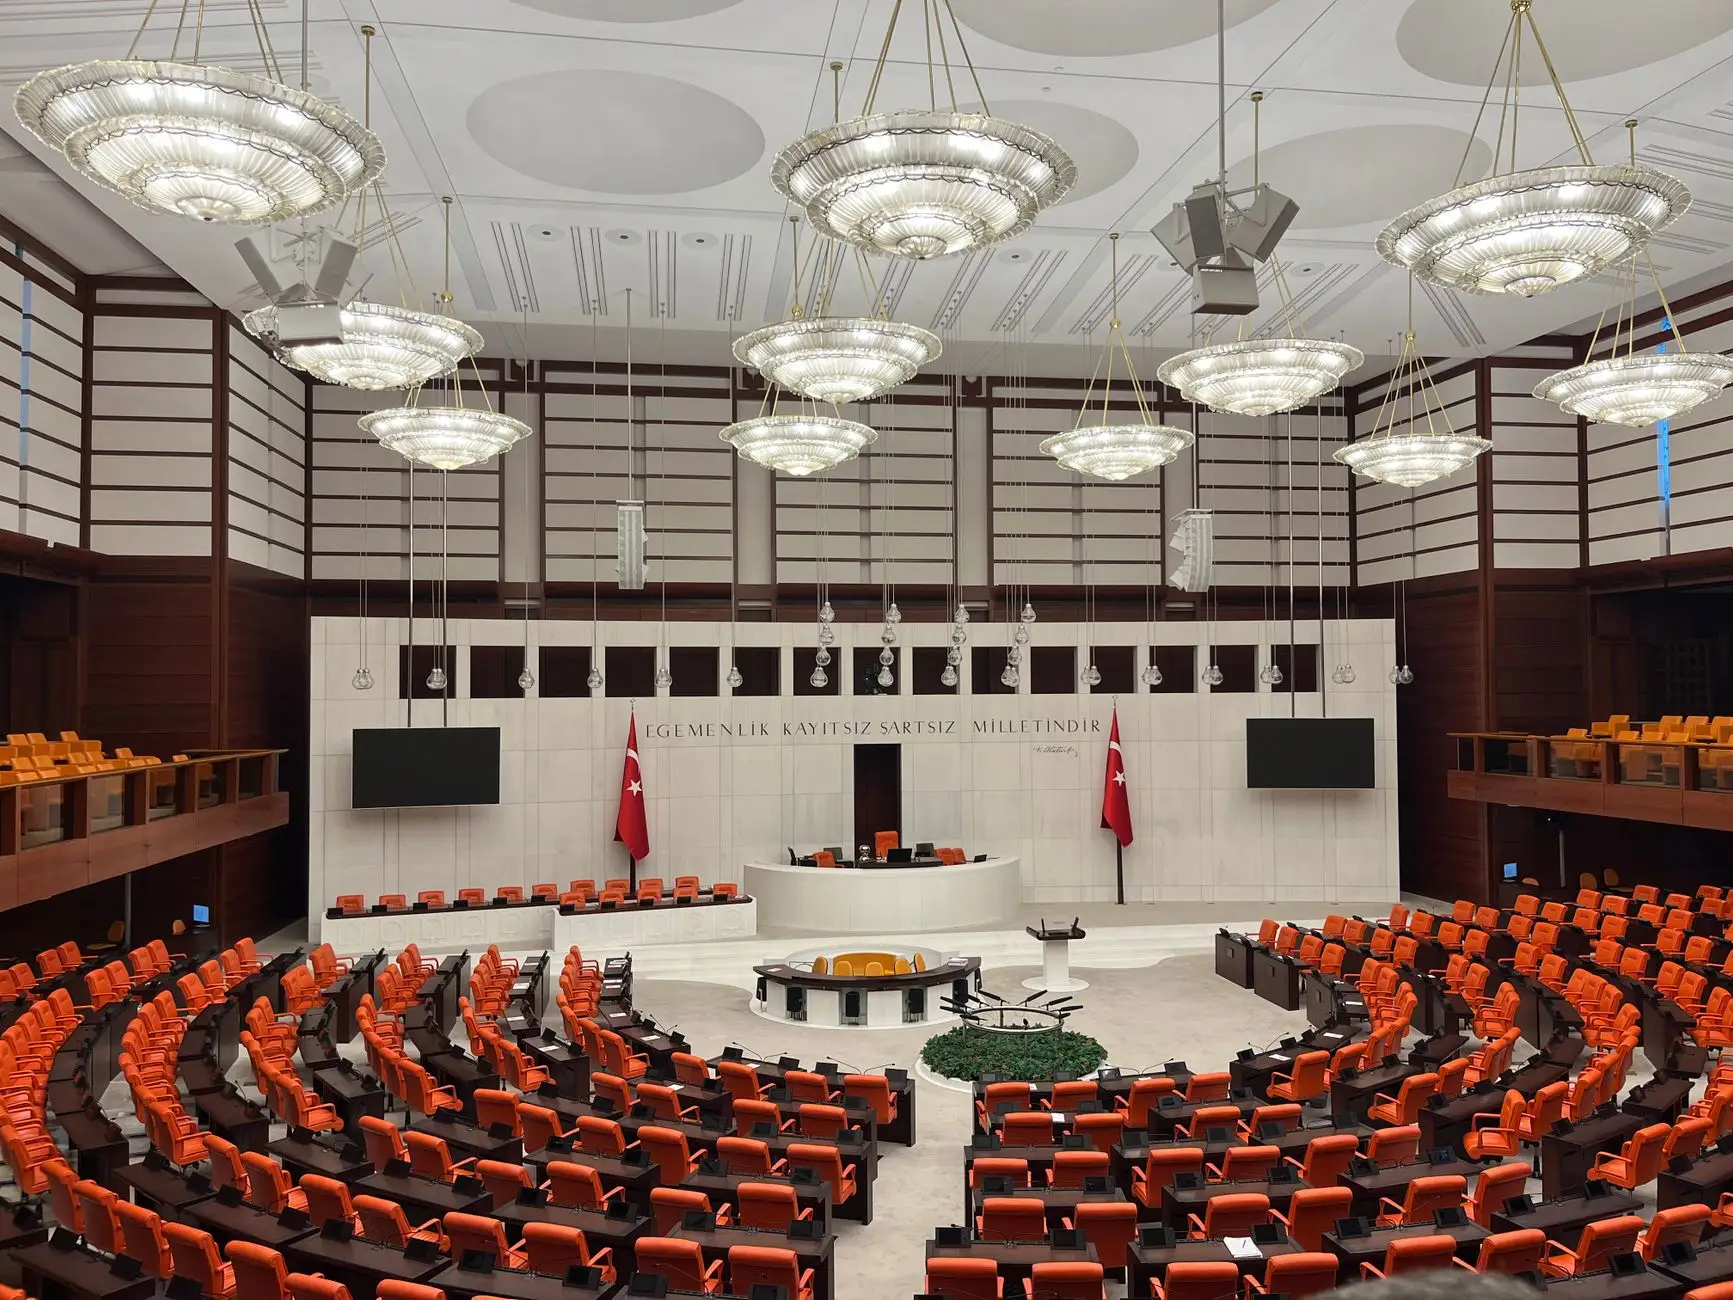
Government departments and municipal offices hold massive repositories of citizen data, ranging from tax records and health histories to public transit logs and digital IDs. When regulatory frameworks shift, public administrators cannot simply adapt overnight. They must restructure operations, rewrite data-sharing agreements, and re-engineer digital services.
Understanding how Policy Changes Affect public agencies is vital for maintaining administrative integrity and public confidence. Unlike private corporations that can sunset a product or alter terms of service unilaterally, public institutions must answer directly to elected representatives, audit boards, and the citizens they serve.
The Core Regulatory Pressures on Government Bodies
Modern data protection regulations increasingly remove the traditional exemptions that public sector entities once enjoyed. Historically, government agencies operated under broader legal allowances regarding data collection and retention. Today, legislation such as the European Union’s GDPR and various state-level US privacy laws impose strict limitations on how government bodies process citizen information.
When new mandates take effect, public institutions face immediate operational bottlenecks. According to reports from the National Institute of Standards and Technology (NIST), public sector agencies lag behind private enterprises in rapid digital compliance deployment due to legacy IT infrastructure and procurement bureaucracy.
Agencies must now evaluate every citizen interaction through the lens of data minimization, purpose limitation, and transparent consent. This creates a friction point between the desire for efficient, data driven governance and the absolute legal requirement to safeguard personal privacy.
Operational Impacts Across Municipal and Federal Levels
The ripple effects of updated regulatory policies touch nearly every department within a government structure. From local law enforcement databases to department of motor vehicles portals, procedural adaptations require careful resource allocation.
| Department | Operational Challenge | Compliance Priority |
|---|---|---|
| Law Enforcement | Balancing investigative data access with strict digital rights management | Access logging and audit trails |
| Health and Human Services | Managing sensitive medical records under multi-tier privacy statutes | Secure encryption and consent management |
| Municipal Services | Handling citizen feedback, utility payments, and housing applications | Data minimization and retention limits |
As these departments update their internal workflows, technology teams must overhaul software architectures. In many cases, policy mandates demand that public agencies offer clear mechanisms for data protection and citizen empowerment, including easy-to-use portals where residents can view, modify, or delete their submitted records.
Real-World Challenges in Public Sector Implementation
Consider a mid-sized municipal government tasked with implementing a unified citizen portal for paying utility bills, reporting potholes, and applying for building permits. Under updated data retention policies, the city can no longer store historical personal data indefinitely “just in case” it proves useful for future urban planning.
The IT department must build automated data purging routines into the database architecture. Simultaneously, the legal team must update the public-facing privacy notice, ensuring every resident understands exactly how their information flows between third-party payment processors and municipal databases. If the agency fails to update these policies or experiences a data spill, the reputational damage and regulatory fines can cripple public trust.
Managing Compliance and Building Digital Trust
To navigate shifting legal landscapes successfully, public sector leaders must take proactive steps rather than waiting for enforcement actions or audits. Effective compliance frameworks in government require cross-departmental collaboration.
- Conduct Comprehensive Data Audits: Map every data point collected, stored, and shared across municipal or agency networks.
- Upgrade Legacy Infrastructure: Replace outdated databases that lack granular access controls and audit logging capabilities.
- Train Public Servants: Ensure all employees handling citizen inquiries understand data privacy principles and confidentiality protocols.
- Enhance Transparency: Publish clear, accessible privacy notices that explain policy changes in plain language rather than legal jargon.
Public agencies exist to serve the public. When privacy policies evolve, our commitment to protecting citizen data must evolve faster than the threats against it. Transparency is no longer optional; it is the foundation of modern governance.
Frequently Asked Questions
Do public agencies have to follow the same privacy rules as private companies?
While public agencies often have specific statutory mandates or public interest exemptions, modern data protection laws increasingly hold government bodies to high accountability standards regarding citizen data rights and breach notification.
How can public agencies prepare for sudden legislative updates?
Agencies can prepare by establishing agile data governance committees, adopting scalable cloud infrastructure with built-in security controls, and conducting regular privacy impact assessments.
Conclusion
The ongoing evolution of privacy legislation signals a permanent shift in how public institutions manage information. Recognizing how Policy Changes Affect public agencies allows municipal and federal leaders to transform regulatory mandates into opportunities for better governance. By prioritizing robust data stewardship and transparent communication, public bodies can protect citizen rights while building lasting digital trust in public institutions.











Leave a Reply