

An attacker hijacked an active AI coding assistant session to deploy the Shai-Hulud worm, infecting approximately 100 internal repositories at a SaaS provider.
Government agencies have issued a joint advisory warning of CHOSEN BRICK, a Windows malware strain used by Iranian state-linked hackers to target dissidents and journalists.

KREMLIN malware uses a sophisticated technique to bypass Chromium's integrity checks, allowing it to force-install malicious browser extensions that steal session tokens and credentials.
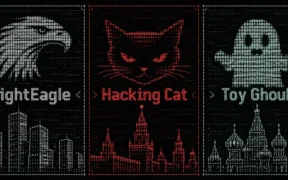
Kaspersky has identified three distinct threat clusters—NightEagle, Hacking Cat, and Toy Ghouls—carrying out diverse cyberattacks against Russian enterprises, ranging from backdoor deployments to destructive wiper malware.
Chinese threat actors are exploiting a sophisticated zero-day chain in Google Chrome and Microsoft Windows to deploy the GRIMWEDGE backdoor against non-governmental organisations.











