

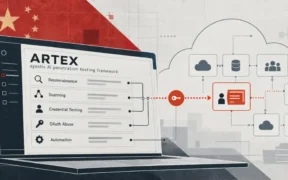
Microsoft has attributed a supply chain attack on ConnectWise Cloud Backup to the China-linked actor Storm-0940, who utilised the ARTEX AI agentic framework to accelerate the intrusion.
ConnectWise has suspended several cloud services while investigating unauthorized access to client Microsoft 365 environments, which reportedly involved the misuse of application tokens.
ConnectWise has released an urgent patch for a critical ScreenConnect vulnerability that allows unauthorised file execution during active remote sessions.













