



What the NDPC Means for healthcare providers Handling Personal Data

Share
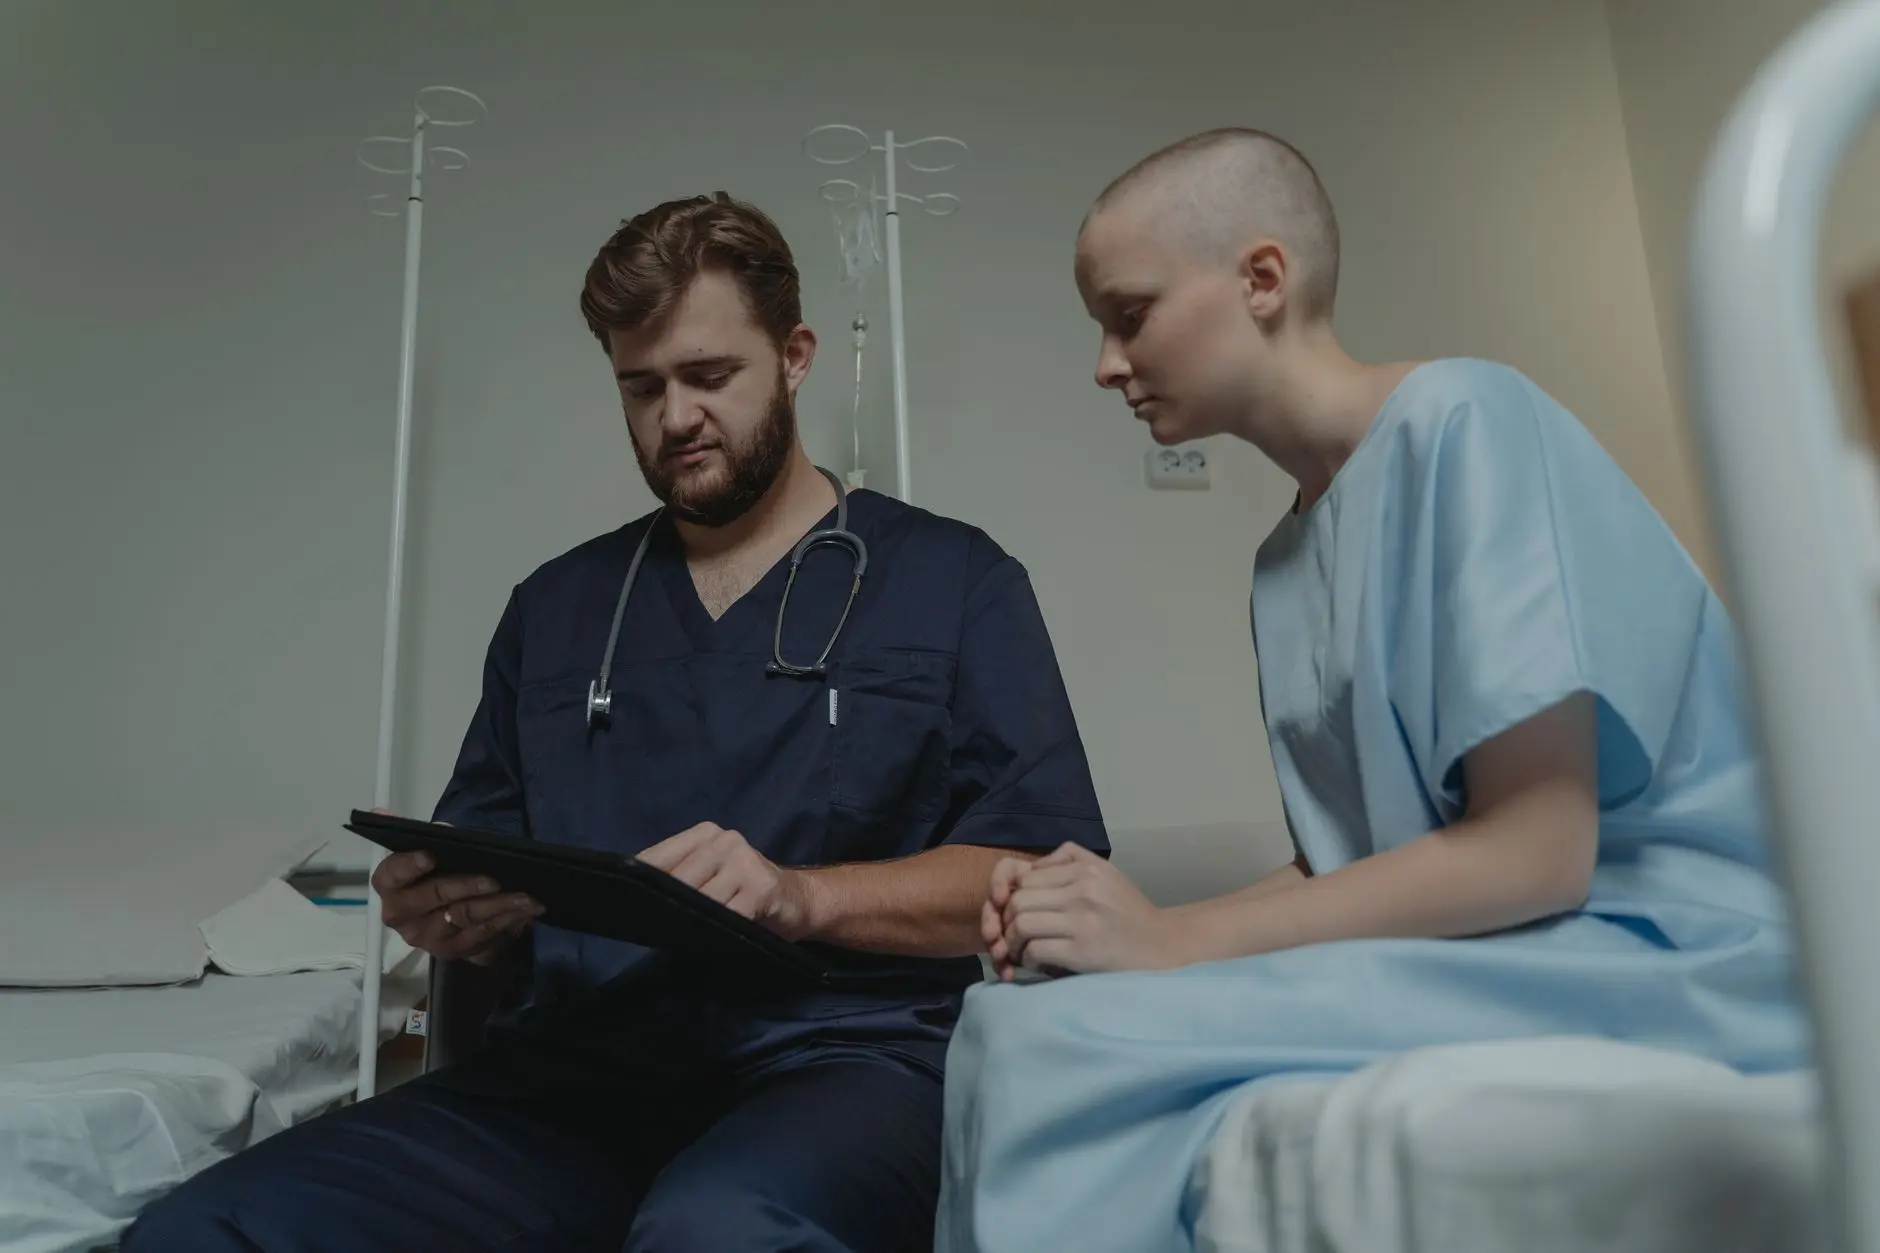
Introduction to Healthcare Data Regulation
Medical institutions process some of the most sensitive personal records in existence. From diagnostic histories to genetic profiles, patient data represents a prime target for misuse or unauthorized access. In Nigeria, the Nigeria Data Protection Commission (NDPC) regulates how organizations handle this sensitive information. Understanding what the NDPC Means for healthcare providers Handling Personal data is no longer optional for clinics, hospitals, and digital health startups. It is an operational necessity that directly impacts clinical trust and legal standing.
Regulatory frameworks have shifted from basic administrative guidelines to strict, enforceable mandates. Under the Nigeria Data Protection Act (NDPA), the NDPC holds the authority to investigate data processing practices, issue financial penalties for non-compliance, and audit medical facilities. For hospital administrators, doctors, and health tech founders, building robust data governance protocols is the only way to safeguard patient trust and avoid regulatory sanctions.
The Core Mandates of the NDPC for Medical Facilities
Healthcare providers collect patient names, phone numbers, payment details, and deeply personal health records every single day. Under the oversight of the NDPC, this information falls under the category of sensitive personal data, which requires a higher standard of care. Facilities must establish lawful bases for processing this data, typically relying on explicit patient consent or vital medical necessity.
Furthermore, the Commission enforces the principle of data minimization. Clinics should only collect information that is strictly necessary for medical diagnosis or administrative processing. Hoarding historical patient charts without a valid retention schedule increases the surface area for a potential data leak. Compliance teams must review intake forms and digital databases to ensure they align with these statutory boundaries.
Practical Implications for Digital Health and Records Management
The modern healthcare ecosystem relies heavily on Electronic Health Records (EHRs) and telemedicine platforms. While these technologies improve patient outcomes, they also introduce complex cybersecurity risks. When examining what the NDPC Means for healthcare providers Handling Personal data, it becomes clear that technical safeguards must match administrative policies. Encryption at rest and in transit, multi-factor authentication, and strict access control lists are baseline expectations for any system housing patient files.
“Data privacy in healthcare is not merely a legal checkbox; it is a fundamental extension of the medical oath to do no harm.” – Dr. Vincent Olatunji, NDPC National Commissioner.
Consider a medium-sized private hospital that outsources its billing and patient database management to a third-party vendor. Under NDPC guidelines, the hospital remains accountable for how that vendor processes patient information. Healthcare executives must implement rigorous vendor due diligence, ensuring data processing agreements include strict security and confidentiality clauses.
Compliance Checklist for Healthcare Institutions
Navigating regulatory audits requires structured preparation. Medical facilities should evaluate their internal operations against established data protection standards to identify vulnerabilities before regulators intervene.
- Conduct a Data Protection Impact Assessment (DPIA): Regularly evaluate high-risk processing activities, such as genetic testing or large-scale patient profiling.
- Appoint a Qualified Data Protection Officer (DPO): Ensure a trained professional oversees compliance efforts and acts as the liaison to the regulatory authority.
- Update Privacy Notices: Inform patients clearly about why their data is collected, how it is stored, and who has access to it.
- Establish Incident Response Plans: Create clear protocols for detecting, containing, and reporting data breaches within statutory timeframes.
Comparing Traditional Records vs. Digital Health Standards
Healthcare delivery has evolved rapidly over the past decade, shifting from paper-based filing systems to cloud-native patient portals. The table below outlines how regulatory expectations differ across operational models.
| Operational Feature | Traditional Paper Records | Modern Digital Health Systems |
|---|---|---|
| Storage Medium | Physical filing cabinets in locked rooms | Cloud servers and encrypted databases |
| Access Control | Manual key management and visitor logs | Role-based permissions and digital audit trails |
| Risk Vector | Physical theft, fire, or unauthorized manual viewing | Cyberattacks, ransomware, and insider data leaks |
| NDPC Oversight | Applies to physical record retention and disposal | Applies fully to automated processing, apps, and APIs |
Handling Patient Rights and Data Subject Requests
A crucial aspect of what the NDPC Means for healthcare providers Handling Personal data involves respecting the rights of patients. Individuals retain the right to access their medical records, request corrections to inaccurate diagnostic details, and, in certain circumstances, object to the processing of their information. Medical practices must establish transparent, efficient channels allowing patients to exercise these rights without unnecessary bureaucratic hurdles.
While patient consent is central to data processing, clinicians must note that withholding certain medical data requests required for ongoing treatment can complicate patient care. Striking the right balance between clinical autonomy and patient rights requires ongoing staff training and well-documented privacy policies.
Frequently Asked Questions
Do small clinics need to comply with NDPC regulations?
Yes. The NDPA applies to any entity processing personal data within Nigeria or targeting Nigerian residents, regardless of the organization’s physical size or staff count.
What happens if a hospital suffers a data breach?
Healthcare providers must notify the NDPC and affected data subjects promptly following a confirmed security incident, detailing the scope of the breach and mitigation steps taken.
Can patients request the total deletion of their medical history?
While the right to erasure exists, exceptions apply when retaining medical records is required by law, public health interests, or ongoing clinical necessity.
Conclusion
The regulatory environment surrounding medical information continues to mature. Understanding what the NDPC Means for healthcare providers Handling Personal data empowers medical leaders to transition from reactive compliance to proactive digital stewardship. By prioritizing robust technical security, transparent patient communication, and regular staff training, healthcare institutions can protect vulnerable populations while fostering long-term trust in modern medical innovation.








Leave a Reply