



A Step-by-Step Guide to Managing Health Data Responsibly

Share
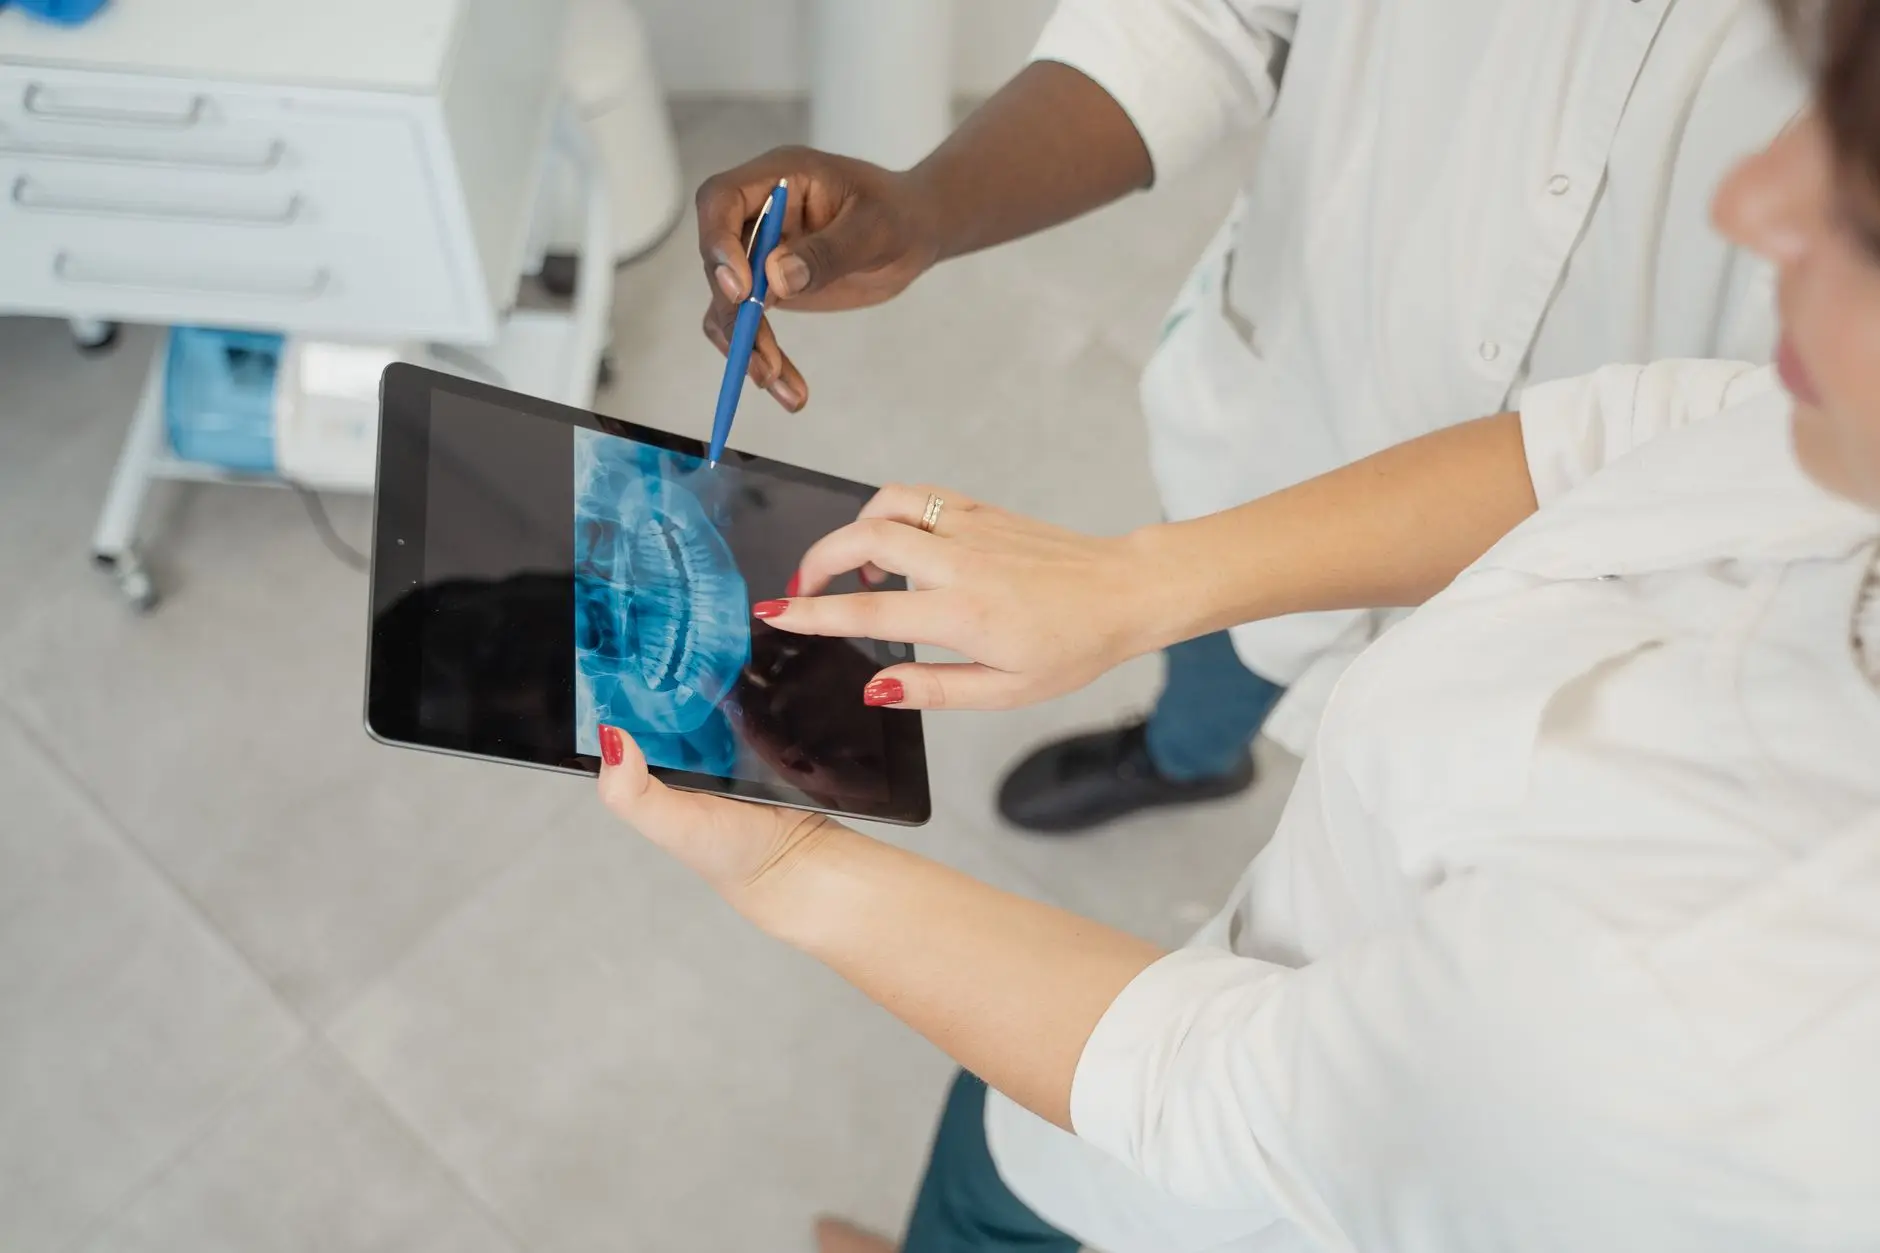
Health data is uniquely sensitive, encompassing deeply personal information that, if misused or exposed, can lead to discrimination, financial harm, reputational damage, and a profound erosion of trust. In our increasingly digitized world, where health records, wearable device data, and telehealth consultations are common, the challenge of protecting this information is escalating. For businesses, healthcare providers, and technology developers alike, managing health data responsibly is not just a regulatory mandate but an ethical imperative.
This guide offers a practical, step-by-step framework for organizations and individuals to navigate the complexities of health data management, ensuring compliance with global privacy laws while fostering a culture of digital trust and safety.
Understanding the Unique Sensitivity of Health Data
Before diving into the steps, it is crucial to recognize what makes health data distinct. Unlike other forms of personal data, health information can reveal an individual’s most vulnerable states, past conditions, genetic predispositions, and future risks. This sensitivity mandates stricter protection and careful consideration of how it is collected, stored, processed, and shared. Regulations like the Health Insurance Portability and Accountability Act (HIPAA) in the U.S., the General Data Protection Regulation (GDPR) in Europe, and numerous national privacy laws globally impose stringent requirements due to this inherent sensitivity.
"Medical data is highly sensitive and requires the utmost protection, as its misuse can have serious implications for individuals’ lives and privacy." — Andrea Jelinek, former Chair of the European Data Protection Board (EDPB)
A Step-by-Step Approach to Managing Health Data Responsibly
Step 1: Establish a Robust Legal and Ethical Framework
Begin by thoroughly identifying all applicable privacy laws and regulations relevant to your specific context and geographical reach. This includes national, regional, and sector-specific legislation. Develop internal privacy policies and procedures that reflect these legal requirements and go further to address ethical considerations in data handling.
- Action: Conduct a legal audit to map all relevant data protection laws.
- Action: Draft or update internal privacy policies, data retention schedules, and acceptable use policies.
Step 2: Implement Granular Consent and Transparency
For most health data processing, especially outside direct medical treatment purposes, explicit and informed consent is paramount. Individuals must understand precisely what data is being collected, why, how it will be used, with whom it will be shared, and for how long. Consent should be freely given, specific, informed, and unambiguous.
- Action: Design clear, concise, and accessible privacy notices.
- Action: Implement mechanisms for obtaining granular consent, allowing individuals to opt-in or out of specific data uses.
Step 3: Secure Data at Every Stage
Robust cybersecurity measures are fundamental to preventing unauthorized access, breaches, and data loss. This involves technical, physical, and administrative safeguards across the data lifecycle, from collection to deletion. Organizations should prioritize securing their infrastructure and systems. For a deeper dive into foundational protection strategies, visit our data protection section.
- Action: Employ encryption for data at rest and in transit.
- Action: Implement strong access controls, multi-factor authentication (MFA), and regular security audits.
- Action: Ensure physical security of data storage facilities and devices.
Step 4: Practice Data Minimization and Purpose Limitation
Adhere to the principles of data minimization and purpose limitation. Only collect the health data that is absolutely necessary for the stated purpose, and do not process it for purposes incompatible with the original collection unless new consent is obtained or a clear legal basis exists.
- Action: Regularly review data collection forms and processes to ensure only essential data is gathered.
- Action: Define clear purposes for all data processing activities and document them.
Step 5: Govern Access and Sharing Rigorously
Limit access to health data on a "need-to-know" basis. Any sharing of health data with third parties—whether for research, analytics, or service provision—must be governed by robust data processing agreements (DPAs) or business associate agreements (BAAs) that mandate equivalent levels of protection.
- Action: Implement strict user access management systems.
- Action: Vet all third-party vendors and ensure comprehensive contracts are in place regarding data handling.
Step 6: Uphold Data Subject Rights
Individuals have fundamental rights concerning their health data, including the right to access, rectify, erase, and port their information, as well as to object to certain processing activities. Organizations must establish clear, efficient processes to facilitate these requests in a timely manner. Adherence to these rights is a core aspect of compliance with global privacy frameworks.
- Action: Develop clear procedures for handling Data Subject Access Requests (DSARs) and other privacy rights requests.
- Action: Train staff on how to recognize and escalate such requests.
Step 7: Prepare for and Respond to Incidents
Data breaches involving health information can be particularly damaging. A proactive incident response plan is critical. This plan should detail steps for detection, containment, investigation, notification, and recovery.
Real-life Example: Imagine a small digital health startup, "WellnessTrack," developing an AI-powered fitness app that collects user heart rate and activity data. One day, a misconfigured server exposes a database containing thousands of user IDs linked to their daily heart rate logs. WellnessTrack’s pre-existing incident response plan, developed in line with privacy regulations, immediately kicks in. They isolate the server, engage forensic experts, and within 72 hours, notify affected users and relevant data protection authorities, outlining steps taken to mitigate harm. This prompt, transparent response, although challenging, minimized regulatory fines and preserved user trust to a greater extent than if they had no plan.
The financial ramifications of such incidents are significant. The IBM Cost of a Data Breach Report consistently highlights the healthcare industry as having the highest average cost of a data breach, reaching approximately $11 million in 2023.
- Action: Develop and regularly test an incident response plan.
- Action: Understand and comply with all breach notification requirements.
Step 8: Foster a Culture of Privacy Through Training
Technology and policies alone are insufficient without a privacy-aware workforce. Regular, mandatory training for all employees who handle health data is essential to instill best practices and reinforce the importance of data protection.
- Action: Implement ongoing privacy and security awareness training for all staff, tailored to their roles.
- Action: Encourage a "privacy-first" mindset across the organization.
Step 9: Conduct Regular Audits and Impact Assessments
Responsible health data management is not a static state but an ongoing process. Regular audits, Data Protection Impact Assessments (DPIAs), and privacy assessments are crucial to identify and mitigate new risks, ensure continued compliance, and adapt to evolving threats and regulations.
- Action: Schedule regular internal and external audits of data processing activities.
- Action: Conduct DPIAs for new projects or technologies involving health data.
| Pillar of Responsible Health Data Management | Key Actions |
|---|---|
| Legal & Ethical Foundation | Identify applicable laws, establish comprehensive policies. |
| Consent & Transparency | Obtain explicit, informed consent; provide clear privacy notices. |
| Security Measures | Encrypt data, implement access controls, conduct audits. |
| Data Minimization & Purpose | Collect only necessary data; define and adhere to processing purposes. |
| Access & Sharing Governance | Apply "need-to-know"; secure data sharing agreements. |
| Data Subject Rights | Facilitate access, rectification, erasure, and portability requests. |
| Incident Preparedness | Develop and test response plans; comply with notification laws. |
| Training & Culture | Provide ongoing privacy and security awareness training. |
| Audits & Assessments | Conduct regular DPIAs and compliance audits. |
FAQ: Managing Health Data Responsibly
What are the biggest risks of poor health data management?
The risks include data breaches leading to identity theft or fraud, regulatory fines and penalties, reputational damage, loss of patient trust, legal action, and potential harm to individuals whose sensitive information is exposed or misused.
How often should our health data privacy policies be reviewed?
Health data privacy policies should be reviewed at least annually, or more frequently if there are significant changes in technology, legal regulations, business operations, or identified risks.
Does this guide apply to small clinics as well as large hospitals?
Yes, absolutely. The principles and steps outlined apply to any entity, regardless of size, that collects, processes, or stores health data. While the scale of implementation may vary, the fundamental obligations to protect sensitive information remain consistent.
Conclusion
Effectively managing health data responsibly is a complex, continuous journey, demanding vigilance, expertise, and a commitment to ethical practices. By following this step-by-step guide, organizations can build robust frameworks that not only meet regulatory obligations but also foster invaluable trust with individuals whose most sensitive information they hold. In an age where digital health is rapidly expanding, proactive data stewardship is not merely a compliance task; it is the cornerstone of patient care, digital innovation, and collective well-being.











Leave a Reply