



Secure Your Sales: A Step-by-Step Guide to Managing Payment Data Responsibly

Share
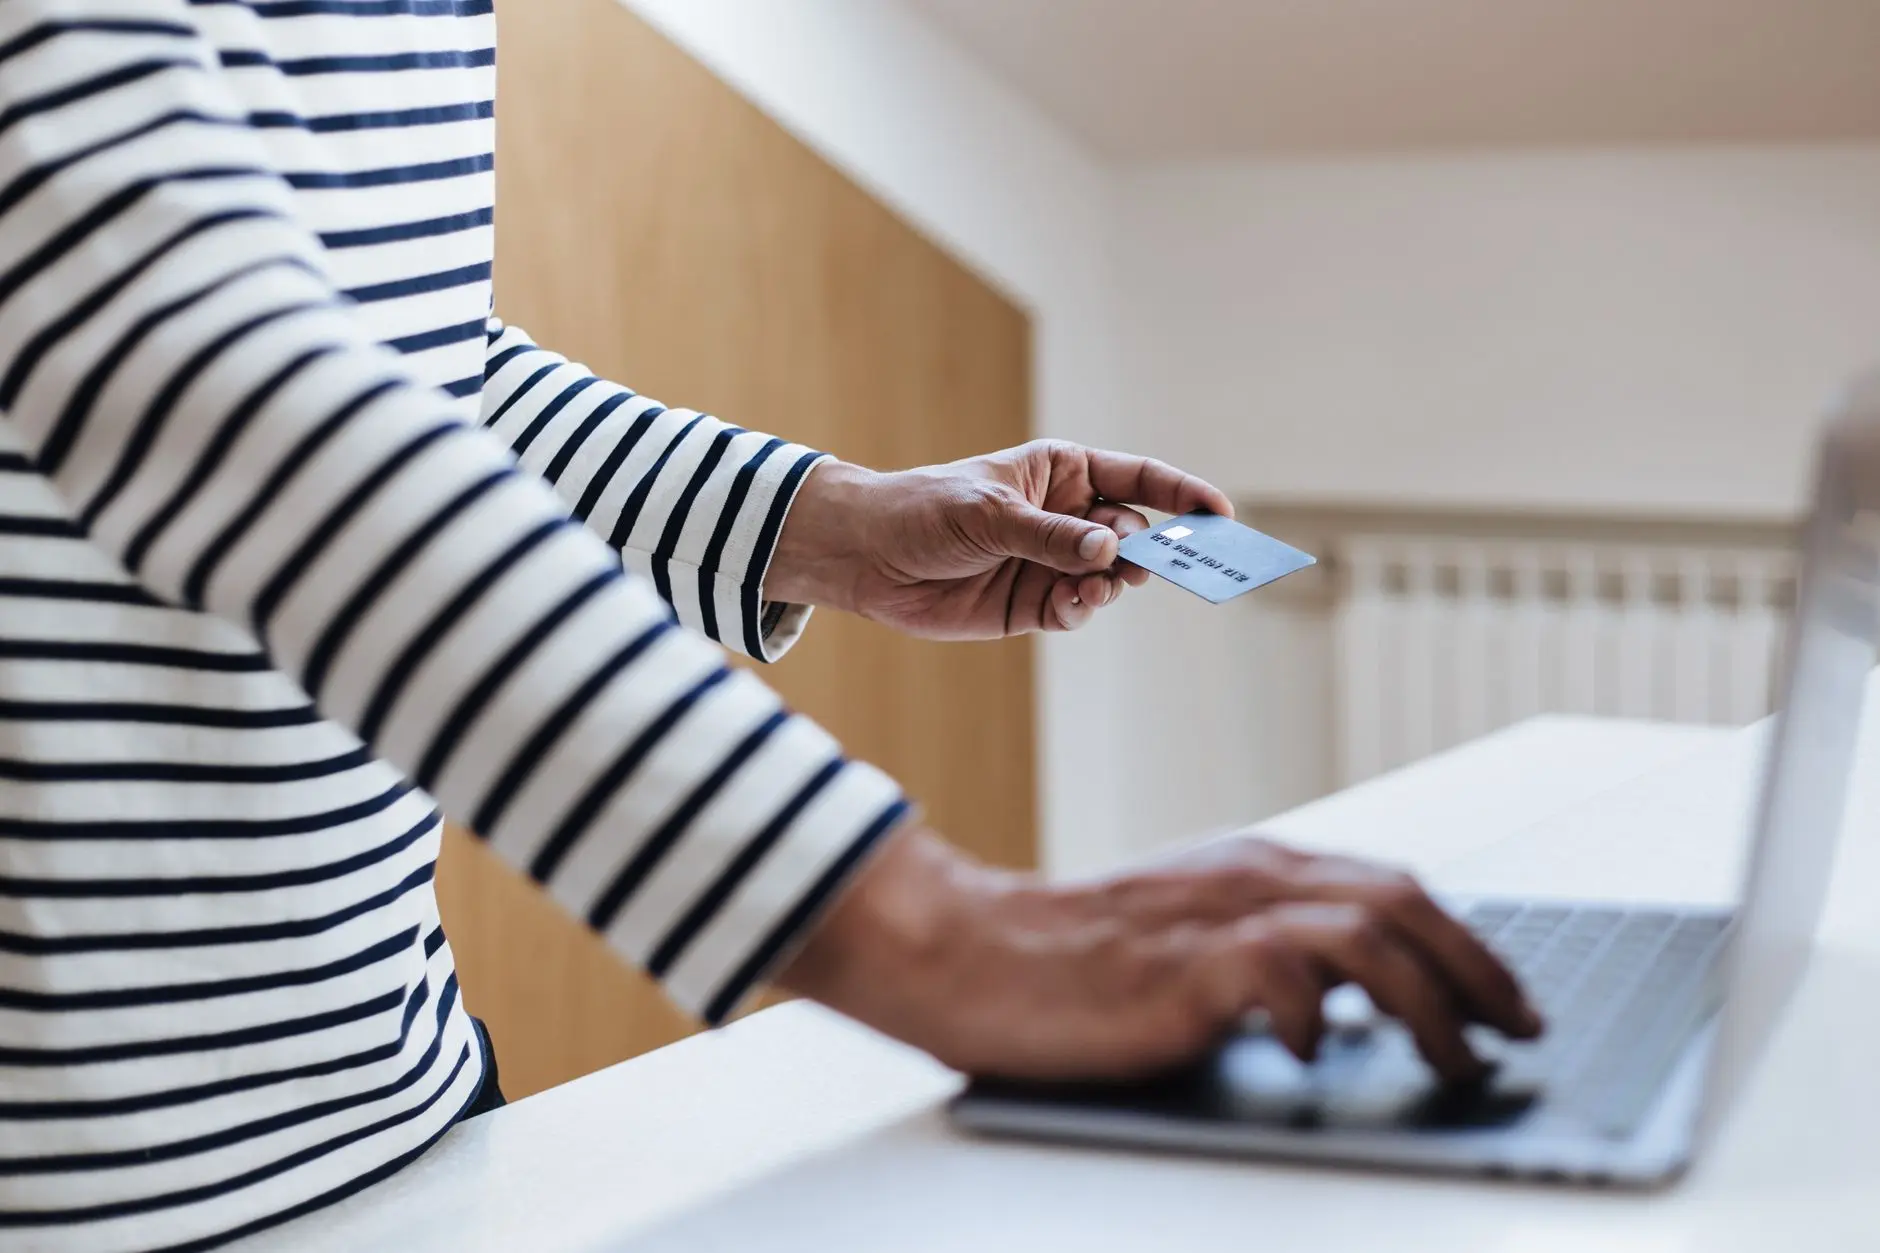
In today’s digital economy, businesses of all sizes routinely handle sensitive payment information. From processing credit card transactions to managing digital wallets, the flow of payment data is constant. However, with great convenience comes immense responsibility. Mishandling this data doesn’t just risk financial penalties; it shatters customer trust, damages reputation, and can lead to severe legal repercussions. For business leaders, privacy professionals, and technology teams alike, understanding how to manage payment data responsibly is no longer optional—it’s foundational to long-term success and digital trust.
This guide provides a comprehensive, step-by-step approach to help your organization safeguard payment data effectively, ensuring compliance and reinforcing your commitment to customer privacy.
The Weight of Trust: Why Responsible Payment Data Management Matters
Payment data is uniquely sensitive. It directly links to individuals’ financial well-being and identity. When compromised, the fallout can include fraudulent transactions, identity theft, and significant emotional distress for those affected. For businesses, a payment data breach can result in:
- Hefty fines and penalties from regulatory bodies (e.g., PCI DSS, GDPR).
- Lawsuits from affected customers.
- Loss of merchant processing capabilities.
- Irreparable damage to brand reputation and customer loyalty.
- Significant operational costs for incident response, forensics, and remediation.
The IBM Cost of a Data Breach Report consistently highlights that breaches involving customer Personally Identifiable Information (PII), including payment data, are among the most expensive types of incidents. Protecting this data is an investment in your business’s future.
Understanding Your Payment Data Landscape
Before you can protect payment data, you must understand what you have, where it lives, and how it moves. This foundational step is critical for developing an effective strategy for managing payment data responsibly.
Step 1: Map Your Data Flow and Identify Sensitive Information
Begin by creating a comprehensive inventory of all payment data your organization collects, stores, processes, and transmits. This involves:
- Identifying Data Types: What specific payment details do you handle (e.g., full credit card numbers, cardholder names, expiration dates, CVVs, bank account numbers, tokenized data)?
- Locating Data Storage: Where is this data stored? On your servers, cloud services, third-party payment gateways, point-of-sale (POS) systems, physical receipts?
- Tracing Data Movement: How does payment data flow through your systems? From customer input to payment processor, to bank, to internal accounting. Who has access at each stage?
- Identifying Data Lifecycles: How long is data retained? When is it securely disposed of?
By mapping your data flow, you identify critical points of vulnerability and areas where data is most exposed, allowing you to prioritize security efforts.
Implementing Robust Security and Compliance
Step 2: Implement Robust Security Measures
Once you understand your data landscape, it’s time to fortify your defenses. Effective security measures are multi-layered:
- Encryption: Encrypt payment data both in transit (using TLS/SSL protocols) and at rest (when stored on servers, databases, or devices). This renders data unreadable to unauthorized parties even if they gain access.
- Access Controls: Enforce the principle of least privilege. Grant access to payment data only to those individuals and systems that absolutely require it to perform their job functions. Implement strong, unique passwords and Multi-Factor Authentication (MFA) for all access points.
- Network Segmentation: Isolate systems that handle payment data from the rest of your network. This limits the scope of a breach if one occurs elsewhere in your infrastructure.
- Tokenization & Anonymization: Wherever possible, replace sensitive payment data with non-sensitive substitutes (tokens) or anonymized identifiers. This significantly reduces the risk if your systems are compromised.
- Regular Vulnerability Assessments and Penetration Testing: Proactively identify and fix security weaknesses in your systems, applications, and network infrastructure.
Step 3: Ensure Compliance with Industry Standards and Regulations
Compliance is non-negotiable when dealing with payment data. The primary standard for card payments is PCI DSS.
"Maintaining compliance is not a one-time event, but an ongoing process that is critical to protecting payment card data and maintaining consumer trust." – PCI Security Standards Council
Key compliance considerations include:
- PCI Data Security Standard (PCI DSS): If you accept credit card payments, adherence to PCI DSS is mandatory. This standard sets forth requirements for security management, policies, procedures, network architecture, software design, and other critical protective measures. The PCI Security Standards Council provides detailed guidelines.
- Data Protection Regulations: Depending on where your customers are located, you must also comply with broader data protection laws like the EU’s GDPR, California’s CCPA/CPRA, or other national privacy laws. These often dictate how you obtain consent, how long you retain data, and how you respond to data subject rights requests.
- Vendor Due Diligence: If you use third-party payment processors or other vendors who handle payment data, ensure they are also compliant with relevant standards and regulations. Your liability doesn’t end with outsourcing.
Adopting robust compliance frameworks safeguards your organization against legal and financial penalties.
Step 4: Train Your Team and Foster a Security-First Culture
The human element remains the weakest link in many security chains. Your employees are your first line of defense:
- Ongoing Training: Educate all employees who interact with payment data on security best practices, company policies, and the latest threats (e.g., phishing, social engineering).
- Policy Enforcement: Develop clear, concise policies for handling, storing, and disposing of payment data. Ensure these policies are regularly reviewed and enforced.
- Incident Reporting: Empower employees to recognize and report suspicious activities without fear of reprisal.
Proactive Measures and Continuous Improvement
Step 5: Plan for Incident Response and Business Continuity
Despite your best efforts, breaches can happen. A well-defined incident response plan is crucial:
- Preparation: Develop a detailed plan outlining steps to take immediately following a suspected breach, including roles, responsibilities, and communication protocols.
- Detection & Analysis: Implement systems for prompt detection of security incidents and conduct thorough analysis to understand the scope and impact.
- Containment & Eradication: Act quickly to isolate affected systems, prevent further data loss, and remove the threat.
- Recovery & Post-Incident Review: Restore affected systems and data, and conduct a comprehensive review to identify lessons learned and improve future security.
Step 6: Regularly Audit and Update Your Practices
The threat landscape is constantly evolving. What was secure yesterday may not be secure tomorrow:
- Periodic Audits: Conduct internal and external audits of your payment data security practices, systems, and compliance posture.
- Technology Updates: Keep all software, operating systems, and security tools (antivirus, firewalls) up to date with the latest patches.
- Policy Reviews: Regularly review and update your payment data handling policies to reflect new threats, technologies, and regulatory changes.
Real-Life Scenario: The Small Business Data Breach
Consider "Petal & Pot," a thriving online plant nursery. They processed payments directly through their e-commerce platform. Initially, they hadn’t segmented their network, stored full credit card numbers for repeat customers, and relied on basic password protection for their administrative portal. An employee fell for a sophisticated phishing scam, inadvertently giving attackers access to the administrative system. Because the payment data wasn’t encrypted at rest and network segmentation was absent, the attackers quickly moved laterally, exfiltrating customer credit card details. The breach led to Petal & Pot losing their merchant account, facing regulatory fines for PCI DSS non-compliance, and experiencing a dramatic drop in customer confidence and sales. Their lack of proactive measures for managing payment data responsibly nearly put them out of business.
Practical Checklist for Responsible Payment Data Management
| Action Item | Description | Frequency |
|---|---|---|
| Map Data Flow | Document all payment data collection, storage, and processing points. | Annually / Upon System Change |
| Encrypt Data | Ensure data is encrypted at rest and in transit. | Continuous |
| Implement Access Controls | Apply least privilege principle, MFA, strong passwords. | Continuous / User Changes |
| PCI DSS Compliance | Adhere to all PCI DSS requirements. | Annually (Assessments) |
| Privacy Regulation Compliance | Comply with GDPR, CCPA, etc. for data subject rights. | Ongoing |
| Employee Training | Regularly train staff on data security best practices. | Quarterly / Bi-annually |
| Incident Response Plan | Develop, test, and update a comprehensive breach response plan. | Annually / Upon Changes |
| Regular Audits & Updates | Conduct security audits and apply software patches. | Quarterly / Monthly |
| Vendor Due Diligence | Vet third-party processors for security and compliance. | Annually / Before Engagement |
Conclusion: The Foundation of Digital Trust
Responsible payment data management is more than just a technical challenge; it’s a fundamental aspect of building and maintaining digital trust with your customers. By systematically mapping your data, implementing robust security measures, ensuring compliance, empowering your team, and planning for contingencies, you create a resilient environment that protects sensitive information. This proactive approach not only safeguards your business from significant risks but also demonstrates your unwavering commitment to privacy, cementing your reputation as a trustworthy entity in the digital marketplace. Continuously adapting and improving your approach to managing payment data responsibly is the key to thriving in our increasingly interconnected world.












Leave a Reply