



Best Practices Managing School Records for SMEs

Share
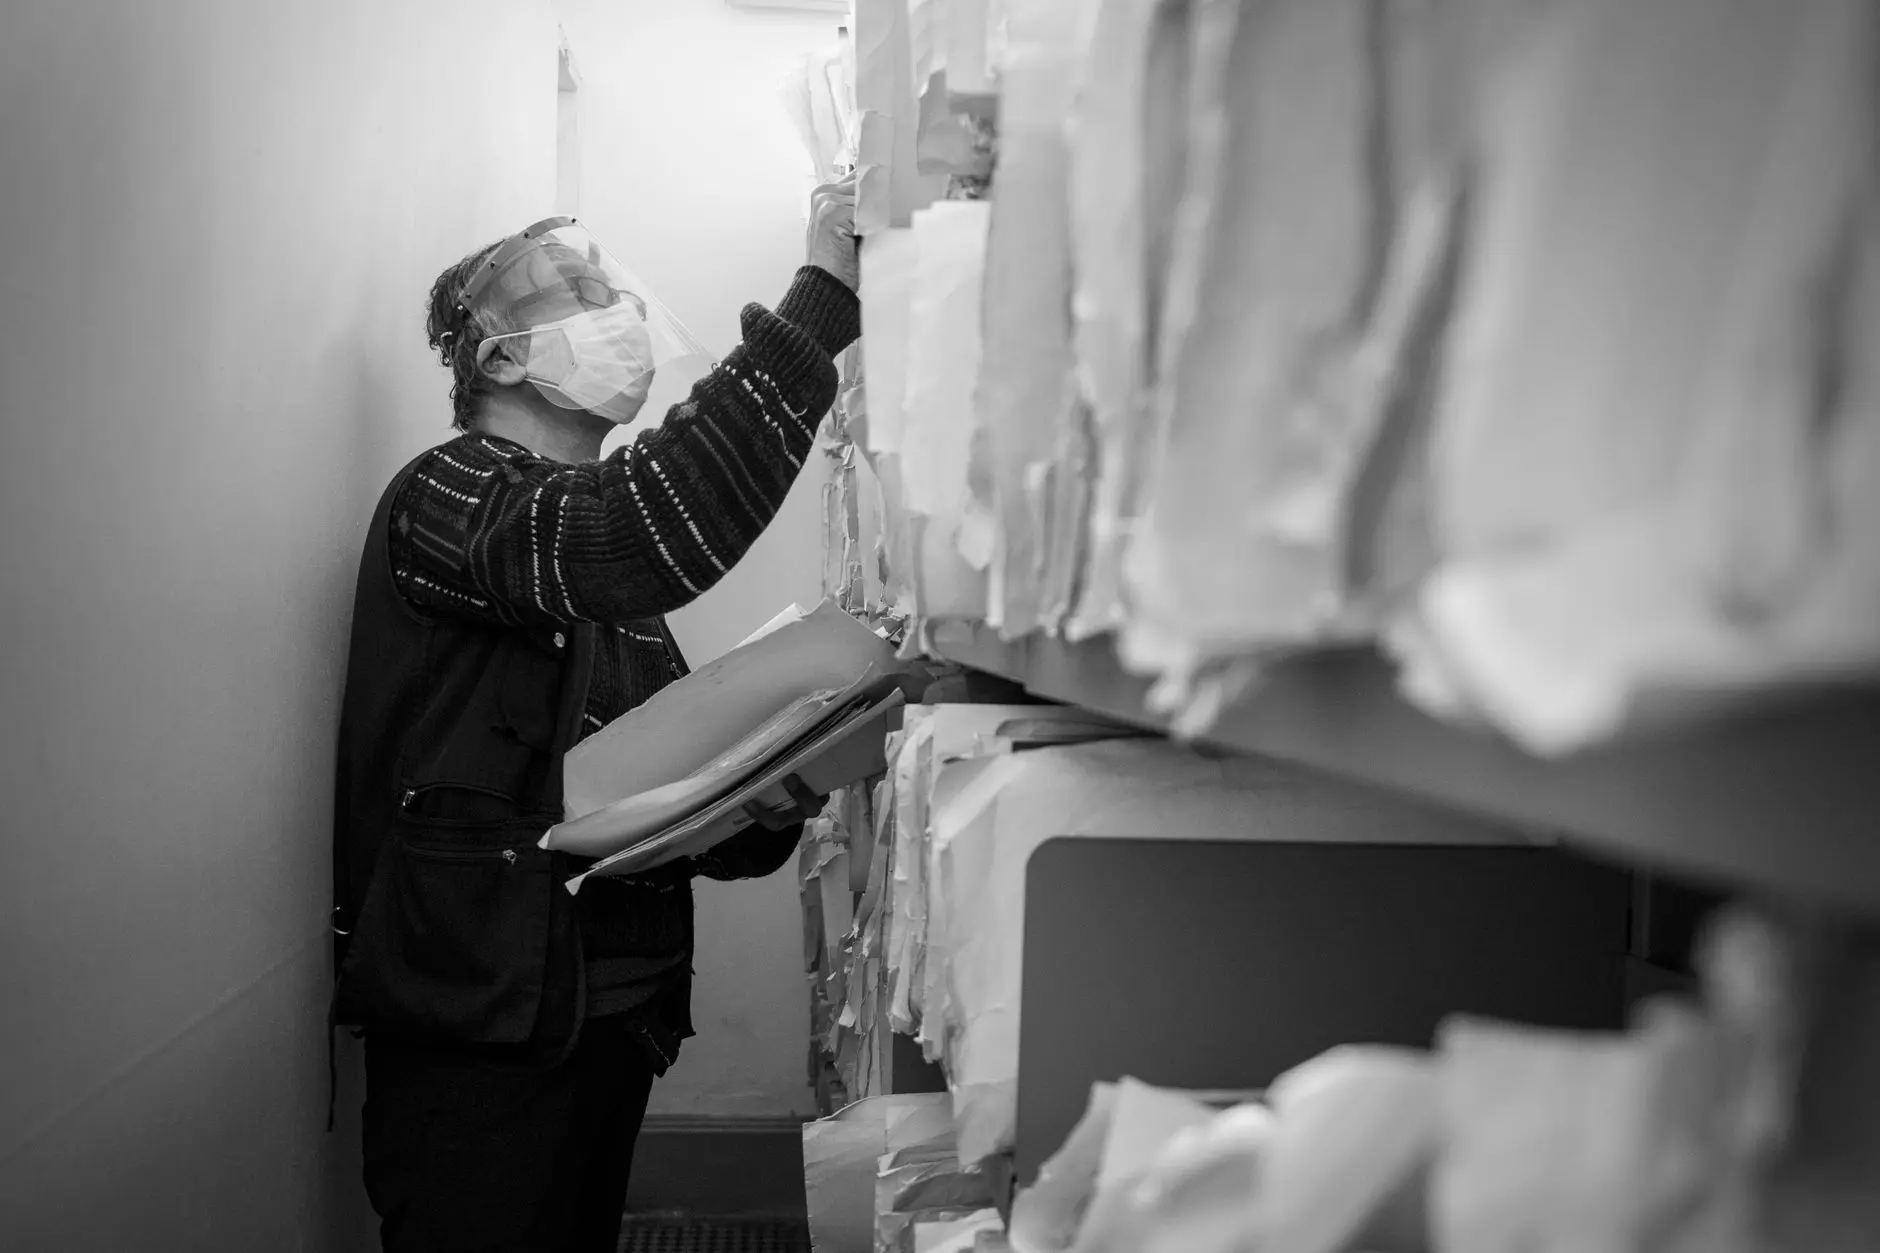
Small and medium‑sized enterprises (SMEs) that provide educational services—from tutoring centers to private primary schools—handle a surprising amount of personal data. Student names, health information, attendance logs, and assessment results are all considered sensitive under most data‑protection regimes. A single misplaced file can trigger regulatory fines, damage reputation, and erode trust with families.
Why School Records Require a Dedicated Strategy
Unlike generic business records, school records are subject to higher standards of confidentiality because they often contain minors’ data. In the EU, the GDPR labels such data as “special category” and requires explicit legal grounds for processing. In the U.S., state laws such as the Family Educational Rights and Privacy Act (FERPA) impose strict handling rules. For SMEs, the cost of non‑compliance can be disproportionate: a 2022 survey by the International Association of Privacy Professionals found that 38% of small education providers experienced a data‑security incident, yet 57% lacked a formal records‑management policy.
Core Elements of a Robust School‑Records Program
Below are the five pillars that form the foundation of any Best Practices Managing School Records approach.
1. Data Inventory and Classification
Start by cataloguing every type of record your SME creates or receives. Classify them by sensitivity (e.g., public, internal, confidential, special‑category). A simple spreadsheet can serve as a living inventory.
2. Legal Basis and Retention Schedule
Identify the lawful basis for each data type—consent, contract, legal obligation, or legitimate interest. Then define how long you must keep each record. Retention periods differ: admission forms may be retained for six years, while health records often require ten years after the student leaves.
| Record Type | Legal Basis | Retention Period |
|---|---|---|
| Enrollment applications | Contract & Legal Obligation | 6 years after last graduation |
| Medical information | Legal Obligation (health & safety) | 10 years after last attendance |
| Attendance logs | Legitimate interest | 3 years |
| Assessment results | Contract | 5 years |
3. Secure Storage and Access Controls
Physical files should be locked in fire‑rated cabinets; digital files must be encrypted at rest and in transit. Implement role‑based access so only authorized staff can view sensitive records. Multi‑factor authentication (MFA) on all devices handling school data is now considered a minimum defense.
4. Data Subject Rights Workflow
Students and parents can request access, correction, or deletion of their data. Design a clear, documented process that logs each request, the verification steps, and the completion date. Automating this workflow with a privacy‑management platform reduces manual errors.
5. Incident Response and Breach Notification
Even with safeguards, breaches happen. Prepare a response plan that outlines containment steps, internal reporting lines, and regulatory notification timelines. Under GDPR, you have 72 hours to inform the supervisory authority; under FERPA, you must notify parents within 60 days.
Practical Example: A Boutique Language School
Consider “LinguaLearn,” a private language academy with 150 students across two locations. After a routine audit, they discovered that enrollment PDFs were stored on a shared Google Drive folder accessible to all staff, including part‑time assistants. The school took the following steps:
- Moved files to an encrypted, role‑based SharePoint site.
- Created a retention policy aligning with the table above.
- Implemented MFA for all staff accounts.
- Drafted a Data Subject Rights template and trained teachers on handling requests.
- Established a breach‑response checklist and assigned a Data Protection Officer (DPO) from their part‑time HR consultant.
Within three months, LinguaLearn passed an external privacy audit with zero non‑conformities, and a parent later praised the school for “quickly providing the child’s medical records when requested.”
Expert Insight
“Schools, regardless of size, must treat student data with the same rigor as hospitals treat medical records. A clear retention schedule and controlled access are the first lines of defense,” says Helen Dixon, Data Protection Commissioner of Ireland.
Checklist for Immediate Implementation
- Conduct a data inventory and classify records.
- Map each record to a legal basis and define retention periods.
- Secure physical storage with locked cabinets; encrypt digital files.
- Set up role‑based access and enforce MFA.
- Document a Data Subject Rights request process.
- Draft a breach‑response plan and appoint a point of contact.
Common Warning Signs
- Shared folders with open permissions.
- Retention policies that keep data indefinitely.
- Staff using personal email accounts for student communication.
- Absence of a documented incident‑response procedure.
Frequently Asked Questions
Do I need a Data Protection Officer for a small school?
Not always. GDPR mandates a DPO only when core activities involve large‑scale processing of special‑category data. However, appointing a dedicated privacy lead—even part‑time—helps streamline compliance.
Can I store student records on cloud services?
Yes, provided the provider offers adequate security (encryption, certifications like ISO 27001) and you have a Data Processing Agreement (DPA) in place.
How often should I review my records‑management policy?
At least annually, or whenever there is a legislative change, a new type of data collected, or a significant incident.
Putting It All Together
Adopting these Best Practices Managing School Records equips SMEs to protect vulnerable student data, avoid costly penalties, and build confidence among parents and regulators. Start with a simple inventory, lock down storage, and embed privacy into everyday operations. The effort today prevents disruptive breaches tomorrow.
For deeper guidance on European data‑protection obligations, see the EU’s official data‑protection portal. Additional resources on secure record‑keeping are available through our Data Protection and Compliance sections.










Leave a Reply