



TP-Link Patches Zero-Day Vulnerabilities in Tapo Security Cameras

Share
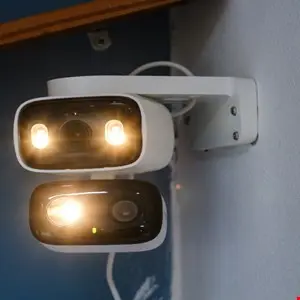
TP-Link has released a security update to address two zero-day vulnerabilities in its Tapo C200 security cameras. The flaws, discovered by researchers at OPSWAT, could allow attackers to bypass authentication and access private video feeds.
The vulnerabilities affect the Tapo C200 model, a device frequently used for home security, pet monitoring, and small office/home office (SOHO) environments. TP-Link has addressed the issues in firmware version V5_1.4.6, which was released on 18 August 2026.
Authentication Bypass and Denial of Service
The first vulnerability, tracked as CVE-2026-15315, is an authentication bypass via a replay attack. An attacker with network access could obtain a valid administrative session without needing the user’s password. According to OPSWAT, this level of access allows an attacker to modify device configurations and access privacy-sensitive functions, including live video streams and stored recordings.
The second vulnerability, CVE-2026-15316, is a denial-of-service (DoS) flaw. This impacts the camera’s onboarding configuration process. An unauthenticated attacker with network access can submit an oversized encrypted credential value, which causes the camera’s HTTPS service to crash.
Potential for Full Device Compromise
While the two identified flaws are rated as high severity, OPSWAT is currently working with TP-Link to address a third zero-day vulnerability. This additional flaw is rated as critical and could allow an attacker to fully compromise the camera, using it as a foothold to attack other devices within the same network.
Researchers suggest this third vulnerability could involve a command injection or a memory-safety bug. If exploited, it could allow an attacker to gain root access and execute code on the device.
Dahvid Schloss, COO at Suzu Labs, noted that the severity of the currently patched flaws is somewhat mitigated by the requirement for an attacker to have network access. Schloss suggested that the risk increases significantly if the camera has been port-forwarded to the internet, a configuration that is less common for standard home users but presents a larger security concern.
Users of the Tapo C200 should ensure their devices are running firmware version V5_1.4.6 or later to protect against the known vulnerabilities.











Leave a Reply