



Hackers Hijack HBO Max Reddit Account to Deploy ClickFix Malware

Share
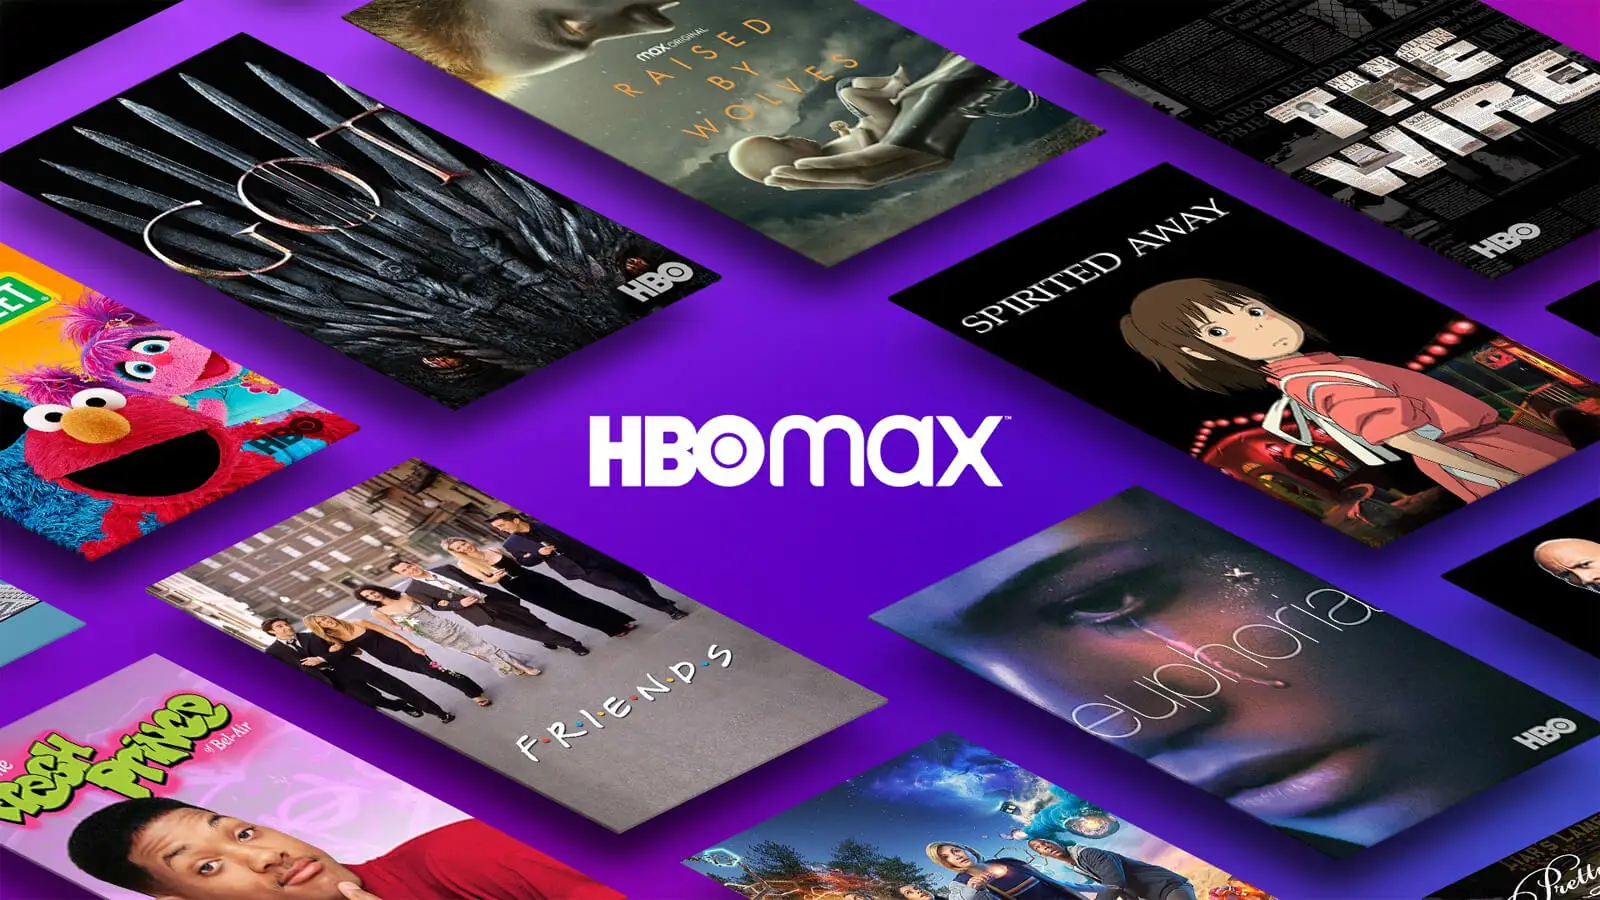
Hackers have compromised the verified u/hbomax Reddit account, using it to distribute malicious advertisements designed to infect Windows and macOS devices with information-stealing malware.
Security researchers at Hudson Rock and ADAMnetworks identified the campaign, which involved the launch of 108 malicious advertisements over a 48-hour period. The operation is part of a broader campaign dubbed “PasteSwitch,” which utilises a specific social engineering technique known as ClickFix to bypass traditional security software.
The ClickFix Social Engineering Method
The ClickFix technique works by tricking users into performing actions that appear to resolve a technical issue. The malicious advertisements, which often impersonated the streaming service or promoted fake AI tools and developer software, redirected users to deceptive websites. Once on these sites, visitors were presented with instructions to copy and paste malicious commands into legitimate operating system tools such as Windows Run, PowerShell, or the macOS Terminal.
By convincing victims to run these commands themselves, attackers can often bypass browser-based protections and endpoint security software designed to block automated malware downloads. The “PasteSwitch” name refers to this method, where the attackers’ backend infrastructure switches between different payloads, platforms, and theft methods depending on the visitor’s system.
Malware Targets and Impact
The campaign deployed various forms of malware tailored to the victim’s operating system. On macOS, researchers identified the use of MacSync, an infostealer capable of harvesting browser credentials, Firefox profiles, Telegram data, Apple Notes, and macOS passwords. Another macOS attack chain utilised “AMOS helper” to establish persistence on infected systems.
Windows users were targeted with commands using mshta and PowerShell. One observed attack chain used an MP3/HTA polyglot to create scheduled tasks and disable Microsoft’s Antimalware Scan Interface (AMSI). This allowed the Amatera Stealer to be loaded directly into memory, making detection more difficult by avoiding saving the final payload to the disk.
The campaign also targeted cryptocurrency users by distributing fake versions of Ledger, Trezor Suite, and Exodus wallet applications to steal recovery phrases. Additionally, clipboard-hijacking malware, such as AnimateClipper and ZigClipper, was observed in the wild.
Response and Mitigation
Reddit administrators have since paused the malicious advertisements after they were reported. It remains unconfirmed how the attackers gained access to the verified HBO Max account or whether other Warner Bros. Discovery assets were compromised.
Users are advised to remain highly sceptical of any website that instructs them to copy and paste code into a command line, terminal, or system tool to fix an error, verify a CAPTCHA, or install software. Legitimate service providers will almost never require a user to execute manual terminal commands for routine software updates or error resolution.










Leave a Reply