



Apple CoreGraphics Flaw: PoC Released for Actively Exploited iPhone/Mac Bug

Share
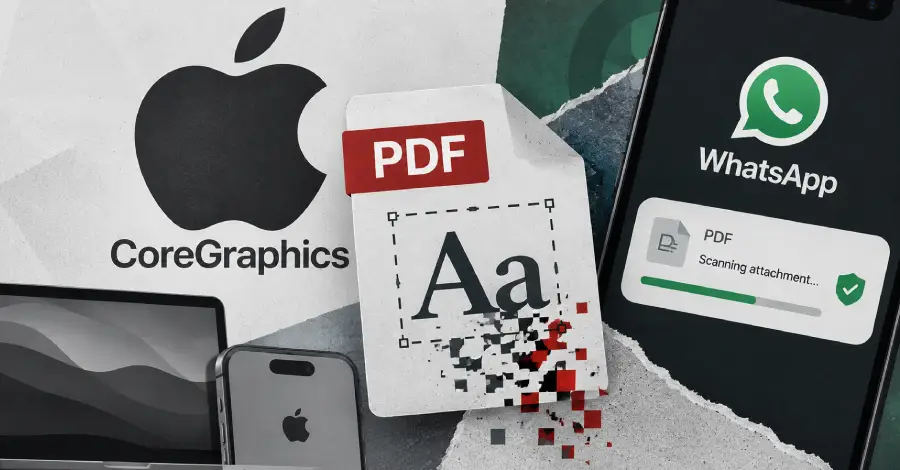
Security researchers have published the first public proof-of-concept (PoC) for CVE-2026-86950, an Apple CoreGraphics vulnerability that Apple confirmed may have been used in targeted attacks against specific individuals.
The flaw, which affects unpatched iPhones and Macs, is triggered by a malicious PDF file containing a specially crafted embedded font. When opened, the PDF can cause unpatched devices to crash.
Apple addressed the CoreGraphics vulnerability on September 28, crediting Meta Product Security with its discovery. The technology giant stated the flaw might have been leveraged in “extremely sophisticated attacks against specific targeted individuals on versions of iOS before iOS 27.” Following Apple’s advisory, the U.S. Cybersecurity and Infrastructure Security Agency (CISA) added the vulnerability to its Known Exploited Vulnerabilities (KEV) catalogue, mandating federal agencies to apply the fix by October 2.
The analysis and public PoC were released on September 30 by Dion Blazakis, Josh Maine, and Anna Groza of Calif, a firm known for its research into zero-click attack surfaces in messaging applications. Their investigation began with a binary comparison of iOS 26.7 and 26.7.1, revealing that CoreGraphics – Apple’s framework for 2D drawing, image rendering, and PDF processing – was the only library modified in the update. The patch, applied more than 20 times across eight rasterizer functions, corrects how glyph coordinates are handled.
Before the patch, a discrepancy in handling out-of-range floating-point values for glyph coordinates led to an incorrect bounding box calculation. This resulted in CoreGraphics allocating a buffer smaller than required, causing an out-of-bounds write when drawing. The researchers developed a TrueType font with large coordinates and embedded it within a PDF using a specific text matrix and nested composite-glyph scaling to exceed the coordinate limit and trigger the bug. The generation scripts and a sample PDF are available in a public GitHub repository.
While the PoC demonstrates a crash on both macOS and iOS, Calif stated that converting this memory corruption into a working exploit for code execution would require additional effort. The controlled out-of-bounds write affects two adjacent 16-bit values in a controllable buffer, potentially allowing writes to the stack or heap.
WhatsApp as a Possible Delivery Vector
Calif’s interest in WhatsApp stemmed from Meta Product Security’s credit for discovering the flaw. The researchers compared WhatsApp versions 26.37.73 and 26.38.74, identifying new code in WhatsApp’s Kaleidoscope attachment scanner. This updated scanner now reads PDF files for embedded font streams and flags suspicious ones with defect tags such as MalformedFontProgram, UndecodableFontProgram, and UnverifiedFontProgram. The presence of any such tag results in a high-risk score, prompting WhatsApp to halt automatic parsing of the flagged file.
Calif described these changes as circumstantial evidence suggesting WhatsApp could have been a delivery vector for the in-the-wild attacks. An earlier version of Calif’s analysis initially claimed that the research suggested WhatsApp could deliver a malicious PDF that triggers the flaw when a victim opens a chat with automatic media downloads enabled. This specific statement was removed shortly after publication by Calif CEO Thai Duong, who described the change as removing speculation.
The firm’s analysis now concludes with a question: whether the flaw “was combined with additional vulnerabilities in WhatsApp to reach parsing with less user interaction,” implying potential user action or further vulnerabilities might be needed for a full attack chain via WhatsApp. WhatsApp has not released any advisory linking this flaw to its products. Meta, WhatsApp’s parent company, did not respond to inquiries regarding WhatsApp’s involvement in the reported attacks.
This scenario has historical precedent; in August 2025, WhatsApp assessed that a flaw in its linked-device synchronisation messages, combined with a separate Apple out-of-bounds write, may have been used in attacks against a small number of targeted users.
No network indicators, attacker identifiers, or exploit payload names related to the CVE-2026-86950 attacks have been made public. Apple has not commented on whether Lockdown Mode would have prevented the delivery path used in the reported incidents, or if any workaround exists for systems unable to update immediately.










Leave a Reply