



Telus Notifies Customers of Multi-Month Account Breach

Share
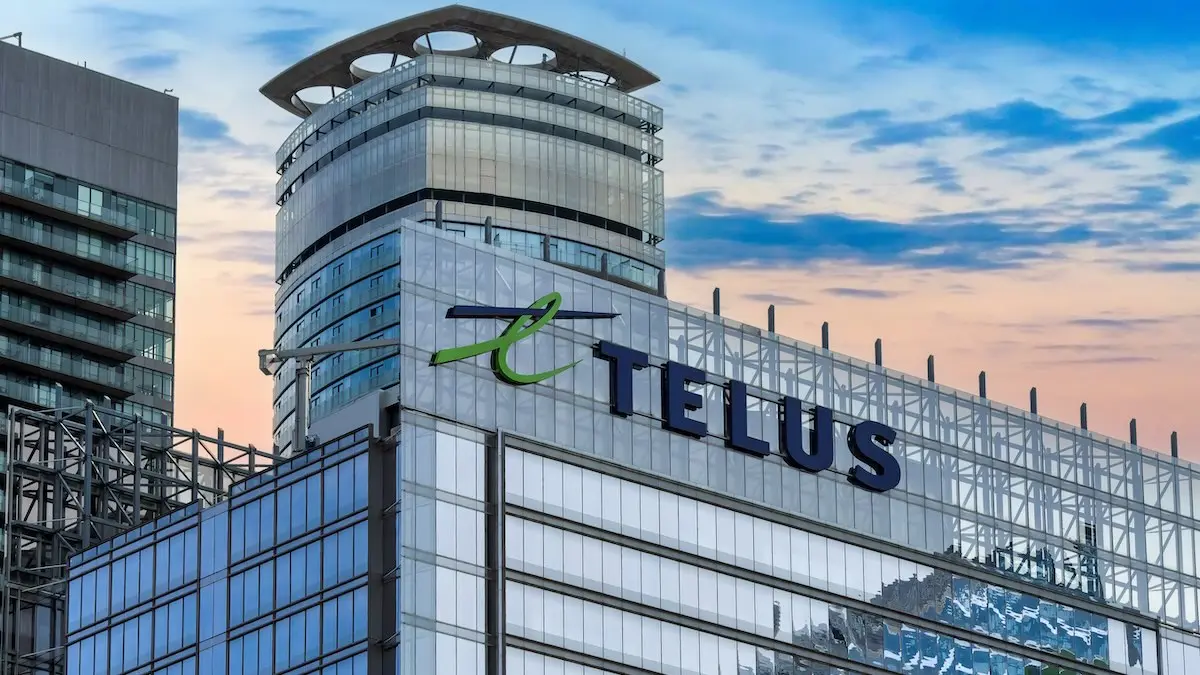
Telus, a major Canadian telecommunications provider, has notified customers that their accounts were compromised in a breach spanning several months.
The company stated that the intrusions occurred between February 2025 and June 2026, during which attackers used stolen credentials to gain unauthorised access to subscriber profiles.
Exposed Data and Fraudulent Activity
The information accessed during the campaign included names, account numbers, phone numbers, billing addresses, and email addresses. Attackers also obtained partial payment card numbers, subscription details, and payment histories.
Beyond the theft of information, the breach had operational consequences. Telus reported that attackers used the stolen data to attempt to persuade customers to move their services to competing providers. In some instances, the attackers also made unauthorised changes to the affected accounts.
Company Response and Historical Context
Telus has reset the compromised credentials and implemented enhanced security monitoring for all impacted accounts. The company has notified the Vancouver Police Department and is providing complimentary identity theft protection services to affected victims.
The nature of the incident suggests a credential stuffing or account takeover (ATO) campaign, likely involving credentials obtained from a third party. While the company has not explicitly confirmed the specific source of the passwords, this method involves using previously leaked login details to gain access to unrelated services.
This incident follows a significant security event involving Telus Digital, a subsidiary of the company. In March, the cybercrime group ShinyHunters claimed to have exfiltrated approximately one petabyte of data from the subsidiary’s systems.











Leave a Reply