



Can Someone Else Make a Privacy Complaint for a Child?

Share
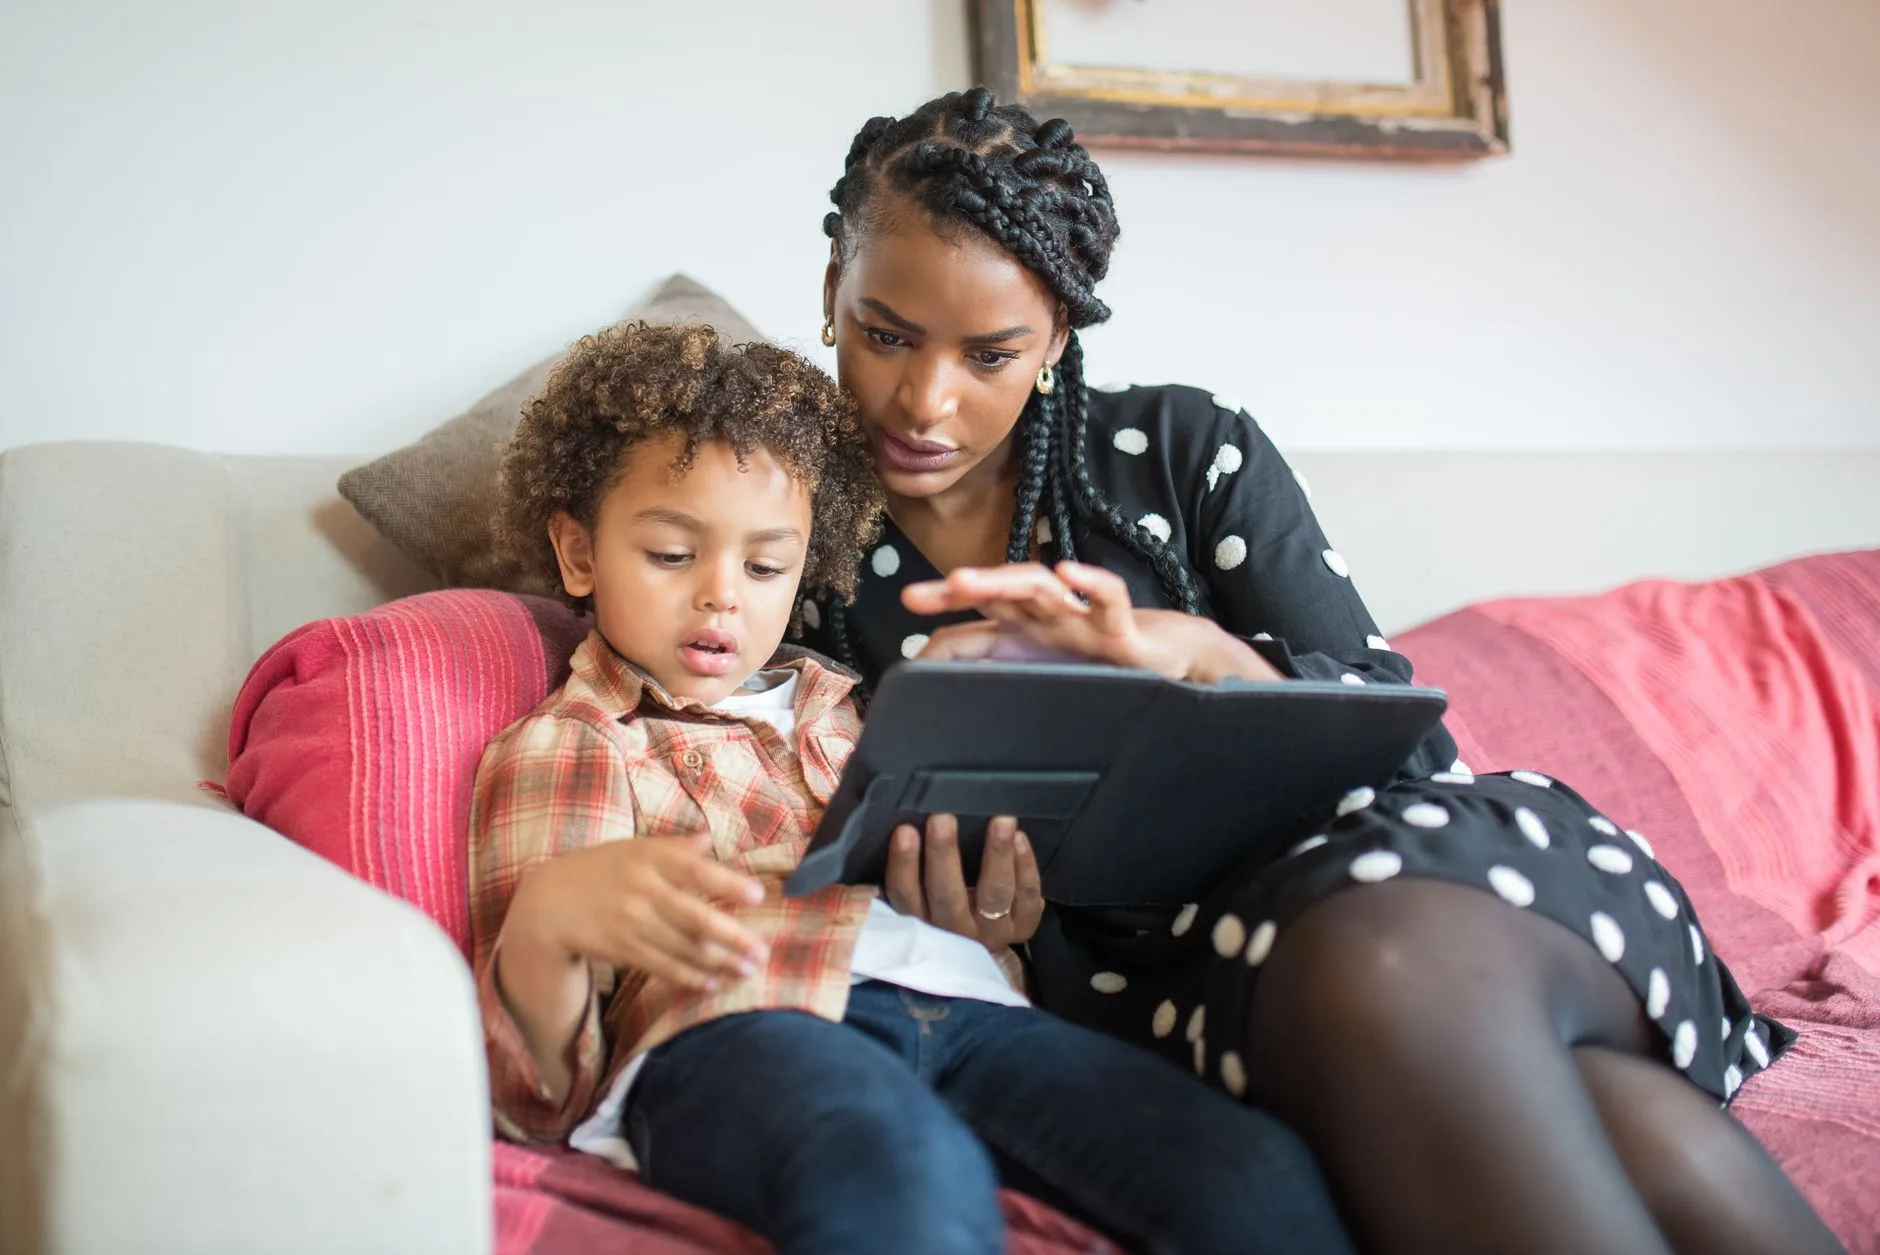
In Lagos, as in many rapidly digitizing cities across Africa, children are increasingly consuming content through educational apps, social media, and gaming platforms. While this digital immersion offers immense opportunities, it creates a significant vulnerability: children are often unaware that their personal data—from their location to their behavioral patterns—is being tracked, profiled, and sometimes sold. When a data breach or misuse occurs, a ten-year-old cannot walk into a regulatory office to demand justice. This raises a critical legal question: if a child is the victim, how can someone else make a complaint for a child to ensure their rights are enforced?
The Legal Paradox of the Minor Data Subject
In the eyes of data protection laws like the GDPR (General Data Protection Regulation) in Europe and the NDPA (Nigeria Data Protection Act) in Nigeria, a child is a “data subject.” This means they possess fundamental rights, such as the right to access their data, the right to be forgotten, and the right to object to processing. However, there is a practical and legal hurdle: legal capacity.
Most legal systems dictate that minors lack the full capacity to enter into binding agreements or to initiate formal legal proceedings. Because a child may not fully understand the implications of a privacy policy, the law shifts the responsibility of oversight to adults. Consequently, the ability to exercise data subject rights on behalf of a minor is not an open door for anyone; it is a controlled mechanism designed to protect the child’s best interests.
How Can Someone Else Make a Complaint for a Child?
To file a valid complaint, the individual must have the legal standing to represent the minor. Generally, this falls into three distinct categories:
1. Parents and Legal Guardians
This is the most common path. Under most jurisdictions, parents or legal guardians are considered the natural representatives of a child. They have the authority to exercise rights such as requesting the deletion of a child’s account or withdrawing consent for data processing. In many regions, the age of digital consent (the age at which a child can legally consent to data processing without a parent) varies, but until that age is reached, the parent is the primary gatekeeper.
2. Legal Representatives and Attorneys
In more complex scenarios—such as a large-scale data breach involving a school or a tech platform—a parent may appoint a legal professional to act on their behalf. An attorney can file formal complaints with data protection authorities or initiate litigation in court. This is particularly relevant in class-action scenarios where a group of parents seeks redress for a systemic privacy failure.
3. Regulatory Authorities
Regulators do not always wait for a parent to act. If a regulator, such as the Nigeria Data Protection Commission (NDPC), identifies a systemic risk to children’s data, they can launch an investigation and file complaints or enforcement actions on behalf of the public interest. This is a vital safeguard that ensures children are protected even when their parents are unaware of the risks.
“The principle of the best interests of the child must be a primary consideration in all actions concerning children, whether undertaken by public or private social welfare institutions, courts of law, administrative authorities or legislative bodies.” — United Nations Convention on the Rights of the Child
Comparing Representation Frameworks
The following table outlines who can typically intervene in different privacy scenarios:
| Scenario | Who Can File? | Required Proof |
|---|---|---|
| Minor’s social media account hacked | Parent or Legal Guardian | Proof of guardianship/parental relationship |
| Massive leak of school records | Parents, Lawyers, or Regulators | Legal standing or regulatory mandate |
| Unauthorized tracking by an app | Parent or Data Protection Authority | Evidence of non-compliance with age-appropriate design |
| Dispute over inheritance of digital assets | Court-appointed Representative | Legal court order or testamentary proof |
A Practical Scenario: The “Edu-Track” Data Breach
Consider the case of “Edu-Track,” a fictional educational app used by primary schools in Abuja. The app collected the names, home addresses, and even the dietary preferences of thousands of students. A vulnerability in the app’s cloud storage allowed an unauthorized third party to access this database.
A mother, discovering that her child’s location history was potentially exposed, realized she could not simply “sue” as an individual easily. However, she had two clear paths. First, she could contact Edu-Track directly to demand a data audit and deletion of her child’s sensitive records. Second, she could file a formal complaint with the NDPC. Because the breach affected thousands of children, the regulator had the power to step in, even if many parents had not yet realized the breach occurred. This demonstrates how the ability for someone else to make a complaint for a child serves as a multi-layered safety net.
Practical Steps for Parents and Compliance Teams
Whether you are a concerned parent or a business leader ensuring your organization maintains compliance, the following steps are essential for managing minor-related privacy risks:
For Parents and Guardians:
- Audit App Permissions: Regularly check which apps your child uses and what permissions (location, microphone, contacts) they have granted.
- Document Misuse: If you suspect a privacy violation, take screenshots and keep a log of how the data was misused. This is vital for any formal complaint.
- Use Official Channels: Start by contacting the company’s Data Protection Officer (DPO). If they do not respond within the statutory timeframe (usually 30 days), escalate to your national regulator.
For Businesses and Tech Teams:
- Implement Age Verification: Ensure you have robust methods to distinguish between adults and minors.
- Adopt Privacy by Design: When designing products for children, default to the highest privacy settings. Understanding your data protection obligations is the first step to avoiding regulatory fines.
- Simplify Consent: If your service is directed at children, your parental consent mechanisms must be clear, easy to use, and not hidden behind complex legal jargon.
Frequently Asked Questions (FAQ)
Can a teacher file a privacy complaint for a student?
Generally, no. While teachers have a duty of care, they do not typically hold the legal guardianship required to exercise data subject rights. They should instead report concerns to the school administration or the parents.
What if parents disagree on a privacy decision?
This can complicate the process. Most regulators and platforms require consensus or a clear legal determination of who holds primary decision-making authority (e.g., through a custody agreement) before acting on a request.
Can an NGO file a complaint for children?
In many jurisdictions, non-governmental organizations (NGOs) or advocacy groups can file complaints if they can demonstrate that the issue is of significant public interest or if they have been granted legal standing by a court.
Conclusion
Protecting the digital footprint of the next generation requires more than just strong passwords; it requires active advocacy. While a child may lack the legal tools to defend their own privacy, the law provides pathways for parents, legal experts, and regulators to step in. Knowing how someone else can make a complaint for a child is a fundamental part of modern digital literacy. By staying informed and acting decisively, we can ensure that the digital world remains a safe space for learning and growth rather than a playground for data exploitation.











Leave a Reply