



What African startups Know ISO 27001 and Privacy Readiness

Share
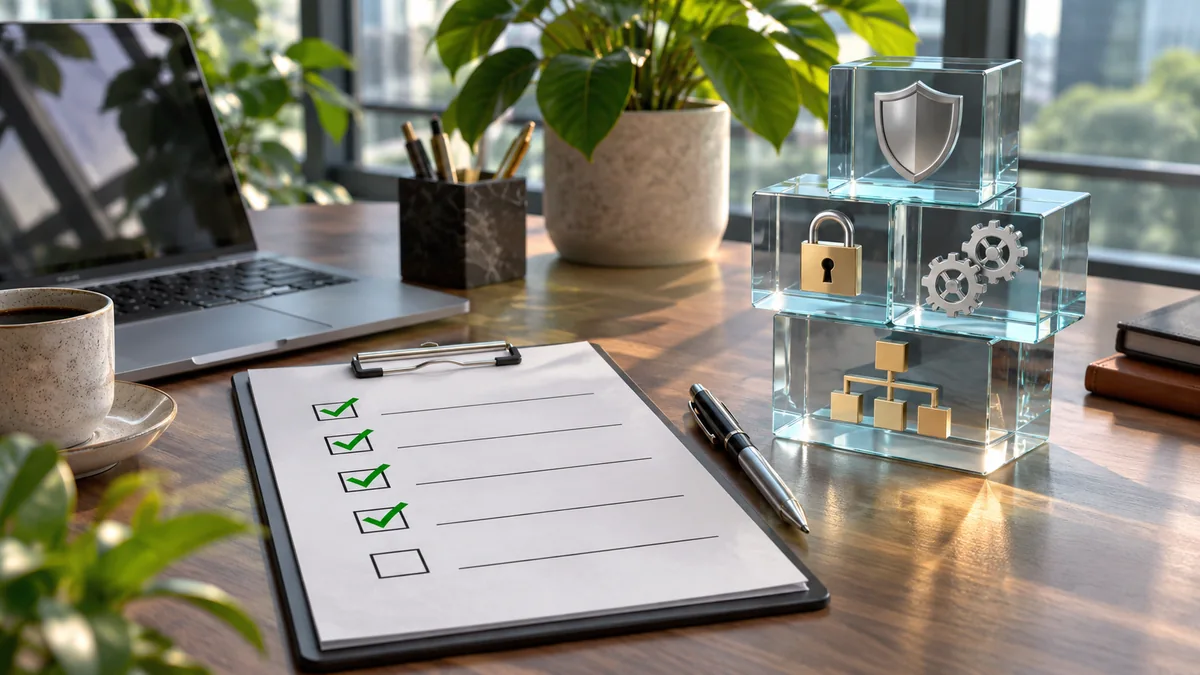
Navigating Security Standards in Emerging Markets
Venture-backed technology companies across Lagos, Nairobi, Cairo, and Cape Town face a distinct operational hurdle. When scaling beyond local borders, enterprise clients and international investors rarely accept verbal assurances of data safety. They demand formal proof. For compliance officers and founders, bridging the gap between baseline local data protection and rigorous global security standards is critical for survival and expansion.
Understanding ISO 27001 and privacy readiness is no longer an optional checklist item reserved for multinational corporations. It is the primary passport for African technology ventures seeking to close enterprise deals, integrate with global financial networks, and attract institutional capital.
The Real Value of ISO 27001 for Emerging Tech Ventures
ISO/IEC 27001 is the world’s best-known standard for information security management systems (ISMS). It provides a systematic approach to managing sensitive company and customer information through effective risk management. According to the International Organization for Standardization, certification demonstrates that an organization has invested in people, processes, and technology to protect information assets.
For young companies operating with lean engineering teams, building an ISMS from scratch can feel daunting. However, waiting until a security incident occurs or until a major client mandates an audit often results in panicked, expensive retrofitting. Proactive privacy readiness ensures that data governance grows alongside the code base.
Bridging ISO 27001 and Regulatory Compliance
Many founders mistakenly view ISO 27001 as purely an IT project. In reality, it intersects deeply with regional privacy laws such as the Nigeria Data Protection Act (NDPA), Kenya’s Data Protection Act, and South Africa’s POPIA. While privacy laws dictate legal rights and lawful processing grounds, ISO 27001 supplies the operational controls to enforce those rules.
When African startups know ISO 27001 readiness inside out, they can easily map technical controls to regulatory mandates. Access controls, encryption standards, and incident response plans satisfy both international security auditors and local data protection regulators simultaneously.
Core Elements of an ISMS for Startups
- Risk Assessment: Identifying where sensitive customer data lives, who accesses it, and what vulnerabilities exist.
- Access Control: Enforcing the principle of least privilege across production databases and administrative dashboards.
- Incident Response: Establishing a tested protocol for detecting, containing, and reporting data breaches.
- Vendor Management: Vetting third-party cloud service providers and software-as-a-service vendors for security hygiene.
A Practical Scenario: From Local App to Global Enterprise Vendor
Consider a fintech scale-up based in East Africa that processes cross-border merchant payments. Initially, the platform complied only with local payment authority guidelines. When the company attempted to partner with a global payment gateway based in Europe, the partnership stalled. The prospective partner refused API integration until the startup provided an independent ISO 27001 audit report.
By investing six months into building an internal ISMS, conducting gap analyses, and tightening code deployment pipelines, the startup achieved certification. Not only did the European partnership close within weeks, but the company also reduced its internal server vulnerabilities by seventy percent, avoiding a potential ransomware attack.
ISO 27001 vs. Privacy Readiness: Key Differences
| Dimension | ISO 27001 Certification | Privacy Readiness |
|---|---|---|
| Primary Focus | Information security management and risk reduction | Lawful data processing and data subject rights |
| Validation | Third-party formal audit and certificate issuance | Internal self-assessment and regulatory alignment |
| Scope | Whole organization or specific product lines | Personally identifiable information (PII) lifecycle |
Expert Perspective on Building Resilient Tech Ecosystems
Security experts emphasize that compliance must be treated as an enabler rather than a bureaucratic checkbox. As noted by industry analysts, companies that embed security early preserve enterprise value during due diligence.
“Security and privacy readiness are the foundational infrastructure of modern digital trade. African innovators cannot afford to treat compliance as an afterthought if they want to compete on the global stage.” – Regional Cybersecurity Researcher
Actionable Checklist for Founders and CTOs
- Conduct an internal data mapping exercise to locate all Personally Identifiable Information (PII).
- Implement multi-factor authentication (MFA) across all employee accounts and developer environments.
- Draft a comprehensive incident response plan and conduct a tabletop simulation.
- Engage an accredited external consultant to perform a readiness assessment before scheduling an official audit.
Frequently Asked Questions
Is ISO 27001 mandatory for African startups?
It is rarely mandated by local law, but major enterprise clients, multinational partners, and venture capital investors increasingly require it as a pre-condition for business relationships.
How long does the certification process take?
Depending on the maturity of existing infrastructure and team size, achieving ISO 27001 certification typically takes between six to twelve months.
Conclusion
Mastering ISO 27001 and privacy readiness transforms an early-stage company from a high-risk gamble into a trusted enterprise partner. When African startups know ISO 27001 readiness, they protect their users, satisfy regional regulators, and unlock unprecedented opportunities in the global digital economy.












Leave a Reply