



What Is Privacy Notice? A SIMple Privacy Needle Explainer

Share
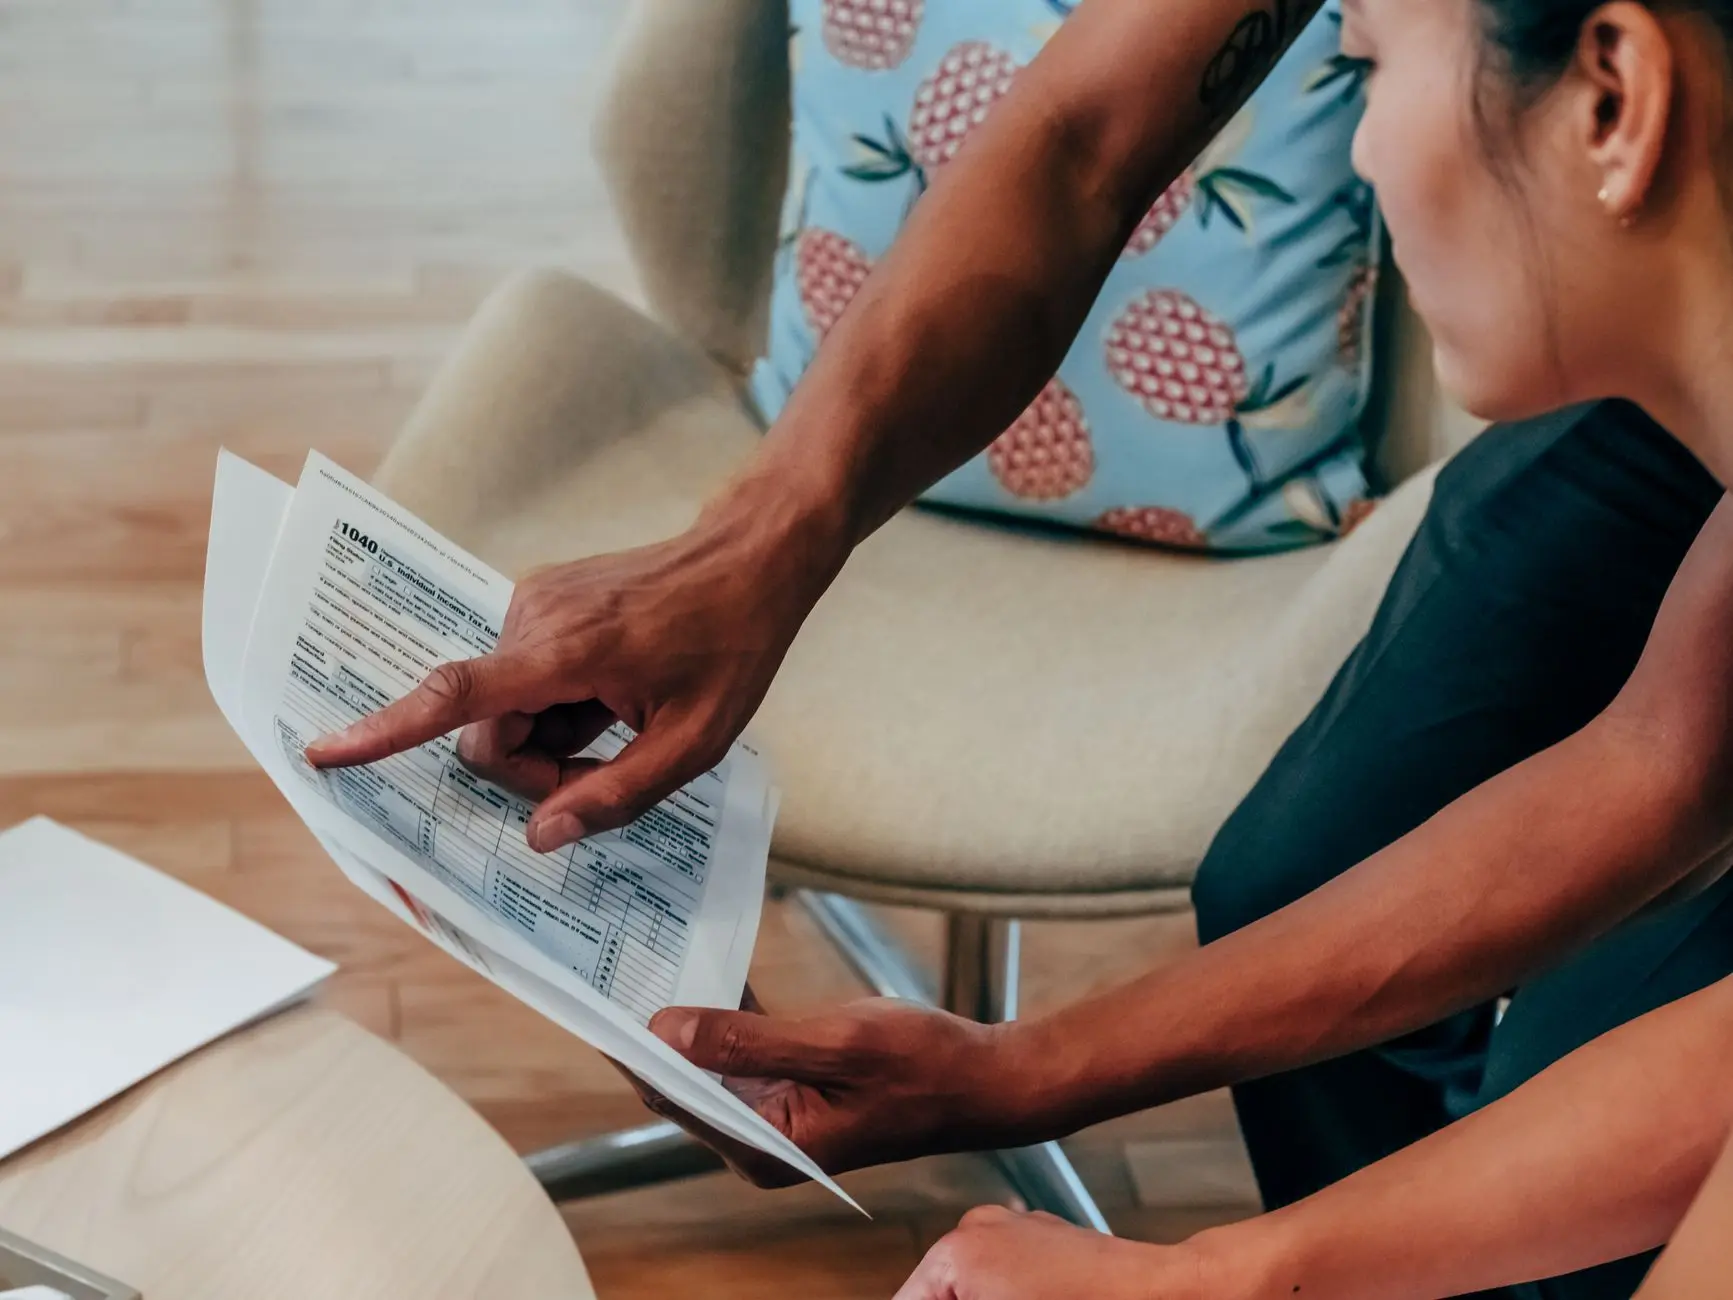
Understanding the Core of Digital Transparency
Every time you create an online account, download a mobile application, or submit your email address to a newsletter, you encounter a legal disclosure detailing how your personal information will be handled. This document is known as a privacy notice. Far from being mere digital boilerplate, a well-crafted privacy notice serves as the foundational contract of trust between individuals who share data and organizations that collect it.
For organizations operating under strict global frameworks like the General Data Protection Regulation (GDPR) or the California Consumer Privacy Act (CCPA), providing a clear notice is not optional. It is a mandatory legal obligation designed to empower data subjects. This Notice Needle Explainer breaks down everything you need to know about these essential compliance documents, exploring what they include, why they matter, and how to draft or evaluate them effectively.
Defining the Notice Needle Explainer: What Is a Privacy Notice?
At its core, a privacy notice is a public-facing statement issued by an organization that discloses how the entity gathers, uses, discloses, and manages a customer or employee’s personal data. It fulfills a fundamental legal and ethical requirement: transparency. When people understand exactly what happens to their information, they can make informed decisions about their digital footprint.
It is important to distinguish between a privacy notice and a privacy policy. While the terms are frequently used interchangeably in everyday conversation, compliance professionals maintain a strict distinction. A privacy notice is typically customer-facing, explaining data practices to the end user. A privacy policy, on the other hand, is often an internal document outlining how an organization handles employee data or governs its internal cybersecurity and information security operations.
Key Components of an Effective Privacy Notice
Regulators across multiple jurisdictions require specific elements to be present in any compliant data disclosure. Vague or hidden clauses can result in severe regulatory penalties and loss of consumer trust. According to the GDPR compliance guidelines, transparency is a cornerstone of lawful data processing.
A comprehensive privacy notice typically includes the following critical details:
- Identity and Contact Details: Who is collecting the data, including organizational name, address, and data protection officer (DPO) contact information.
- Categories of Data Collected: What specific information is gathered, such as names, IP addresses, financial details, or biometric markers.
- Purposes of Processing: Why the data is being collected, whether for order fulfillment, marketing analytics, or security verification.
- Legal Basis: The lawful grounds for processing, such as explicit consent, contractual necessity, or legitimate interest.
- Data Sharing and Recipients: Whether information is sold, shared with third-party vendors, or transferred across international borders.
- Retention Periods: How long the organization intends to keep the personal data before secure deletion.
- Individual Rights: Clear instructions on how users can exercise their rights to access, correct, or delete their data.
Privacy Notice vs. Privacy Policy: Key Differences
To help business leaders and compliance teams differentiate between internal governance and external transparency, review the quick comparison table below.
| Feature | Privacy Notice | Privacy Policy |
|---|---|---|
| Primary Audience | External users, customers, website visitors | Internal employees, IT teams, management |
| Primary Purpose | External transparency and legal compliance | Internal data governance and security rules |
| Required by Law | Yes, mandatory for consumer-facing entities | Internal policies are recommended, but format varies |
Real-World Scenario: The Cost of Poor Transparency
Consider a mid-sized e-commerce startup that launched a mobile shopping application without updating its website disclosure. The company collected user location data and browsing history to power targeted advertising but failed to disclose this third-party sharing in its disclosure statement. When European regulators reviewed the application following a user complaint, the company faced significant fines not only for unlawful data processing but specifically for failing to provide transparent, accessible information.
As privacy expert Max Schrems often notes, “Transparency is the baseline of modern data protection; without clear information, individuals cannot defend their fundamental rights.” This principle underscores why organizations must treat transparency documents as living compliance instruments rather than static legal text.
Best Practices for Writing and Maintaining Compliance Documents
Drafting an effective disclosure requires balancing legal precision with plain language readability. Compliance teams should implement the following action steps:
- Use Plain Language: Avoid overly dense legal jargon. A high school reading level ensures everyday users actually understand the terms.
- Adopt a Layered Approach: Provide a short summary upfront with links to deeper, granular details for users who want complete technical specifics.
- Keep It Updated: Review disclosures whenever business operations change, such as introducing new AI analytics tools or partnering with new cloud vendors.
- Ensure Easy Accessibility: Place links clearly in website footers, app store listings, and sign-up forms.
Frequently Asked Questions
Is a privacy notice legally required for all websites?
If your website collects any form of personal data, including email addresses via contact forms, analytics cookies, or account registrations, privacy laws in regions like the EU, UK, and California require a clear disclosure.
How often should an organization update its disclosure?
You should review and update your notice at least annually, or immediately whenever your data collection practices, technology stack, or third-party vendors change.
Conclusion
Mastering the fundamentals outlined in this Notice Needle Explainer is essential for navigating modern regulatory landscapes. A transparent privacy notice protects organizations from costly penalties while fostering genuine digital trust with customers. By prioritizing clarity, accuracy, and accessibility, businesses can turn compliance requirements into a competitive advantage.












Leave a Reply