



How Policy Changes Affect e-Commerce Businesses

Share
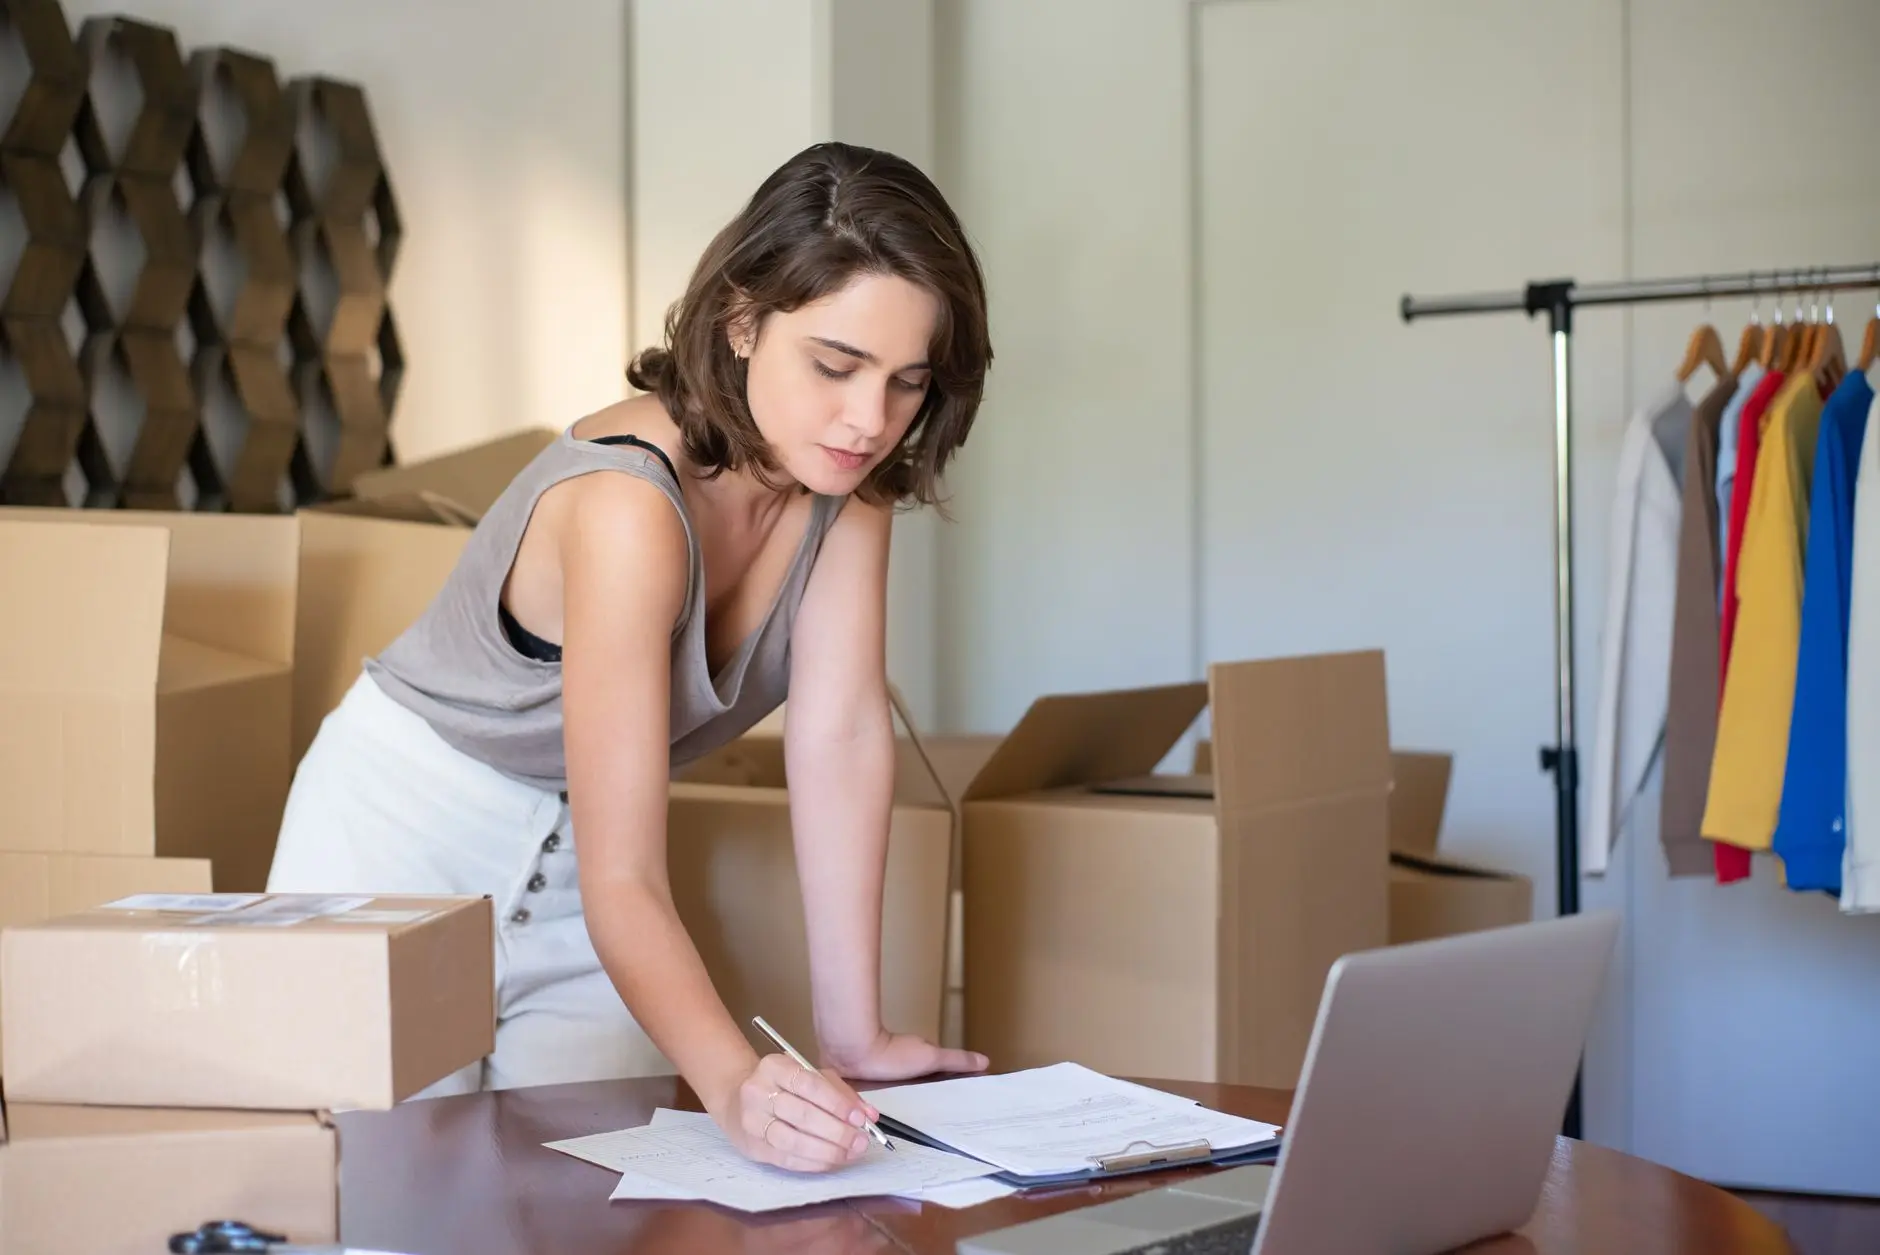
When legislators update privacy statutes or major tech platforms rewrite terms of service, online retail operations feel the immediate impact. Today, online merchants face a shifting regulatory maze where consumer data collection, tracking cookies, and cross-border transactions face strict scrutiny. Understanding how Policy Changes Affect e commerce is no longer optional for founders and compliance officers; it is a core pillar of operational survival.
As global data protection frameworks mature, digital storefronts must adapt faster than ever. A single legislative adjustment can invalidate years of customer acquisition strategies, rendering traditional marketing funnels non-compliant almost overnight. Below, we break down the operational, financial, and technical consequences that modern digital merchants encounter when regulatory standards shift.
The Core Drivers Behind Modern Regulatory Shifts
Legislative bodies across the European Union, the United States, and other jurisdictions are tightening rules around how personal data is gathered, stored, and monetized. The enforcement of frameworks like the General Data Protection Regulation (GDPR) and emerging state-level US privacy laws forces merchants to rethink their data pipelines. According to recent regulatory enforcement trends, supervisory authorities are actively auditing online checkouts and cookie banners for deceptive design patterns.
Furthermore, technology gatekeepers like Apple and Google are implementing their own internal privacy policies. Features such as App Tracking Transparency and the phasing out of third-party cookies drastically alter how digital storefronts target buyers. Merchants can no longer rely on passive tracking to build profitable marketing campaigns.
How Policy Changes Affect e-Commerce Operations
When new rules take effect, digital stores experience friction across multiple departments. Compliance is not merely a legal checkbox; it changes software architecture, customer service workflows, and financial forecasting.
- Marketing Attribution and ROI: Stricter tracking consent rules mean fewer granular data points for ad platforms, increasing customer acquisition costs.
- Website Architecture and Consent Management: Stores must integrate robust Consent Management Platforms (CMPs) that respect user opt-outs in real time.
- Vendor Risk Management: Third-party logistics, payment gateways, and software-as-a-service providers must sign updated data processing agreements.
Operational Impact Comparison
| Area of Business | Before Policy Overhaul | After Policy Overhaul |
|---|---|---|
| Data Collection | Default opt-in tracking and broad profiling | Explicit opt-in consent and data minimization |
| Customer Acquisition | Targeted hyper-segmentation via third-party cookies | Contextual advertising and first-party data strategies |
| Legal Exposure | Low regulatory oversight | High risk of substantial financial penalties |
A Real-World Compliance Scenario
Consider a mid-sized online apparel retailer operating across multiple international borders. Following a local update to data protection legislation, the company received a consumer complaint regarding an ambiguous checkout consent checkbox. Because the store failed to decouple marketing consent from its terms of service agreement, local regulators launched an inquiry.
The business had to halt active retargeting campaigns, hire external legal counsel to overhaul its website privacy disclosures, and manually purge unverified user segments. The financial impact extended far beyond legal fees; lost momentum during a peak shopping season resulted in a twenty percent drop in quarterly revenue. This scenario highlights why proactive adaptation to compliance mandates protects long-term viability.
Actionable Steps for Digital Merchants
To insulate your online store against regulatory shocks, implement a structured resilience plan. Following expert guidance from bodies like the Information Commissioner’s Office helps businesses stay aligned with evolving standards. Use the following checklist to evaluate your current setup:
- Audit Data Flows: Map every point where customer data enters your ecosystem, including checkouts, newsletter signups, and customer support chat logs.
- Review Privacy Disclosures: Ensure your website privacy notice is clear, jargon-free, and accurately reflects your current data retention practices.
- Upgrade Consent Mechanics: Replace legacy cookie banners with modern CMPs that give users genuine control over tracking preferences.
- Prioritize First-Party Data: Build direct relationships with your buyers through loyalty programs and email lists rather than relying on rented audience data.
Privacy compliance is no longer just a legal obligation. It is a fundamental trust signal that dictates whether modern consumers will complete a transaction on your digital storefront.
Frequently Asked Questions
Do privacy policy changes apply to small e-commerce stores?
Yes. Many modern privacy laws apply based on the geographic location of the consumer, not the physical location or size of the business. Even small dropshipping stores must respect user rights if they sell to regulated regions.
How often should online stores update their privacy notices?
Merchants should review their privacy policies at least annually or immediately whenever they introduce new data collection tools, third-party software plugins, or payment processors.
Conclusion
Navigating the complex landscape of digital regulation requires constant vigilance. As legislators and tech giants continue to tighten the rules, the overarching lesson remains clear. When Policy Changes Affect e commerce, proactive brands that embrace transparency and data minimization will outperform competitors who treat privacy as an afterthought.












Leave a Reply