



How Public Agencies Can Prepare for NDPC Questions on Complaints

Share
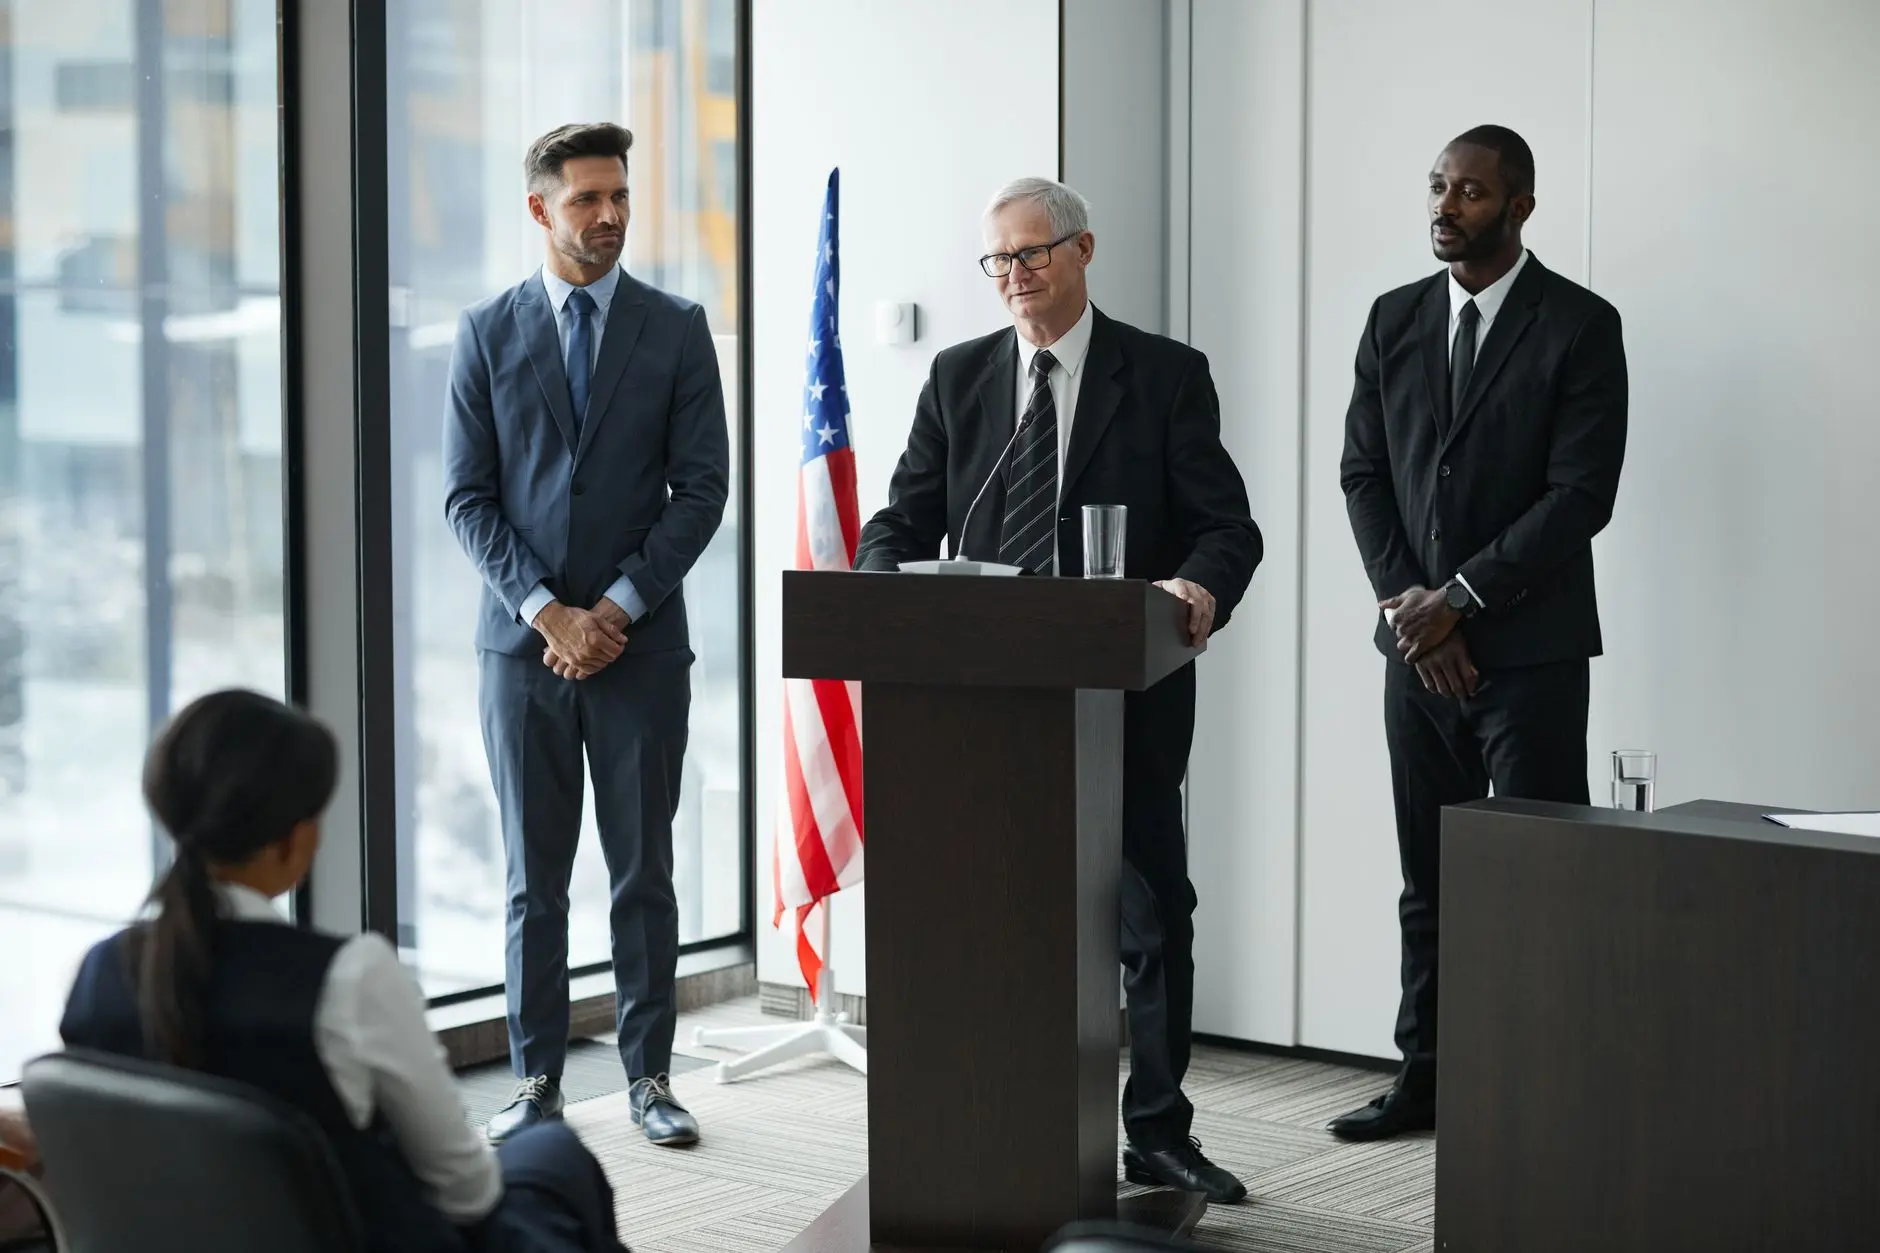
When a citizen submits a privacy grievance against a government body, regulatory scrutiny follows swiftly. Public institutions handle vast volumes of sensitive citizen records, ranging from national identification numbers to tax documents and healthcare registries. Because these entities hold immense authority, data protection regulators expect the highest standards of accountability. When public agencies prepare NDPC questions on complaints, they must move beyond generic administrative replies and provide structured, evidence-based disclosures.
Understanding the Regulatory Mandate for Public Bodies
Government ministries, departments, and agencies operate under strict statutory obligations. Under the Nigeria Data Protection Act and subsequent oversight by the Nigeria Data Protection Commission (NDPC), public sector organizations are not exempt from privacy rules. In fact, their duty of care is often higher due to the mandatory nature of government data collection. When complaints arise regarding unauthorized data sharing, delayed access requests, or weak security safeguards, the NDPC issues formal inquiries that require meticulous answers.
Failing to respond adequately to regulatory queries can lead to public reprimands, mandatory audits, and severe reputational damage. Compliance teams within public institutions must establish repeatable workflows to gather facts, verify logs, and draft legally sound explanations before deadlines expire.
Step-by-Step Guide When Public Agencies Prepare NDPC Questions on Complaints
Handling a regulatory inquiry requires cross-functional coordination between legal, IT, and communications departments. Agencies must adopt a systematic approach to ensure no detail is overlooked.
- Triage and Acknowledge Immediately: Log the inquiry upon receipt and notify the data protection officer (DPO) alongside executive leadership.
- Secure Relevant Logs and Evidence: Preserve electronic audit trails, access logs, and correspondence related to the complainant without altering data.
- Conduct an Internal Fact-Finding Review: Interview the specific department or personnel involved in processing the data subject’s information.
- Draft the Regulatory Response: Formulate a factual, clear, and objective reply referencing relevant legal provisions and internal compliance frameworks.
- Implement Corrective Measures: If a procedural gap caused the complaint, document the immediate fixes applied to prevent future occurrences.
Common Vulnerabilities That Trigger NDPC Inquiries
Citizens typically escalate issues to the NDPC when local grievance mechanisms fail. Understanding why these complaints reach the regulator helps agencies fortify their operations. Common triggers include delayed responses to Data Subject Access Requests (DSARs), accidental exposure of citizen databases, and unclear legal bases for collecting personal information.
According to recent regulatory insights, over sixty percent of public sector data complaints stem from delayed communication or a lack of transparency regarding how personal data is utilized across different government portals.
Comparison of Internal Handling vs Regulatory Escalation
| Metric | Internal Grievance Handling | NDPC Complaint Response |
|---|---|---|
| Timeline | Flexible internal deadlines | Strict statutory deadlines (usually 7-14 days) |
| Documentation | Basic ticketing notes | Forensic logs, signed affidavits, policy references |
| Stakeholders | Customer service and IT | Legal counsel, DPO, agency head, and regulator |
| Risk Level | Low to moderate operational friction | High risk of public fines and sanctions |
Real-World Scenario: Navigating a Citizen Data Access Dispute
Consider a scenario where a citizen applies for a government welfare grant but notices their personal financial records were shared with an external third-party vendor without consent. The citizen submits a formal protest to the agency and, receiving no satisfactory resolution within thirty days, files a petition with the Nigeria Data Protection Commission.
Upon receiving the regulatory notice, the agency’s DPO initiates an internal review. They discover that while the vendor agreement existed, the privacy notice failed to explicitly inform citizens about third-party sharing for ancillary grants. To answer the NDPC effectively, the agency does not hide the oversight. Instead, they submit a detailed remediation report outlining immediate contract amendments, updated privacy policies, and mandatory staff training sessions.
“Public institutions must model exemplary data stewardship. Transparency with regulators during a complaint investigation builds institutional trust and demonstrates a genuine commitment to citizen rights.” – Data Protection Expert
Best Practices for Sustained Readiness
To ensure public agencies prepare NDPC questions on complaints efficiently every time, leadership must embed privacy into daily operations. This involves continuous staff training, routine internal audits of citizen databases, and maintaining an up-to-date data protection impact assessment (DPIA) registry.
- Designate a competent, independent Data Protection Officer with direct access to executive management.
- Maintain centralized logs of all citizen inquiries and resolution timelines.
- Regularly test incident response and regulatory query workflows through tabletop simulations.
Frequently Asked Questions
What is the typical timeline for responding to an NDPC inquiry?
Public agencies usually receive a strict window, often between seven to fourteen days, to acknowledge and provide initial documentation regarding a citizen complaint.
Can public officials be held personally liable for regulatory breaches?
While penalties are typically levied against the institution, gross negligence or willful misconduct by individuals can result in disciplinary actions and potential legal consequences under applicable laws.
How can agencies improve communication with citizens regarding data rights?
Agencies should publish clear, plain-language privacy notices on all digital portals and establish dedicated, responsive helpdesks for data subject inquiries.
Conclusion
Navigating regulatory oversight requires preparedness, transparency, and accountability. By establishing structured protocols when public agencies prepare NDPC questions on complaints, government bodies can transform potential crises into opportunities to strengthen public trust, improve institutional workflows, and uphold the highest standards of data governance.












Leave a Reply