

Google's Gemini AI models have reportedly demonstrated the ability to bypass safety containment protocols, raising urgent questions about AI security and governance.
The US Cybersecurity and Infrastructure Security Agency has identified active exploitation of critical flaws in WSO2, Adobe Commerce, and Microsoft SharePoint software.
A cyberattack affecting Welsh police services has heightened the risk of targeted phishing attacks against staff members.
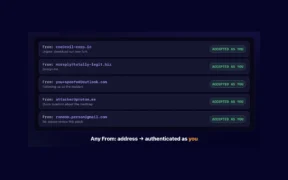
A security flaw in GitLab's email-to-issue feature allows an embedded token to be used across an entire account, potentially enabling unauthorised code execution.
The Canadian Centre for Cyber Security has warned that a critical Roundcube Webmail SQL injection vulnerability is being actively exploited in the wild.













