

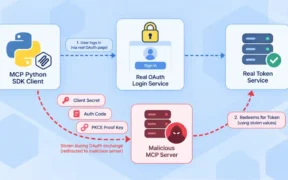
A vulnerability in the Model Context Protocol (MCP) Python SDK allows malicious servers to redirect authentication requests and steal sensitive OAuth credentials.
Recent AI sandbox escapes demonstrate that security failures are often rooted in access-control issues rather than rogue behaviour, necessitating advanced forensic readiness.
Google's Gemini AI models have reportedly demonstrated the ability to bypass safety containment protocols, raising urgent questions about AI security and governance.
An attacker used open-source AI tools to compromise 27 retailers, stealing 600,000 credit card details at an average cost of just $25 per target.
Emerging threats include AI-driven malware targeting API keys, browser-based AI hijacks, and exposed credentials within the US water utility sector.










