



What the NDPC Means for Fintech Companies Handling Personal Data

Share
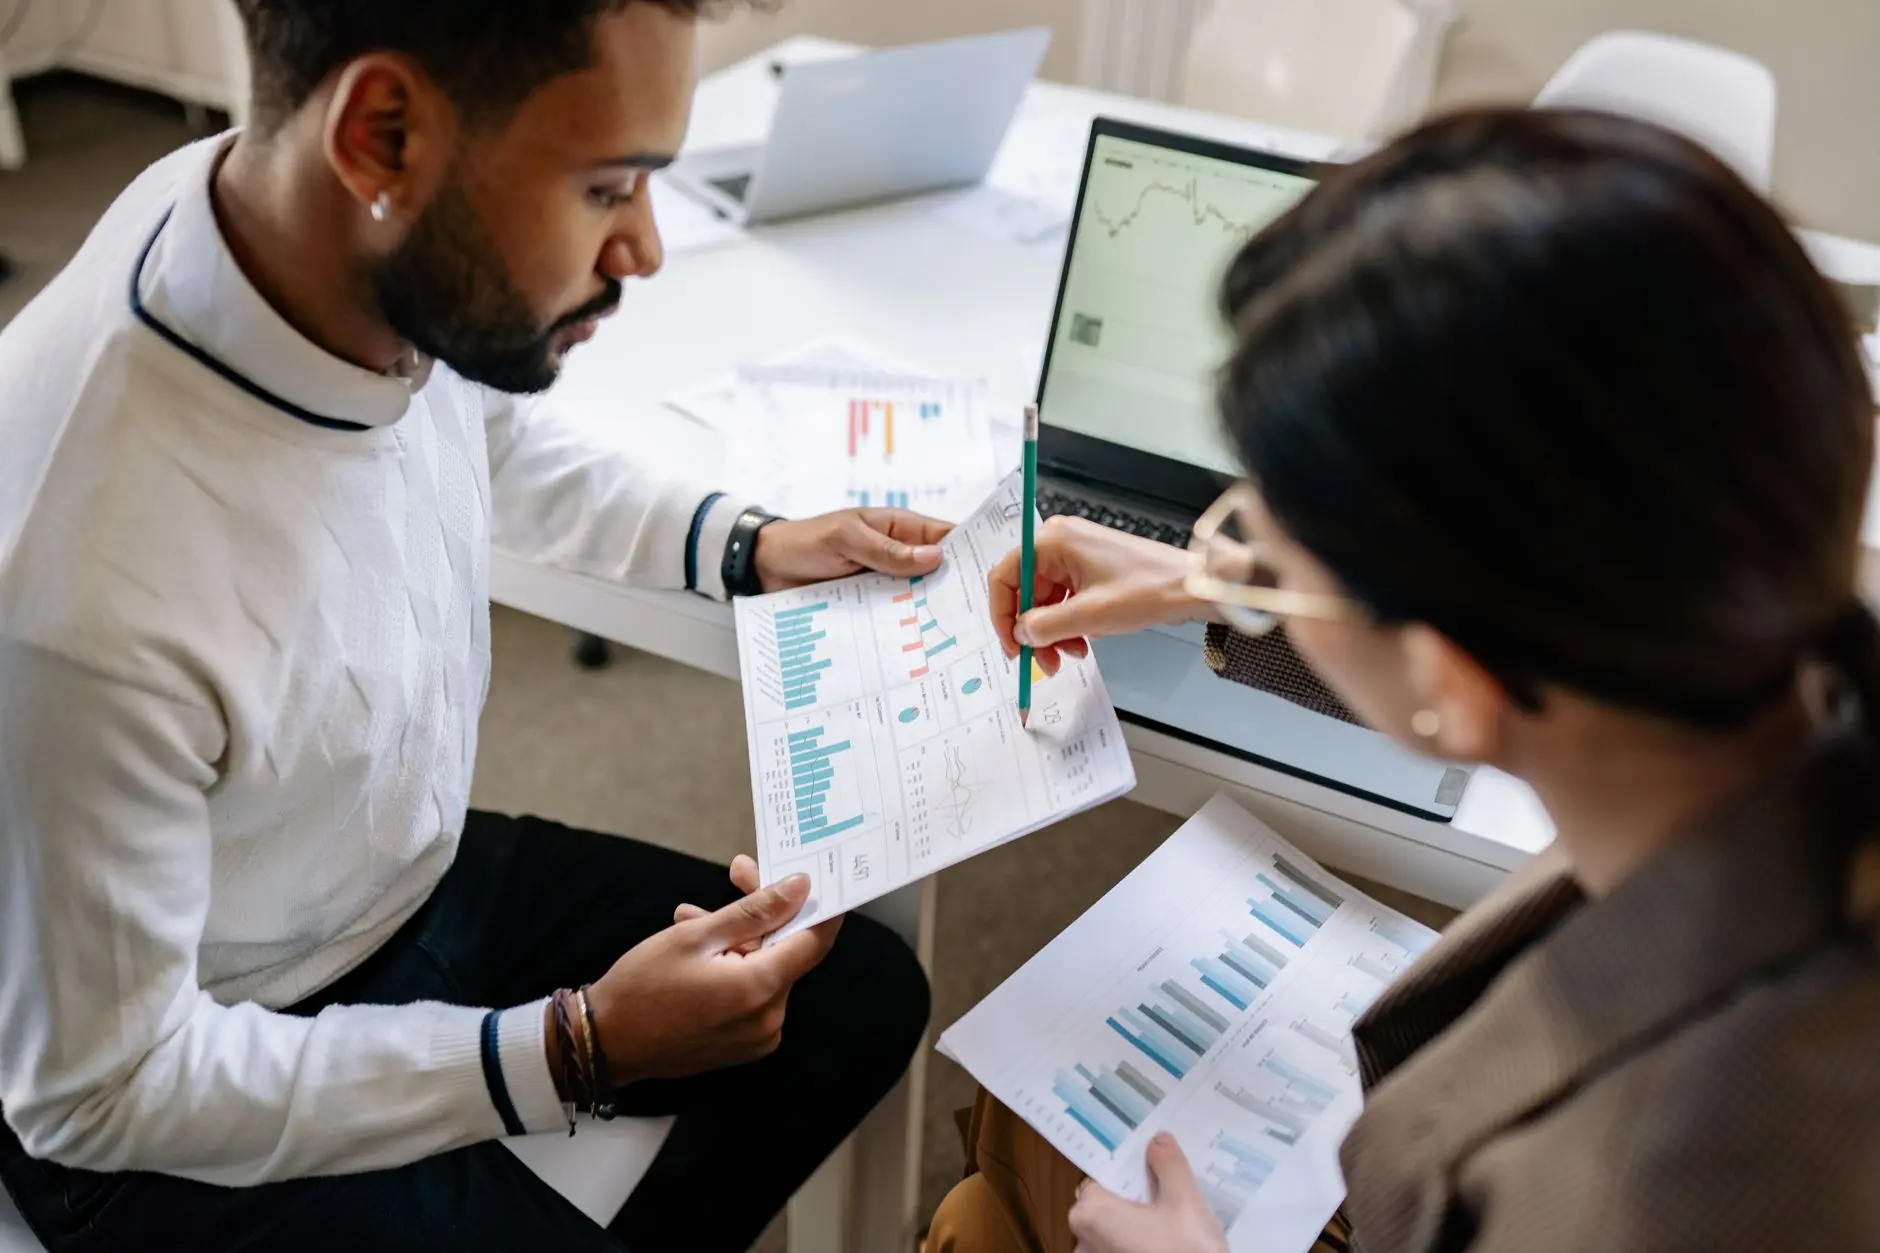
Understanding the Regulatory Mandate for Financial Technology
Financial technology startups and established digital lenders process millions of sensitive transactions daily. From credit scoring algorithms to instant loan disbursements, these platforms gather immense volumes of consumer details. However, operating in this sector requires more than innovative software; it demands strict adherence to regulatory frameworks. This is where understanding what the NDPC Means fintech Handling Personal data becomes critical for founders and compliance officers alike.
The Nigeria Data Protection Commission (NDPC) serves as the primary regulatory body overseeing privacy compliance and data security practices. For fintech operators, this means moving away from informal data handling toward institutionalized accountability. Protecting user profiles is no longer just a technical preference or a nice-to-have feature. It is a legal prerequisite for doing business in the digital economy.
Core Obligations Under the NDPC Framework
Regulatory scrutiny in the financial sector focuses heavily on transparency, lawful processing, and robust security safeguards. Fintech platforms often collect National Identification Numbers, biometric verifications, bank verification numbers, and transaction histories. Under current supervisory expectations, processing this information requires explicit consent and a clearly defined legal basis.
Furthermore, businesses must implement rigorous data protection principles such as data minimization and storage limitation. Keeping consumer logs indefinitely or repurposing financial analytics without explicit authorization exposes companies to severe financial penalties and reputational damage. Compliance teams must audit every database to ensure that data collection aligns strictly with the stated purpose of the financial service provided.
Operational Impact on Fintech Architecture
Engineering teams and product managers must integrate privacy by design directly into their application development lifecycles. When a user creates an account, requests a loan, or links a bank account, the underlying architecture must encrypt sensitive fields both in transit and at rest. Security misconfigurations or unprotected application programming interfaces often lead to accidental exposure.
Consider a digital lending platform that stores unencrypted user identification documents in an open cloud storage bucket. Under the oversight of the NDPC, such an oversight constitutes a severe violation of data security mandates. Regulatory authorities expect continuous monitoring, regular vulnerability assessments, and prompt incident response protocols to mitigate emerging threats.
| Compliance Area | Fintech Requirement | Potential Risk |
|---|---|---|
| Consent Management | Explicit, granular opt-in | Regulatory fines and user trust loss |
| Data Security | End-to-end encryption & access controls | Data breaches and legal liability |
| Data Subject Rights | Mechanisms for access and deletion | Failure to honor legal consumer requests |
| Vendor Management | Third-party risk assessments | Upstream data leaks via cloud vendors |
Empowering Consumers and Upholding Rights
A major focus of modern privacy regulation is the empowerment of data subjects. Fintech customers retain the right to know how their profiles are processed, request corrections, or demand the deletion of their information when accounts are closed. Implementing self-service portals where users can manage their preferences helps organizations maintain transparency.
According to the Nigeria Data Protection Commission, fostering a culture of compliance protects both the financial ecosystem and individual consumers from identity fraud and unauthorized profiling. Companies that build user-friendly rights management workflows frequently see higher customer retention and stronger market trust.
Actionable Steps for Compliance Teams
Navigating these regulatory demands requires a structured, multi-departmental approach. Legal, engineering, and customer support teams must collaborate to close existing compliance gaps. Consider implementing the following checklist:
- Conduct Comprehensive Audits: Map every data flow from initial collection to final deletion across all product lines.
- Update Privacy Policies: Ensure terms of service and privacy notices are written in clear, accessible language rather than dense legal jargon.
- Appoint Qualified Officers: Designate a dedicated data protection officer to manage regulatory communications and internal compliance monitoring.
- Train Employees: Regularly educate staff on secure handling practices, phishing awareness, and prompt incident escalation.
Frequently Asked Questions
Does the NDPC apply to foreign fintech apps operating locally?
Yes. Any platform targeting or processing personal information of individuals within the jurisdiction must comply with local regulatory standards, regardless of where the company is incorporated.
What are the financial consequences of non-compliance?
Penalties vary depending on the severity of the infraction, the volume of affected users, and the organization’s willingness to remediate identified security vulnerabilities.
Conclusion
Ultimately, what the NDPC means for fintech handling personal data is a transition toward sustainable, trust-based innovation. By embedding robust security controls, respecting consumer rights, and maintaining transparent data practices, financial technology companies can safeguard their operations against regulatory penalties while securing long-term growth in a competitive digital market.








Leave a Reply