



A SIMple Privacy Checklist for SMEs Handling Biometric Data

Share
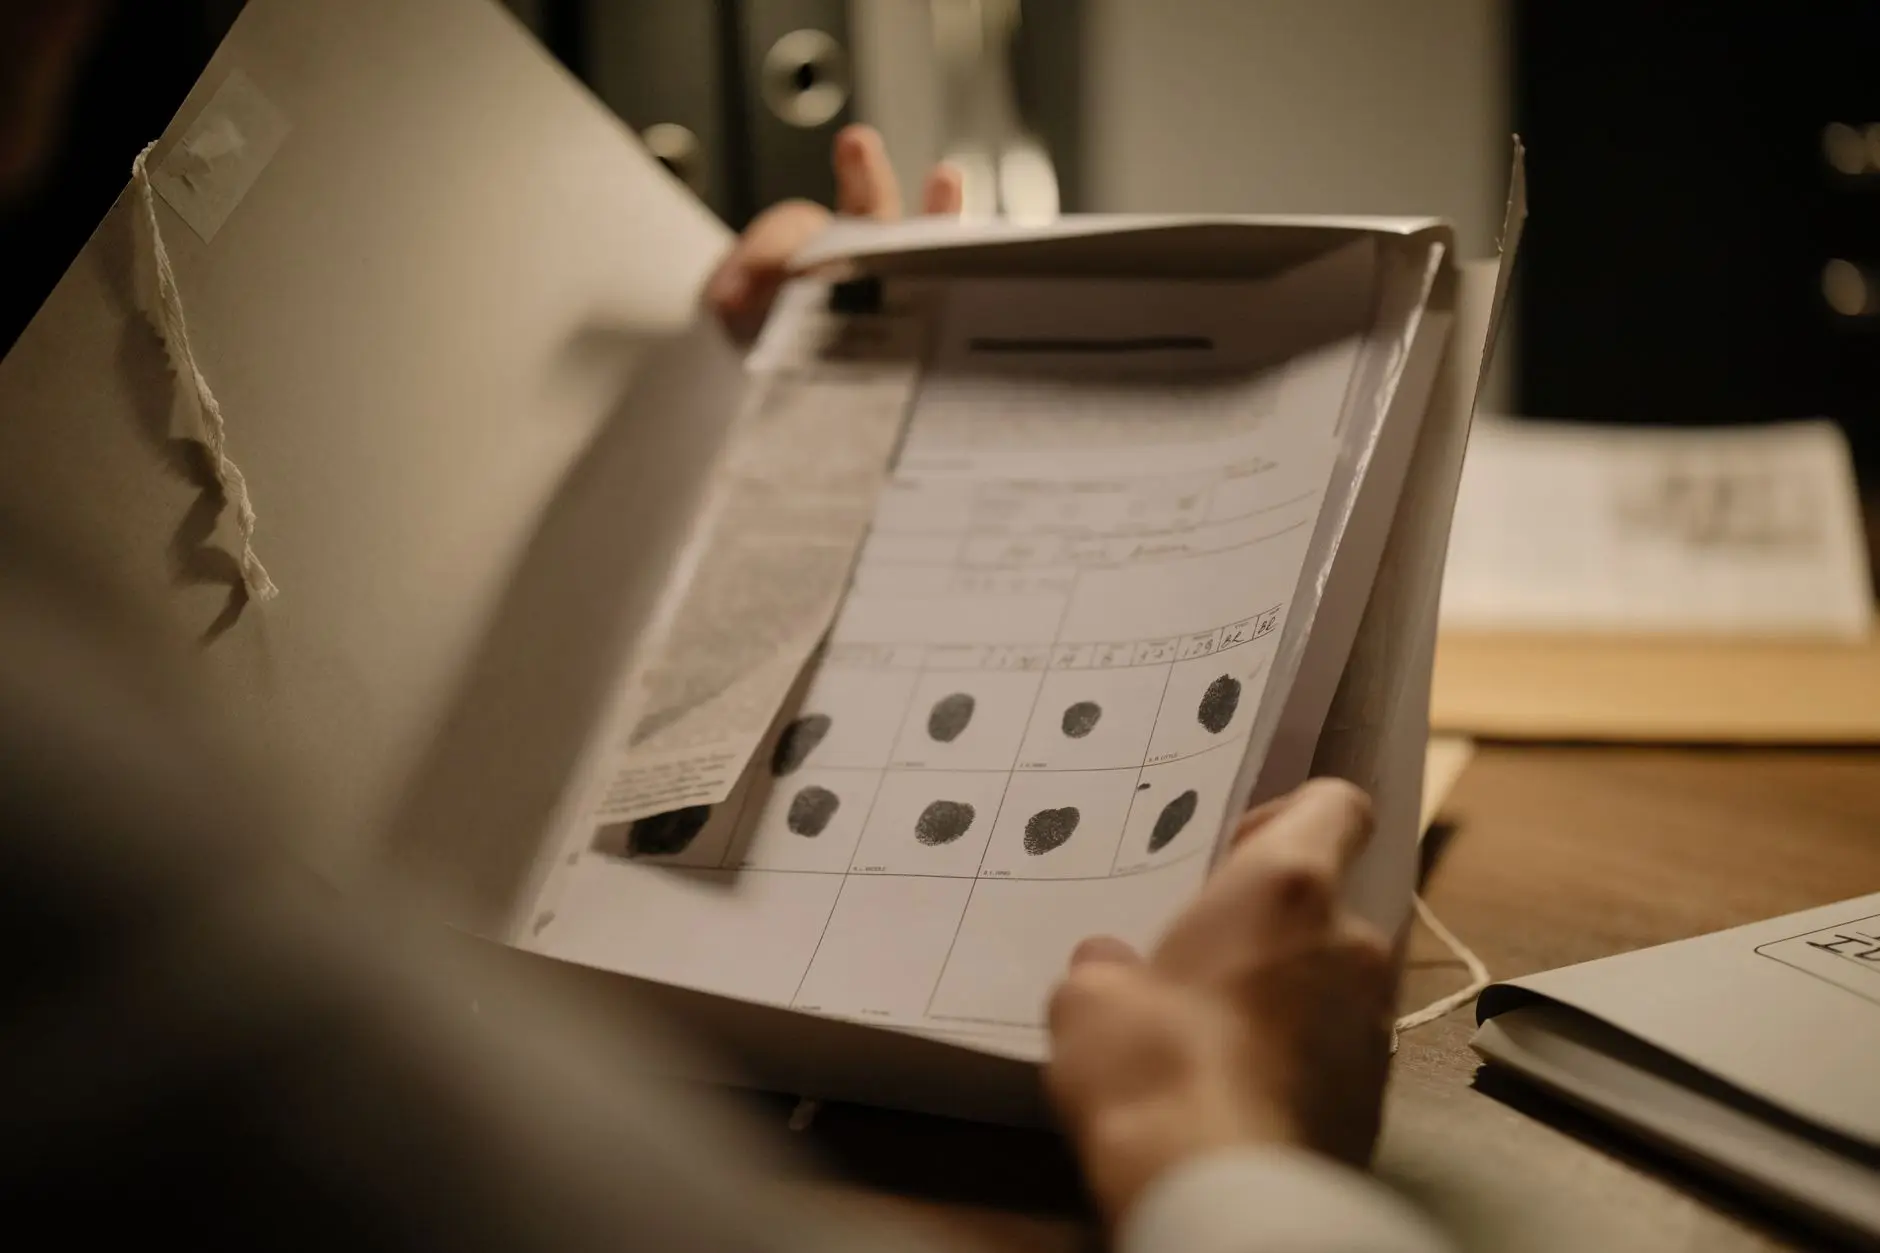
Biometrics—the measurement and statistical analysis of people’s unique physical and behavioral characteristics—have moved from high-security government facilities to the local office. From fingerprint scanners for timekeeping to facial recognition for building entry, SMEs are increasingly adopting these technologies for their perceived convenience. However, biometric data is immutable; if a password is stolen, you can reset it. If a fingerprint is leaked, that individual’s data is compromised for life.
Understanding the High Stakes of Biometrics
For small and medium-sized enterprises (SMEs), biometric data represents a unique class of sensitive information. Unlike a credit card number or a residential address, biometric identifiers cannot be changed if a breach occurs. Regulators globally, from the EU under GDPR to various state laws in the US, treat this data with extreme scrutiny. As noted by the IAPP, the legislative landscape is rapidly evolving, often imposing strict notice and consent requirements on private entities.
A Practical Checklist for SMEs Handling Biometric Data
Before deploying any system that collects fingerprints, retina scans, or facial geometry, follow this data protection roadmap to minimize risk and ensure regulatory alignment.
- Necessity Assessment: Does your business truly need biometric data? If a PIN code or physical badge achieves the same goal, avoid the legal burden of collecting biometrics entirely.
- Explicit Informed Consent: Ensure you provide a clear, written notice to employees or customers explaining exactly what data is collected, how long it is stored, and the purpose of collection.
- Data Minimization: Store only the mathematical representation (the template) of the biometric, never the raw image. If the system is compromised, a mathematical hash is significantly harder to reverse-engineer than an actual photo of a face or print.
- Encryption Standards: Ensure that all stored biometric templates are encrypted using industry-standard protocols, both at rest and in transit.
- Retention Policies: Establish a strict sunset clause. Delete biometric data immediately after the purpose for collection has expired (e.g., when an employee leaves the company).
- Access Control: Implement the principle of least privilege. Only essential personnel should have access to the databases where biometric templates reside.
Comparing Biometric Storage Methods
| Method | Risk Level | Recommendation |
|---|---|---|
| Raw Image Storage | Extreme | Avoid at all costs |
| Local Template Storage (Device Only) | Low | Preferred |
| Centralized Database Storage | High | Requires rigorous encryption and auditing |
Real-Life Scenario: The Timekeeping Pitfall
Consider a retail SME that implemented a fingerprint-based time-clock system. The vendor promised high security but failed to disclose that the biometric images were being uploaded to a third-party cloud server in an unencrypted format. When the vendor suffered a breach, the SME became the primary target for lawsuits because they had failed to conduct a vendor compliance audit. The lesson here is clear: you are responsible for the biometric data you collect, regardless of which third-party provider you use.
The Human and Legal Implications
For digital platforms and businesses, biometric processing is not just a technical challenge; it is a profound trust issue. If your customers or employees feel their physical identity is being monitored or insecurely stored, the loss of brand equity can be more damaging than a potential fine. Businesses must adopt a privacy-by-design approach where security is baked into the architecture, not added as an afterthought.
Frequently Asked Questions
Why is biometric data treated differently than passwords?
Passwords can be changed; biometric markers such as irises, fingerprints, and facial geometry are permanent. The risk of identity theft is permanent if this data is compromised.
Can I store biometric data on a mobile device?
Storing biometrics locally on a secure enclave within a device is generally safer than centralizing them on a server, provided the device is managed and encrypted.
What is the biggest mistake SMEs make?
The most common error is failing to obtain informed, opt-in consent before the first scan occurs, often assuming that ’employment’ constitutes implied consent.
Conclusion
Successfully navigating the complexities of biometric data requires a shift in mindset. It is not just about adopting the latest security hardware; it is about respecting the sanctity of unique human identifiers. By using this checklist for SMEs handling biometric data, you can build a more secure, compliant, and trustworthy operation. Prioritize data minimization and transparency, and ensure your third-party vendors are held to the same high standards you apply to your own internal data protection policies.











Leave a Reply