



Best Practices for Managing Health Data in SMEs

Share
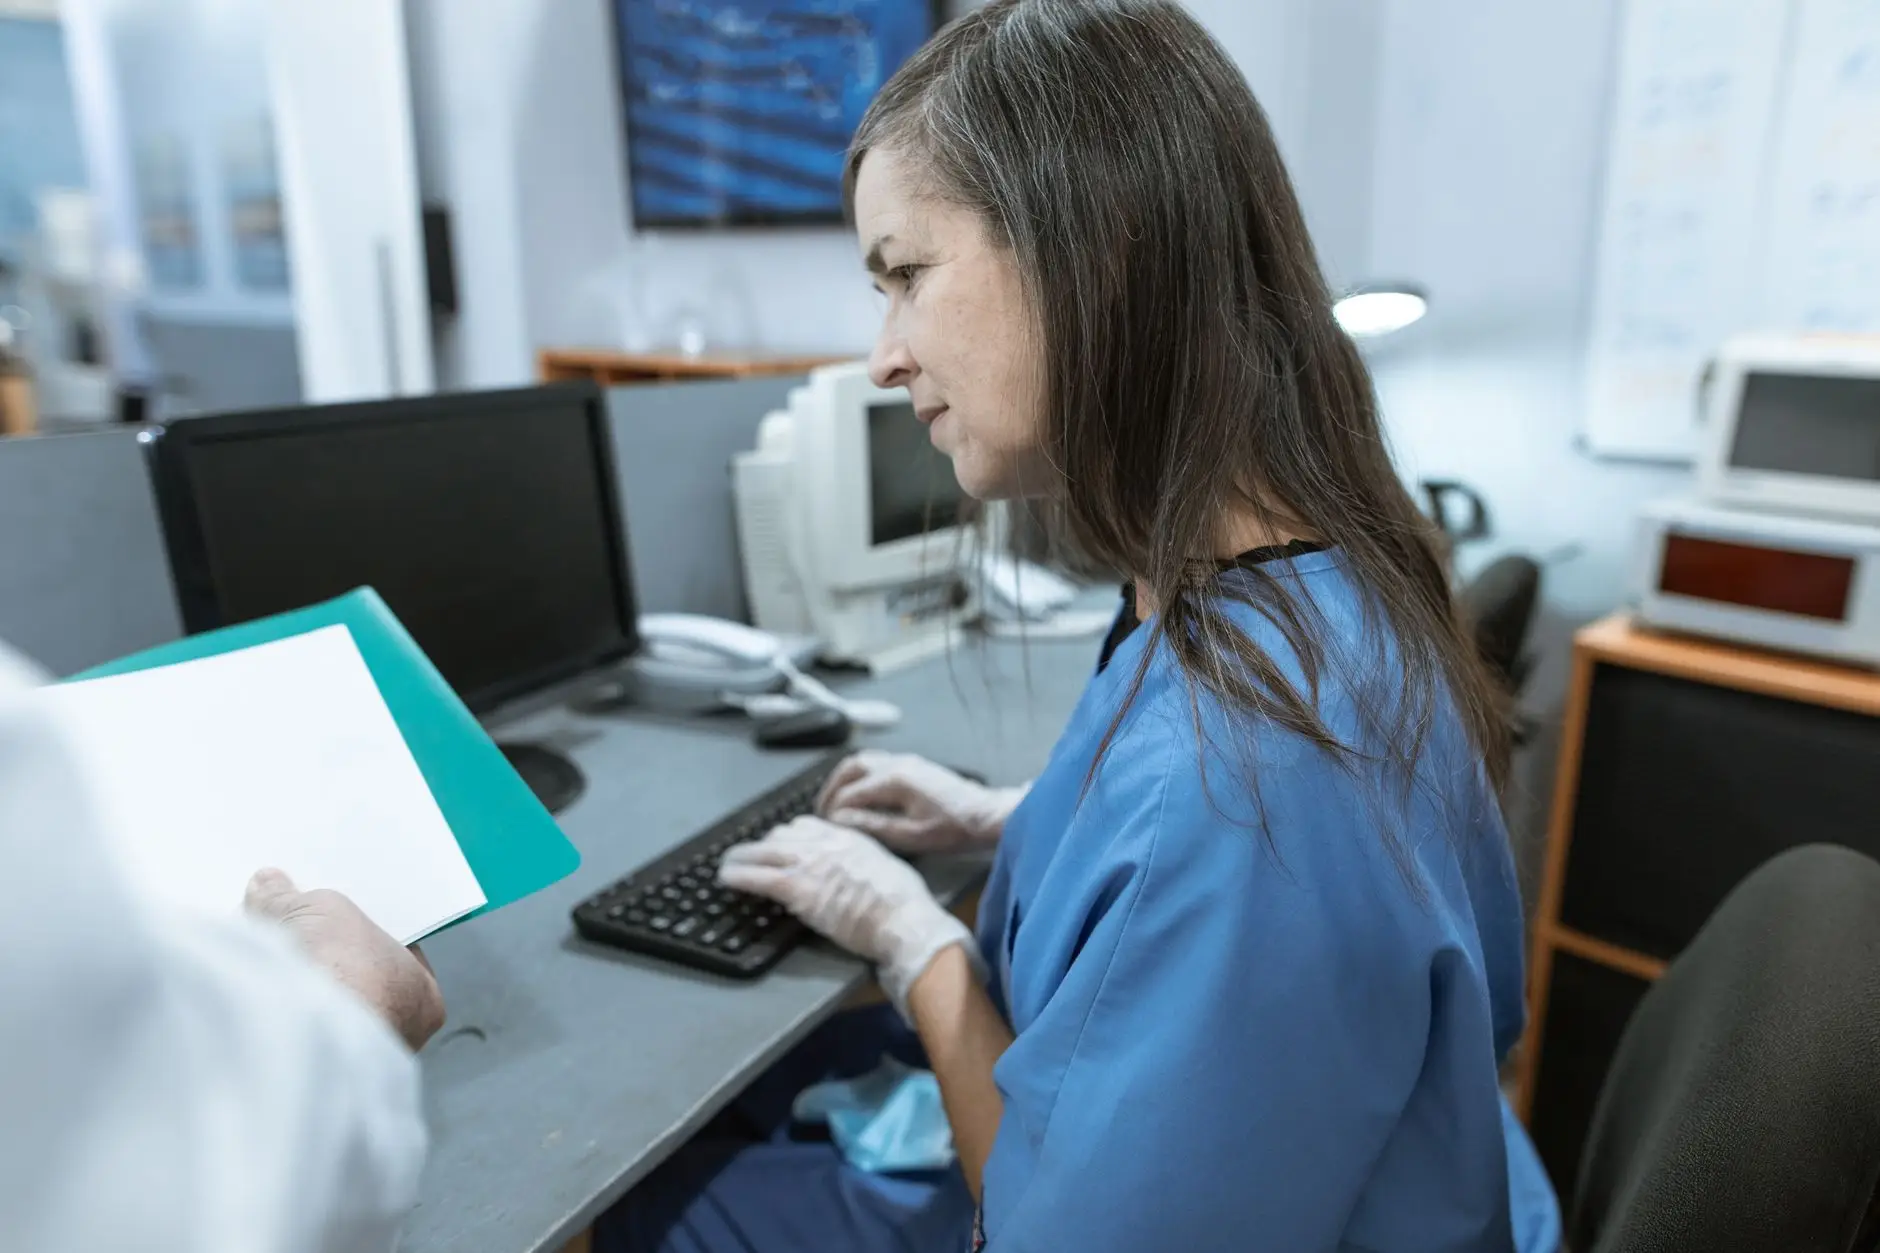
Small and medium enterprises (SMEs) often mistakenly believe they are too small to be targeted by cybercriminals or audited by regulators. When your organization handles sensitive health information, this assumption is a liability. Health data is highly lucrative on the black market, making clinics, wellness apps, and diagnostic startups prime targets for data theft.
The Critical Nature of Health Data
Unlike financial data, which can be changed if compromised, health records are immutable. Once a patient’s medical history is leaked, that damage is permanent. Managing this data requires a shift from viewing privacy as a legal hurdle to viewing it as a core service component. Implementing Best Practices Managing Health SMEs is not just about avoiding fines; it is about protecting the patient-provider relationship.
Foundation of a Robust Privacy Program
To secure sensitive data, leadership must move beyond perimeter defense. A holistic approach involves administrative, physical, and technical safeguards. For those beginning this journey, reviewing our guide on data protection fundamentals is a necessary first step.
Administrative Safeguards
Every employee, regardless of their role, is a potential security gatekeeper. Regular training programs must address the specific risks associated with medical data, such as accidental disclosure or phishing attempts targeting login credentials for Electronic Health Record (EHR) systems.
Technical Security Measures
Encryption should be the standard for both data at rest and data in transit. If an SME experiences a hardware theft or a network intrusion, encrypted data remains unusable to the attacker. Access control is equally vital; apply the principle of least privilege, ensuring employees access only the information necessary for their specific tasks.
| Security Tier | Actionable Strategy |
|---|---|
| Infrastructure | Use multi-factor authentication (MFA) everywhere. |
| Access | Regularly audit user accounts and delete inactive ones. |
| Storage | Implement end-to-end encryption for all patient files. |
| Response | Document a clear compliance incident plan. |
Real-World Risk: The Phishing Scenario
Consider a small physical therapy clinic that fell victim to a business email compromise (BEC) attack. An administrator received a fake email that appeared to be from their EHR software provider requesting a password reset. By entering their credentials on a spoofed site, the admin gave attackers full access to thousands of patient records. This led to a major data breach, significant recovery costs, and a loss of local reputation.
As noted by the U.S. Department of Health and Human Services, HIPAA security guidance emphasizes that security is a continuous process, not a one-time setup. SMEs must perform regular risk assessments to identify vulnerabilities before attackers do.
Managing Third-Party Risk
Many SMEs outsource their billing, cloud storage, or patient communication platforms. These third-party vendors are often the weakest link in your supply chain. You remain legally and ethically responsible for the data you collect, even when it sits on a vendor’s server. Always conduct due diligence on vendors, review their security certifications, and ensure your data processing agreements are legally sound.
Key Action Steps for SMEs
- Inventory your data: You cannot protect what you do not know you have. Document where all health data is stored.
- Automate backups: Ensure backups are encrypted and stored offline to protect against ransomware.
- Adopt a clean-desk policy: Physical files, tablets, and sticky notes with passwords are common vectors for data leakage in small clinics.
- Update software: Never ignore security patches for your EHR or operating systems.
Frequently Asked Questions
Do SMEs really face the same regulatory risks as large hospitals?
Yes. Data protection laws generally apply to the data, not the size of the entity. If you handle health information, you are obligated to protect it under applicable laws like HIPAA, GDPR, or national equivalent regulations.
How can we afford enterprise-grade security?
Security is not just about expensive software. It is about policy and discipline. Using MFA and enforcing strong password practices costs very little but significantly reduces your risk profile.
Conclusion
The responsibility of managing health data is significant, but it is manageable when approached with a structured plan. By embedding Best Practices Managing Health SMEs into your daily operations, you protect your patients and secure your business longevity. Security is not an expense; it is the infrastructure of trust that allows your organization to thrive in a digital-first economy.











Leave a Reply