



ShinyHunters Claims FBI Breach and Theft of Agent Data

Share
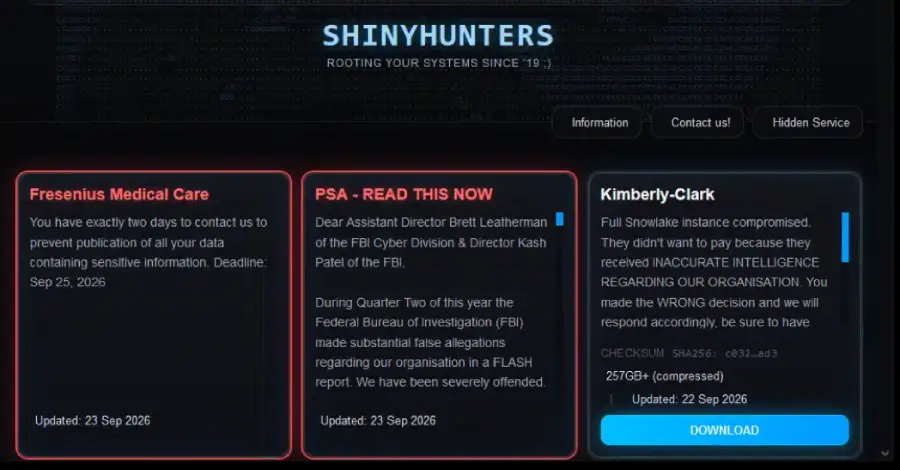
The cyber extortion group known as ShinyHunters has claimed to have breached the U.S. Federal Bureau of Investigation (FBI), alleging the theft of sensitive information belonging to current and former employees.
In a statement released on Tuesday, the group asserted that it holds sensitive data pertaining to nearly all FBI agents, as well as individuals who have submitted job applications to the agency. The attackers claimed to have compromised several internal services, including Human Resources (HR), Criminal Justice (CJ), and Medlink.
Exploitation of Oracle PeopleSoft Vulnerability
A spokesperson for ShinyHunters stated that the group exploited a new zero-day vulnerability in Oracle PeopleSoft to achieve remote code execution (RCE). This exploit reportedly allowed the attackers to deface the FBI’s recruitment website with a banner claiming the site had been seized.
While specific technical details regarding the new PeopleSoft flaw have not yet been disclosed, the group has a history of weaponising similar vulnerabilities. In June 2026, ShinyHunters utilised CVE-2026-35273 to penetrate enterprise networks for extortion purposes.
FBI Response and Retaliatory Motive
The FBI has acknowledged the reports, stating it is aware of claims regarding unauthorised activity affecting FBIjobs.gov and is currently investigating the matter.
ShinyHunters suggested the attack was a retaliatory response to a May 2026 public service announcement (PSA) that detailed the group’s targeting of the Canvas Learning Management System (LMS) and urged victims against paying ransoms. The group described the government’s previous communications as “substantial false allegations” and “disinformation.”
Expert Analysis on Threat Actor Activity
Industry experts suggest the claim represents a significant escalation in the tension between law enforcement and cybercriminal organisations. Etay Maor, VP of threat intelligence at Cato Networks, described the move as “unusually provocative” and advised that it should be treated with seriousness.
Maor also noted that the timestamp on the group’s announcement might provide a clue regarding their location. If the timestamp reflects the group’s actual operating environment, it could suggest activity originating in Asia, though this remains unconfirmed.











Leave a Reply