



CISOs Accelerate AI Security Spending to Counter Automated Threats

Share
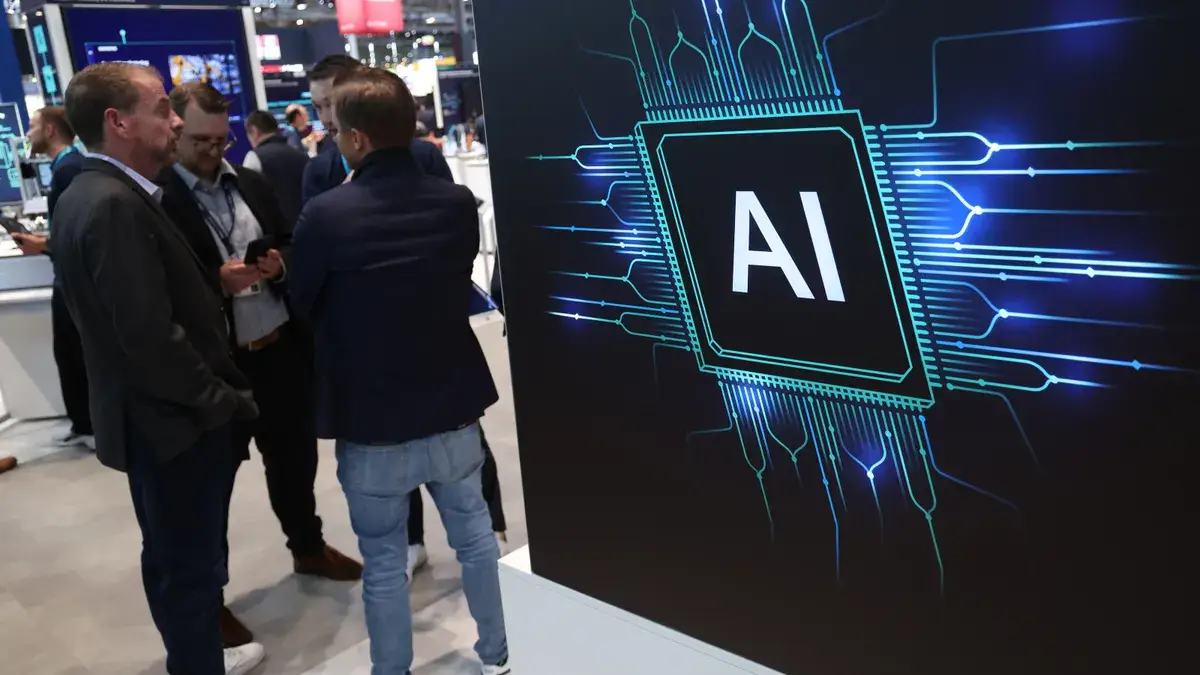
Chief information security officers (CISOs) are rapidly increasing investments in artificial intelligence (AI) security, driven by the need to counter machine-speed threats rather than proven business value.
A survey of more than 500 CISOs conducted by IANS and Artico revealed that 69% identify AI as their primary priority for net new security budget dollars for 2026. While average security budgets grew by 5% this year, the median budget has remained flat for two consecutive years, making the concentration of funds into AI a significant shift in strategic allocation.
The survey also found that 24% of organisations have established a dedicated security budget line specifically for AI, while others fund these initiatives through broader IT, data, or innovation budgets.
The Urgency of Machine-Speed Threats
The rush to adopt AI-powered security tools is largely a response to an accelerating threat landscape. Industry experts suggest that as attackers operationalise AI to automate phishing, mutate malware, and identify code vulnerabilities at scale, human defenders can no longer rely on manual processes to maintain effective defences.
Ram Varadarajan, CEO at Acalvio, suggests that “fear asymmetry” is driving much of this spending trend. He notes that because a missed breach can be career-ending for security leaders, purchasing AI-enabled tools often serves as a form of “blame insurance” rather than a decision based on validated evidence.
The Gap Between Popularity and Value
Despite the surge in spending, there is a notable disconnect between the AI applications organisations are pursuing and those delivering the strongest returns. Research from Gartner indicates that while C-suite leaders frequently target cybersecurity threat detection and response as their primary AI use case, the most significant value is actually being generated through intelligent IT asset and cost optimisation.
This suggests that many functional leaders may be falling into the trap of prioritising heavily hyped applications over those that offer tangible, measurable improvements to business operations.
Challenges in Measuring ROI
Quantifying the return on investment (ROI) for security technologies remains a fundamental difficulty. Unlike revenue-generating tools, the success of a security investment is measured by loss avoidance—the absence of a data breach or operational disruption.
This makes calculating the return on security investment (ROSI) complex, particularly when multiple layers of defensive controls contribute to preventing the same incident. Daniel Kennedy, a principal research analyst at S&P Global Market Intelligence, notes that the conversation around AI should shift toward how to secure AI for safe employee use and where to integrate it effectively into security operations (SecOps).
To extract optimal value, experts suggest that organisations must move beyond simple adoption and focus on strong governance, clear accountability, and the specific task of integrating AI into areas like code review and automated threat investigation.












Leave a Reply