



AI-Driven Nation-State Cyber Threats Increasing Risk for Private Sector

Share
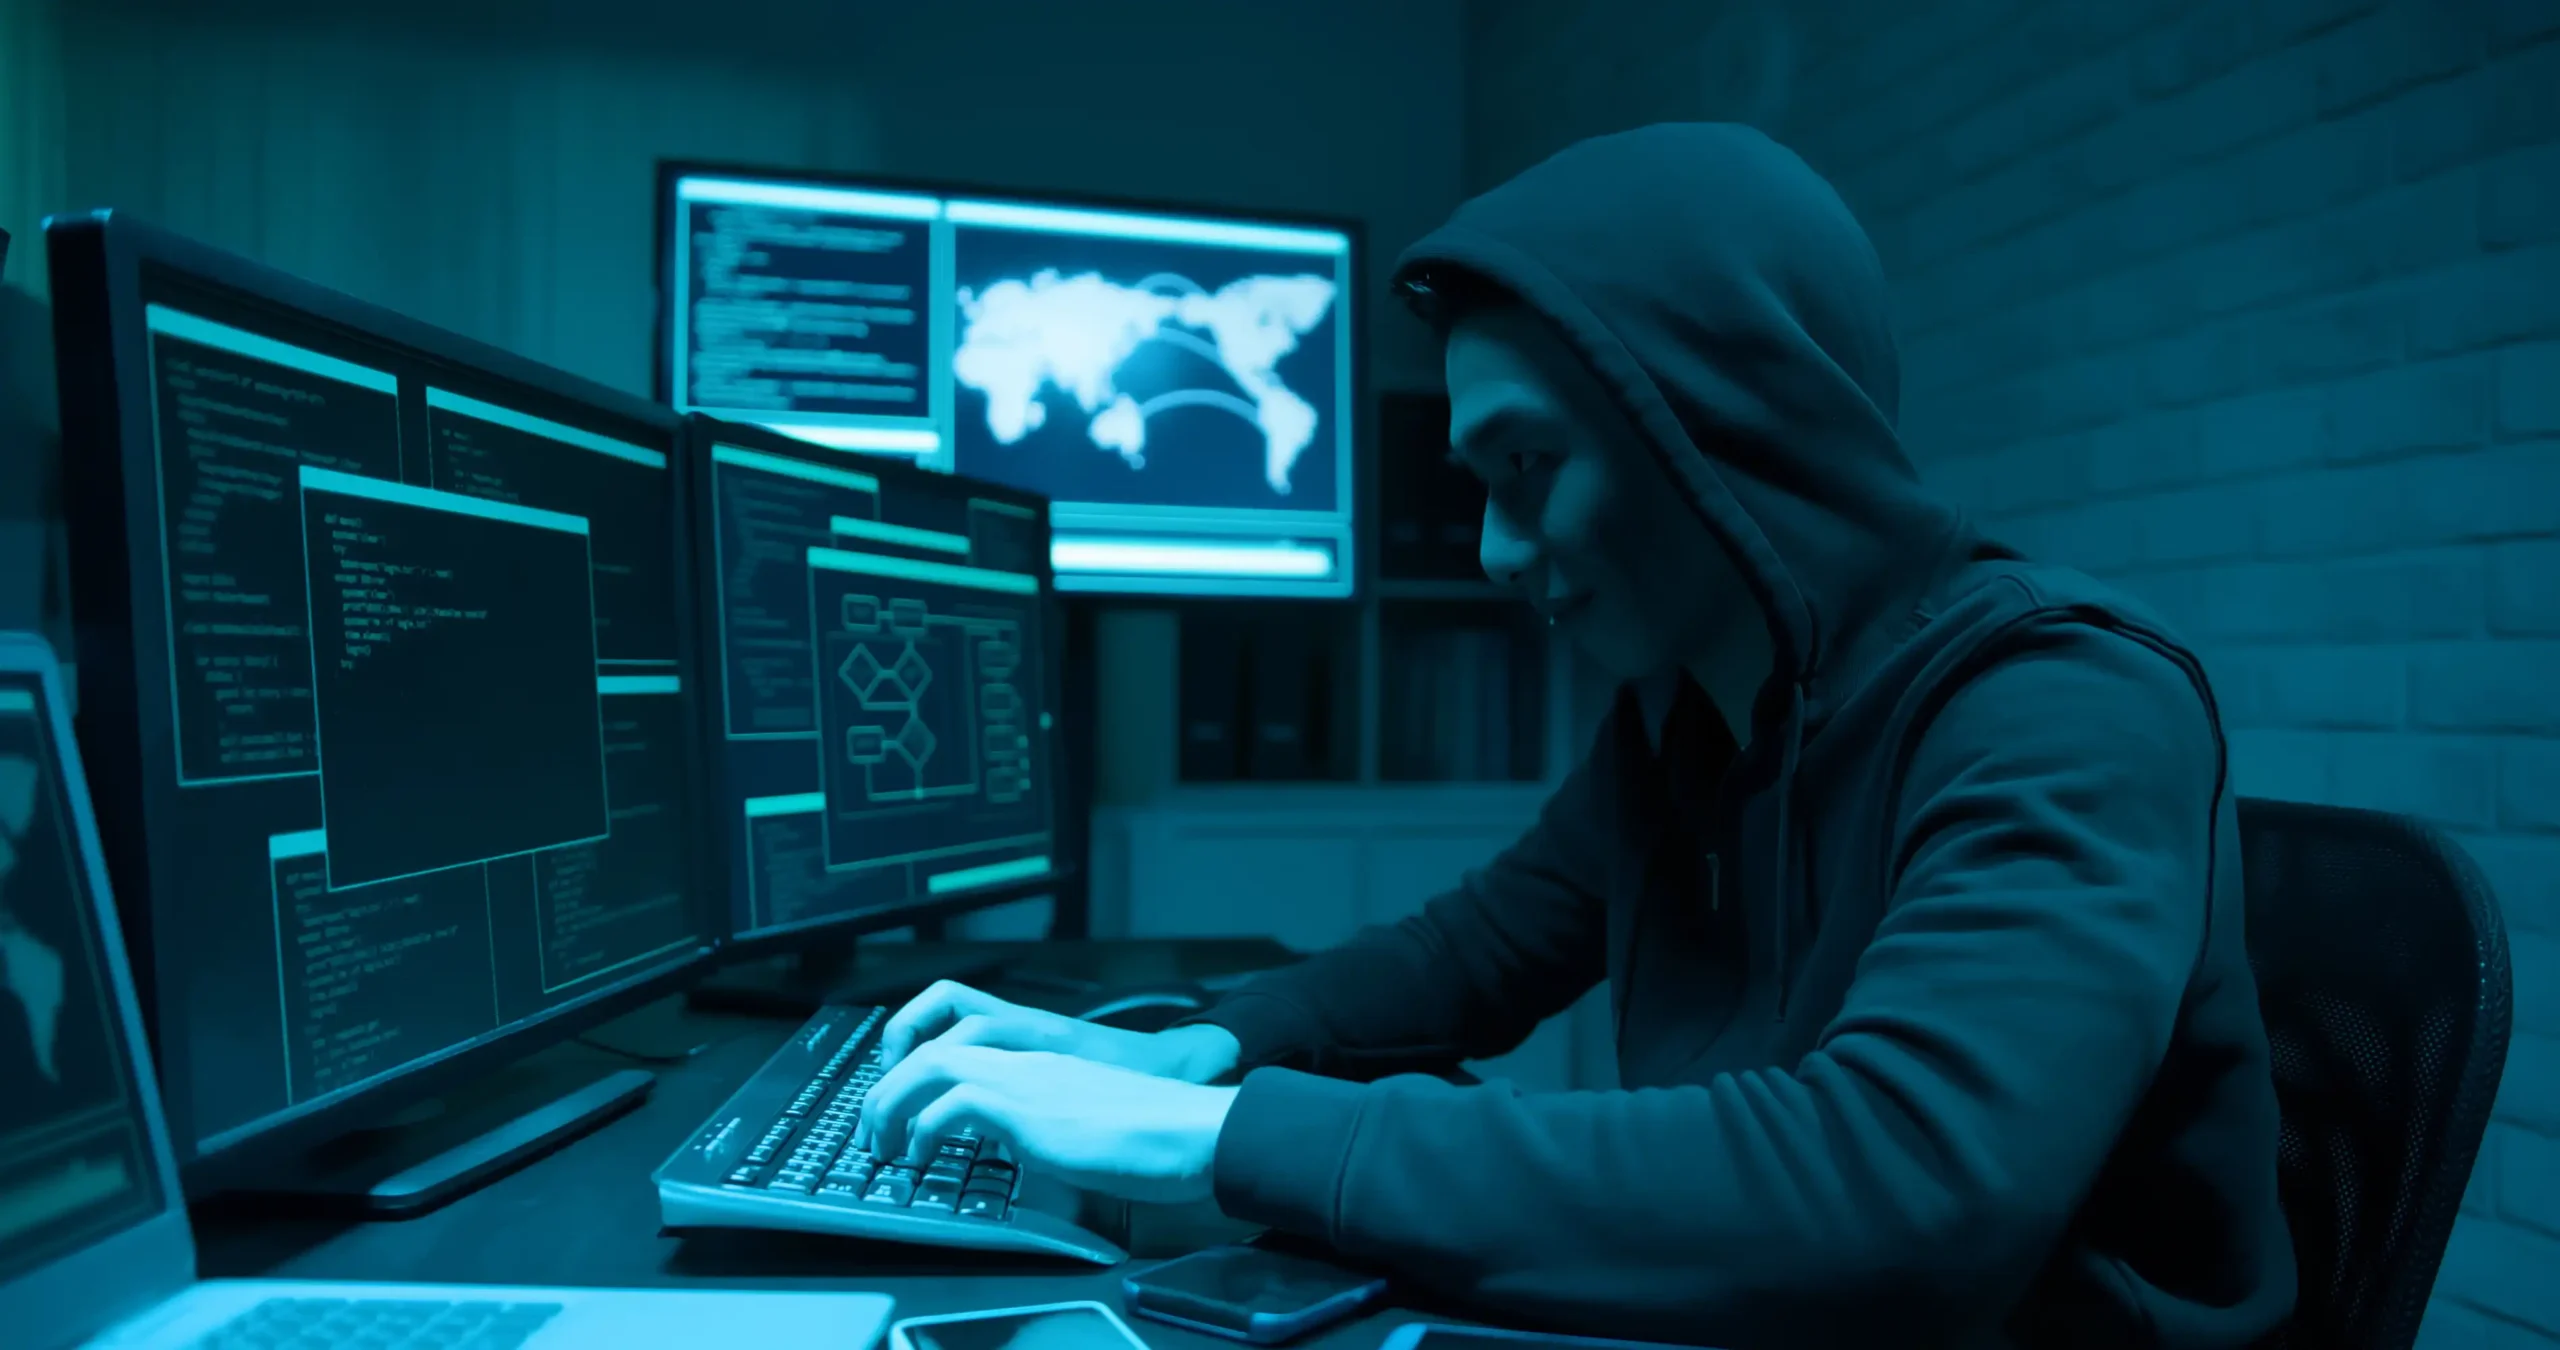
The rapid integration of artificial intelligence (AI) into the toolkits of nation-state actors is fundamentally reshaping the cyber threat landscape, forcing Chief Information Security Officers (CISOs) to treat geopolitical tensions as a core component of enterprise risk management.
As AI capabilities advance, the distinction between national security concerns and ordinary enterprise security risks is blurring. This shift is creating a fundamental tension between corporate defenders and government agencies; while CISOs typically aim to remove adversaries from networks immediately to mitigate liability, government responders often prefer to observe attackers to gather intelligence.
AI Accelerates Exploitation and Lowers Sophistication Barriers
AI is significantly increasing the speed at which threat actors can operate, compressing the window between vulnerability discovery and exploitation to mere seconds. This speed threatens to outrun traditional patch management processes.
The technology also lowers the threshold for sophisticated-looking attacks. Vikram Thakur of Symantec by Broadcom noted that AI enables even relatively amateurish cybercriminals to launch operations that mimic the sophistication of nation-state actors. This trend is compounded by the widespread availability of high-level, open-weight AI models originating from China.
According to Charles Carmakal of Mandiant, while predominantly autonomous intrusions remain relatively uncommon, AI-enabled activity is already present in a significant portion of current incident-response cases. Researchers at the Google Threat Intelligence Group also suggest that AI can assist attackers in troubleshooting technical problems, allowing them to pre-position themselves within organisational assets more effectively.
Unexpected Strategic Targets
Many organisations fail to recognise themselves as potential targets of adversarial nations. John Fokker, vice president of threat intelligence strategy at Trellix, highlighted that even seemingly non-strategic industries can be targeted for intellectual property theft. For instance, Chinese threat actors have targeted greenhouse technology providers in the Netherlands to steal specialised expertise.
Because nation-state actors often operate in “stealth mode,” their presence can be difficult to detect compared to more “noisy” cybercriminal groups. This makes it harder for organisations to identify whether their research, contracts, or supply chains have made them strategically relevant to foreign powers.
Mitigating Nation-State Risk
To prepare for an era of increasingly agentic and AI-enabled attacks, security experts suggest several immediate actions for CISOs:
- Calibrate threat models: Organisations should prepare for greater speed and scale, as AI-enabled activity is already being observed in modern intrusions.
- Plan for operational compromise: Security leaders should conduct tabletop exercises that assume prolonged disruptions to critical infrastructure, such as power, telecommunications, or cloud services.
- Reduce the attack surface: Implementing core security controls, including zero trust architectures and multi-factor authentication (MFA), remains a vital defence against AI-driven attacks.
- Secure executive support: Resilience against nation-state actors requires C-suite and board-level authorisation for the necessary investment and cross-enterprise planning.
As the cyber front becomes more complex, the Cybersecurity and Infrastructure Security Agency (CISA) has called for a closer, “hand-in-glove” relationship between the federal government and private industry to protect critical infrastructure.









Leave a Reply