



Trezor Confirms Malicious Hardware Implants in Safe 5 Wallets

Share
Trezor has confirmed that malicious hardware implants were discovered in three Safe 5 cryptocurrency wallets sold through the Southeast Asian reseller CryptoBilis.
The hardware manufacturer identified the compromise following an investigation into a suspected implant reported by a customer in October. Trezor engineers later identified two additional compromised devices after examining photographs provided by other owners.
All confirmed compromised devices were purchased from CryptoBilis between 20 August and 23 September 2026. While 48 customers have contacted the company regarding potential tampering, Trezor stated that no loss of funds has been reported as a result of these implants to date.
Technical Analysis of the Implant
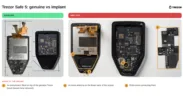
The malicious hardware consists of an unauthorised circuit board installed between the Safe 5 main board and the display. This placement allows the implant to monitor screen activity without modifying the device’s legitimate firmware or Secure Element.
The implant is designed to capture wallet recovery phrases and passphrases as they appear on the screen during wallet creation or restoration. Once the sensitive data is collected, the device encrypts the information and transmits it to an attacker-controlled server via a mobile cellular network. If a connection is unavailable, the implant retains the data and attempts to transmit it repeatedly until successful.
Firmware Fix and Security Warnings
On 11 November, Trezor released firmware version 2.13.1 to address the vulnerability. The update includes a protection mechanism designed to stop these specific implants from capturing data on devices running the new firmware.
However, Trezor cautioned that the update cannot protect recovery phrases that may have been captured by the implant before the firmware was installed. Consequently, the company advises anyone who purchased a Trezor wallet from CryptoBilis since March 2026 to transfer their cryptocurrency to a newly created wallet using a completely new recovery phrase.
Supply Chain Response
In response to these supply-chain attacks, Trezor has reduced its global reseller network by approximately 80%. The company is implementing stricter security requirements for its remaining partners, governing how devices are sourced, stored, and accessed.
Trezor is also offering replacement devices to customers who purchased a wallet from CryptoBilis since March 2026, including those whose devices have not been explicitly confirmed as compromised.











Leave a Reply