



Windows CLFS Zero-Day Exploit ‘SignDrop’ Achieves SYSTEM Privileges

Share
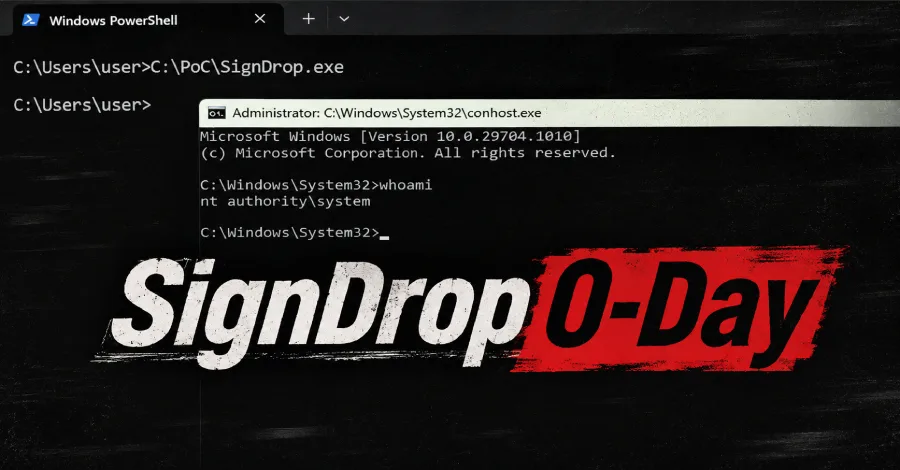
A new publicly released zero-day exploit, dubbed ‘SignDrop’, allows a local Windows user to escalate privileges to SYSTEM by leveraging a security feature within the Common Log File System (CLFS) driver.
The proof-of-concept (PoC) code targets a log-authentication mechanism introduced by Microsoft last year to bolster CLFS security. The exploit was released by a researcher operating under the pseudonym MSNightmare on GitHub, coinciding with Microsoft’s November security updates.
Microsoft has not yet publicly confirmed the claimed vulnerability, assigned a Common Vulnerabilities and Exposures (CVE) identifier, or released a patch.
Exploit Details and Impact
The SignDrop exploit abuses how the clfs.sys driver creates companion files (`.cnpf`) when a privileged process opens a specially crafted log file. The vulnerability hinges on path redirection, using object manager symbolic links to control where these companion files are created.
According to MSNightmare’s detailed write-up, a standard user can prepare a CLFS log and container with paths they control. When a privileged process subsequently opens this log, the driver creates the companion file within the privileged process’s security context, rather than the user’s. The exploit redirects this file creation to an attacker-chosen location, resulting in a SYSTEM-privileged file that a standard user can then modify.
The published PoC uses the Windows Defender antimalware service, triggered via its update interface, as the privileged process. MSNightmare noted that while Microsoft’s implementation is technically correct, the logic allows for abuse, which can be chained into a SYSTEM shell.
The exploit has been tested successfully on Windows 11 26H2, a Windows 11 26H2 Experimental build, and Windows Server 2025 Experimental. Systems are vulnerable if the CLFS authentication registry mode is set to 0 (enforced) or 1 (learning). Established installations typically default to enforcement, making them susceptible.
Independent Verification and Context
Sungyup Nam, head of research at Korean security firm 78researchlab, confirmed the exploit’s functionality in a published assessment. Heewon Song, from 78researchlab’s PurpleHound offensive content team, validated that SignDrop works, though noted it may not be reliably operational for widespread use. For the published chain to succeed, Defender must be enabled. An active exploit also makes the attack noticeable through altered User Account Control (UAC) prompts.
The CLFS driver has historically been a frequent target for privilege escalation attacks. Ten CLFS flaws are listed in CISA’s catalog of vulnerabilities known to have been exploited in attacks, including one used in ransomware campaigns in April 2025. To mitigate this, Microsoft introduced an authentication check for CLFS log files in October 2025 updates for Windows 11 25H2, 26H1, and Windows Server 2025.
MSNightmare has a history of discovering and releasing exploits targeting Windows and Defender. Previous Defender exploits, RoguePlanet (CVE-2026-50656) and ShieldBreak (CVE-2026-69414), were confirmed and patched by Microsoft. SignDrop, however, represents a different class of issue, targeting the CLFS driver’s authentication feature itself, rather than race conditions in Defender’s file handling.
Mitigation Advice
As no CVE or official advisory has been issued for SignDrop, and it is not yet listed in the CISA Known Exploited Vulnerabilities catalog, administrators are advised to monitor their systems.
Organisations can check their exposure by examining the CLFS authentication mode in the Windows registry at HKLM\SYSTEM\CurrentControlSet\Services\CLFS\Authentication. A ‘Mode’ value of 0 or 1 indicates potential exposure. While a value of 2 or 3 disables the mitigation and removes the system from the claimed attack surface, both MSNightmare and Microsoft’s own documentation warn against this, as it reopens memory corruption flaws the protection was designed to prevent.
Further details on the exploit and its mechanics are available on MSNightmare’s GitHub repository.










Leave a Reply