



How Law Firms Should Think About AI Governance Before Using AI Tools

Share
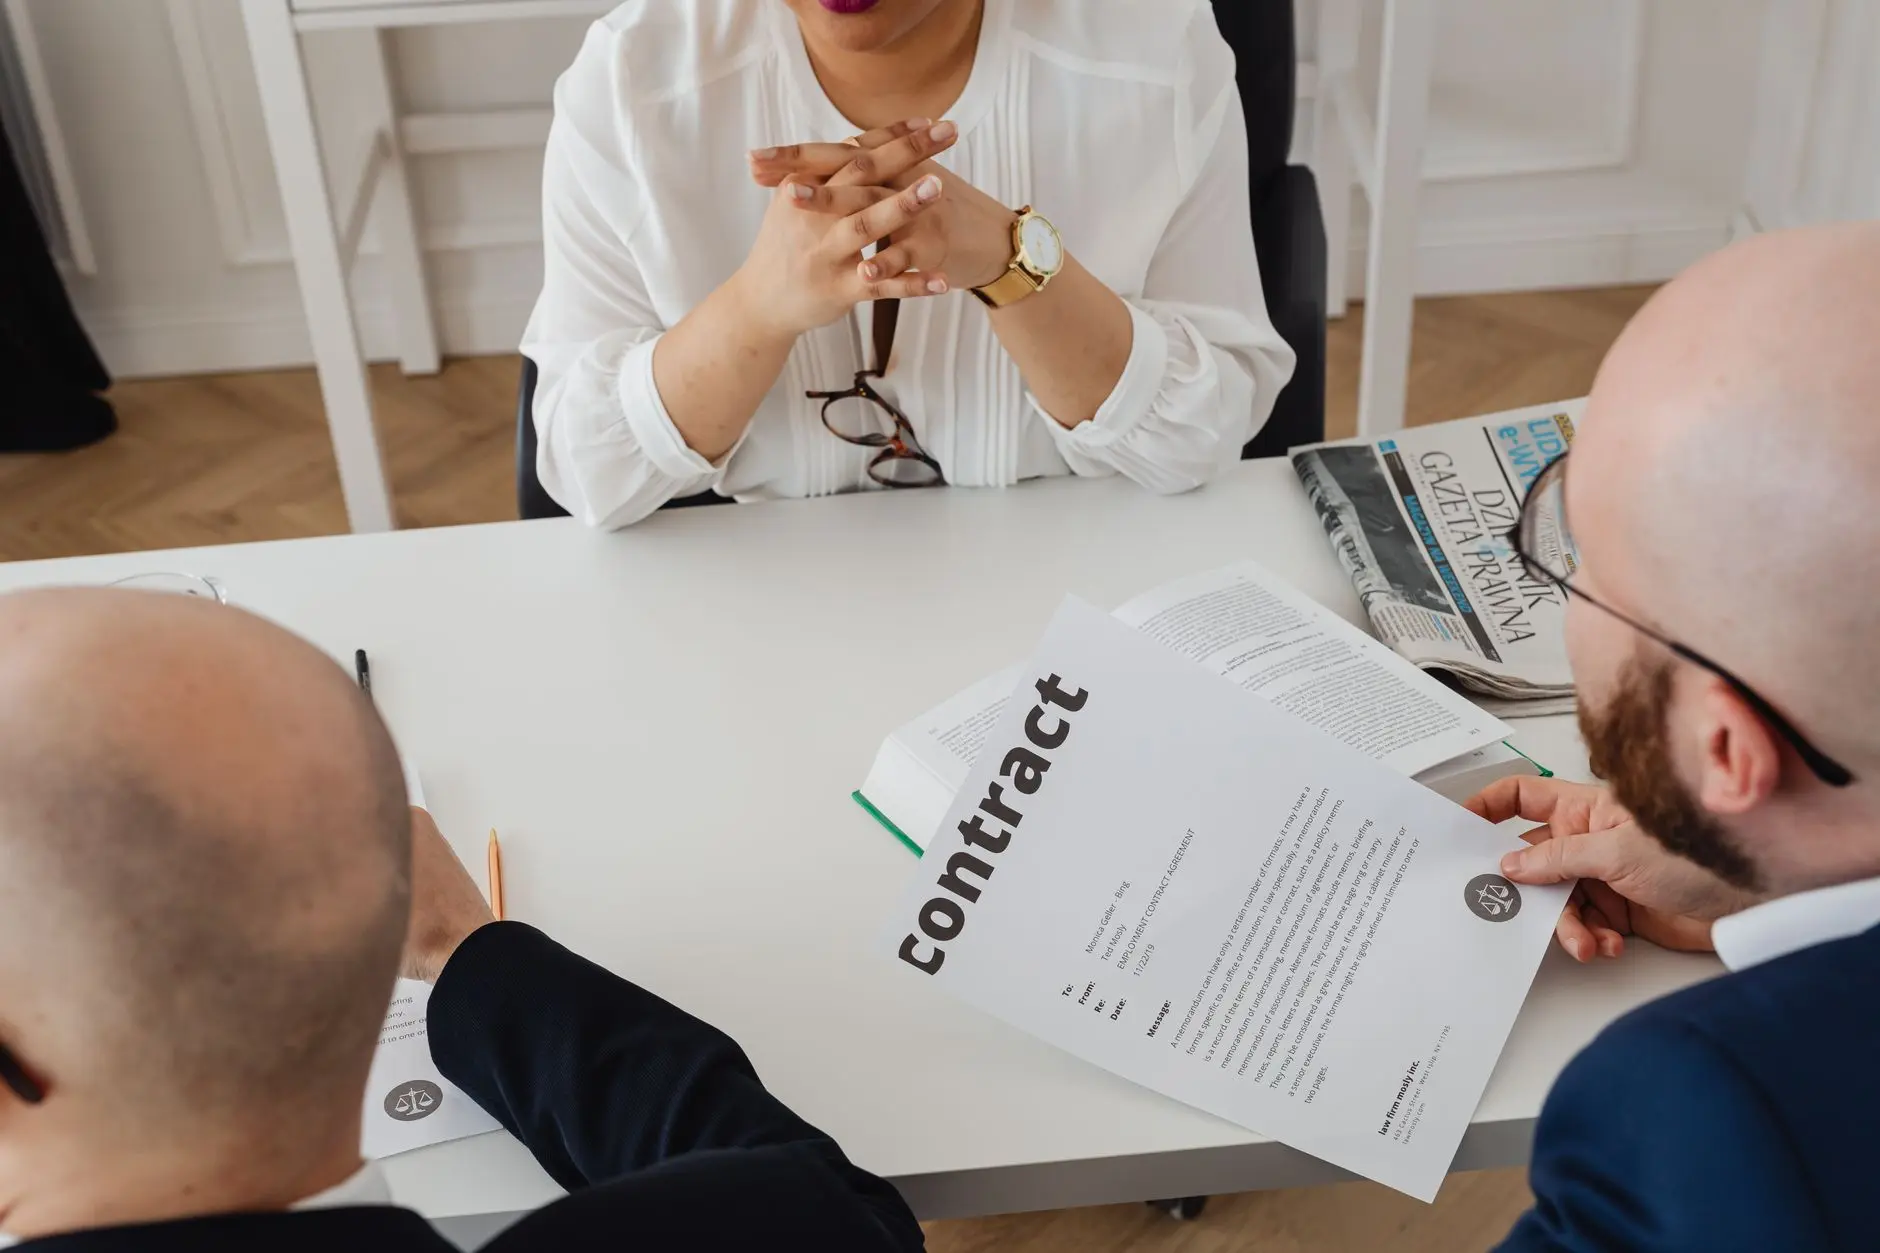
Law firms operate on strict pillars of client confidentiality, privilege, and professional accountability. As legal technology advances, many practices rush to adopt artificial intelligence to draft documents, summarize depositions, and conduct case research. However, before any firm integrates these systems, leadership must understand how law firms think AI governance using structured frameworks, risk assessments, and compliance guardrails. Unregulated adoption can trigger severe data breaches, ethical violations, and malpractice claims.
The Unique Risks of AI in Legal Practice
Unlike standard corporate enterprises, law firms handle highly sensitive dossiers, including intellectual property, mergers and acquisitions data, criminal evidence, and personal health information. When attorneys feed this information into third party large language models without vetting, they risk waiving attorney client privilege and violating data protection regulations like the GDPR.
According to a recent legal technology survey by Artificial Lawyer, over forty percent of mid sized firms admit to staff using consumer grade generative AI tools without formal institutional oversight. This creates a dangerous shadow IT environment where client secrets are processed on external servers without enterprise data processing agreements.
Establishing Core AI Governance Frameworks
Effective AI governance begins long before software installation. Law firm managing partners, chief information security officers, and risk committees must collaborate to establish clear boundaries. This requires understanding how data flows into, through, and out of any artificial intelligence tool.
- Data Minimization: Only input anonymized or redacted information into public or semi private AI models.
- Vendor Due Diligence: Demand transparent answers regarding whether vendor models are trained on firm specific inputs.
- Human in the Loop Validation: Never submit AI generated briefs or contracts to courts without rigorous manual review by qualified attorneys.
- Client Transparency: Update standard engagement letters to inform clients when and how artificial intelligence assists in legal work.
Regulatory Pressures and the EU AI Act
For practices operating within or advising clients in the European Union, the regulatory stakes are exceptionally high. The EU AI Act classifies certain legal decision support systems as high risk applications. This designation imposes stringent obligations regarding data quality, technical robustness, human oversight, and transparent record keeping.
Firms failing to comply face astronomical fines that can rival severe data protection penalties. Beyond legislation, local bar associations and law societies are rapidly issuing ethical guidance regarding competence in technology. Ignorance of how an AI tool hallucinates case law is no longer an acceptable defense in professional negligence disputes.
Comparing AI Deployment Models for Law Firms
| Deployment Model | Data Security Level | Governance Complexity | Recommended Use Case |
|---|---|---|---|
| Public Consumer AI | Very Low | High Risk | General brainstorming only with zero client data. |
| Enterprise SaaS AI | Moderate to High | Medium Risk | Internal knowledge management and secure document drafting. |
| On Premise Private LLM | Maximum | Low Risk | Deep document review involving highly confidential litigation files. |
Real World Scenario: The Danger of Unvetted Briefs
Consider a mid sized litigation firm where an associate uses a popular public AI chatbot to draft a motion summary. The associate pastes unredacted settlement figures and opposing party details into the prompt box. Unbeknownst to the associate, the platform retains this input to retrain its models. Weeks later, a competing firm prompts the same tool and receives details of the confidential settlement strategy. The resulting malpractice suit and reputational damage devastate the firm overnight.
Technology should empower the practice of law, not compromise the sacred duty of confidentiality that underpins the legal profession.
To prevent such incidents, risk teams must prioritize ongoing staff training and continuous compliance monitoring, aligning closely with internal compliance policies and broader data protection protocols.
Actionable Steps for Law Firm Leadership
Step 1: Conduct an AI Inventory. Audit all existing software to identify hidden or unsanctioned AI features embedded in standard office suites.
Step 2: Draft an Acceptable Use Policy. Define explicitly what data can and cannot be shared with artificial intelligence tools.
Step 3: Appoint an AI Ethics Officer. Designate a qualified individual or committee to vet new legal tech vendors before purchase.
Frequently Asked Questions
Can law firms use commercial AI tools without breaking client confidentiality?
Only if the firm uses enterprise tier versions with strict zero data retention guarantees and executed Data Processing Agreements that prohibit vendor training on firm inputs.
Are lawyers legally liable for AI hallucinations?
Yes. The attorney of record is ultimately responsible for every filing, citation, and legal argument submitted to a court, regardless of whether AI assisted in its creation.
How does the EU AI Act impact international law firms?
Any international firm processing data or deploying AI systems within the European Union must adhere to the EU AI Act requirements, particularly for high risk legal tools.
Conclusion
Artificial intelligence offers unprecedented efficiency for legal research, contract analysis, and administrative workflows. However, technological innovation must never outpace professional responsibility. When law firms think AI governance using proactive, security first methodologies, they safeguard client trust, maintain regulatory compliance, and build resilient modern practices ready for the future of law.









Leave a Reply