



Chinese Hackers Exploit ZyXEL Switch Vulnerability to Exfiltrate Data

Share
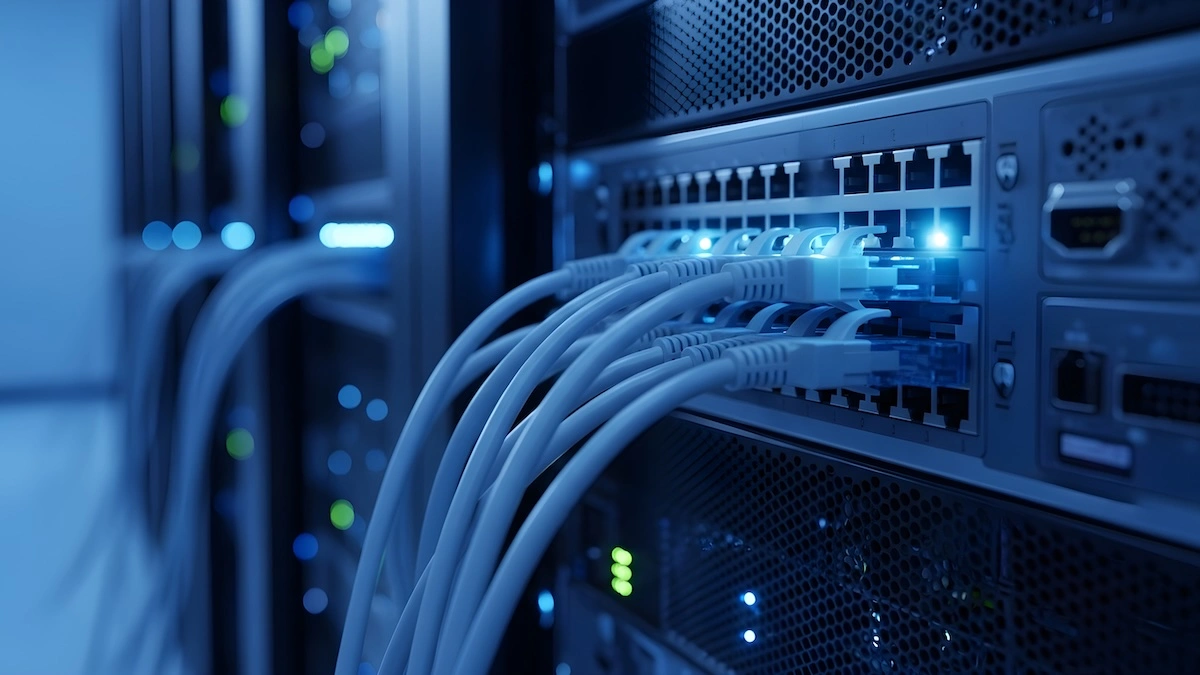
A Chinese threat actor has exploited a critical vulnerability in ZyXEL GS1900 switches to exfiltrate sensitive information from nearly 1,000 devices across 48 countries.
The security defect, tracked as CVE-2026-7273, has a CVSS score of 8.8. It is a stack-based buffer overflow that allows an attacker to execute operating system commands via specially crafted HTTP requests without requiring authentication.
Threat intelligence firm GreyNoise reported that the attackers utilised a heavily obfuscated Python script to target the devices. The script was used to steal hashed root credentials, network information, and configuration details. While the script specifically targeted firmware versions 2.10 through 2.90 of the GS1900-24, it included command-line options to target other firmware versions susceptible to the flaw.
GreyNoise also identified a significant security lapse among the victims: 564 of the compromised devices were still using factory default credentials, which facilitated the attackers’ access and potential for future intrusions.
CISA Mandates Patching for Federal Agencies
The US Cybersecurity and Infrastructure Security Agency (CISA) has added CVE-2026-7273 to its Known Exploited Vulnerabilities (KEV) catalogue. This inclusion mandates that federal agencies patch the affected systems within three days to mitigate the ongoing risk.
Researchers believe the threat actor may be closely related to the Red Heron hacking group, which has been observed exploiting other vulnerabilities in recent months, including targeting Gitea installations.
ZyXEL released security updates in June to patch the bug in ten different GS1900 switch models. Organisations using these devices should immediately ensure they have applied the latest firmware updates and changed all factory default credentials.












Leave a Reply