

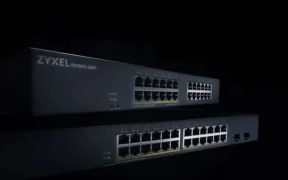
Zyxel has issued urgent security updates for its GS1900 series network switches following the discovery of a zero-day vulnerability used to compromise nearly 1,000 devices globally.
A Chinese-speaking threat actor exploited vulnerabilities in ZyXEL GS1900 switches and WordPress to steal over 18,500 records from backend databases.
Threat actors exploited CVE-2026-7273 in ZyXEL GS1900 switches to steal credentials and configuration data from devices across 48 countries.
CISA has mandated that federal agencies patch a high-severity Zyxel GS1900 series switch vulnerability after reports of active exploitation and data exfiltration.













