



A SIMple Privacy Checklist for SMEs Handling Location Data

Share
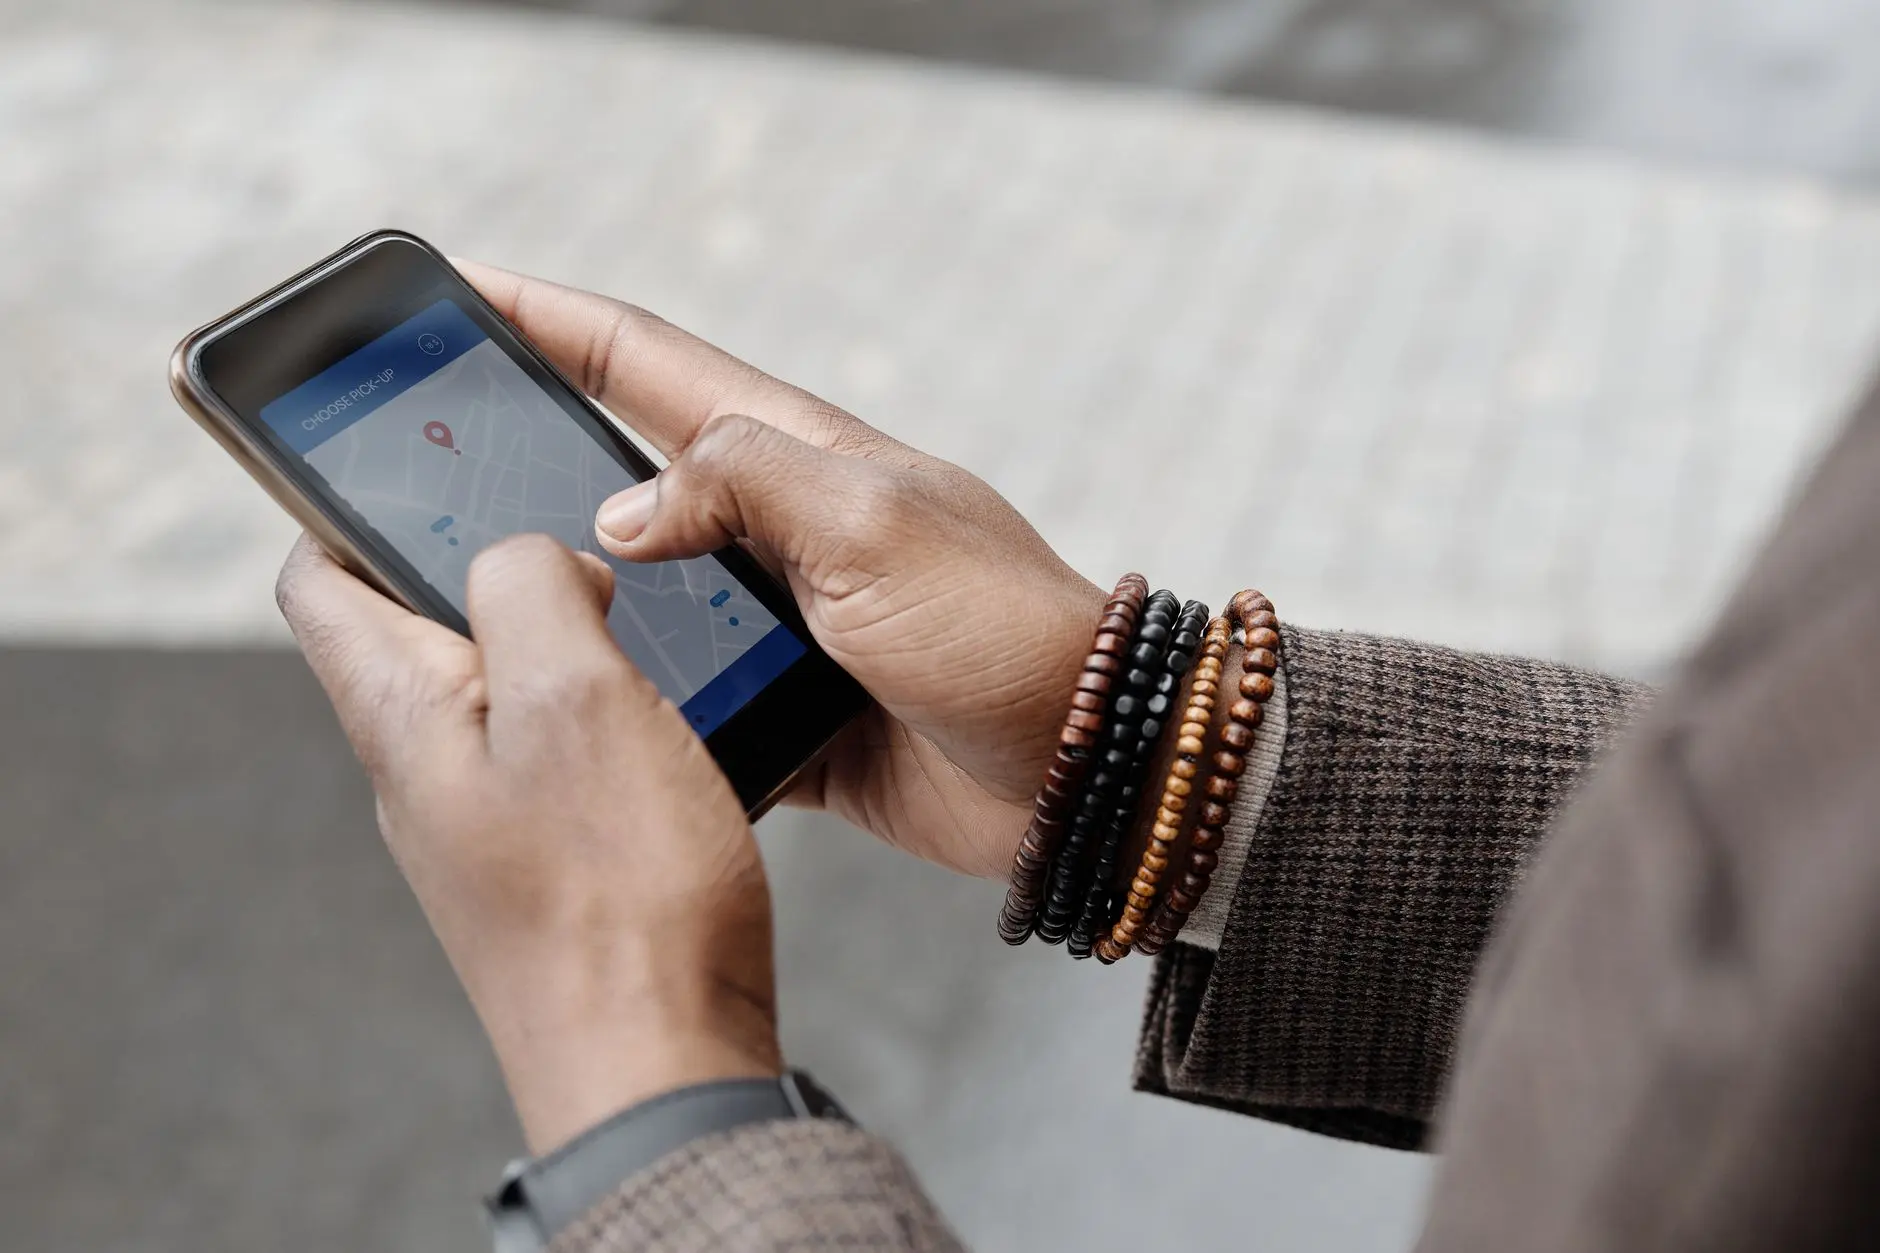
For many small and medium-sized enterprises (SMEs), geolocation data is a goldmine for business intelligence, personalized marketing, and operational efficiency. Whether you are running a food delivery service, a fitness app, or a retail store tracking foot traffic, the ability to pinpoint a user’s location is invaluable. However, this data is classified as highly sensitive under most global compliance frameworks, including the GDPR and CCPA. Mishandling it is not just a regulatory risk; it is a direct threat to your customers’ safety.
Understanding the Risk of Location Data
Location data can reveal more about a person than almost any other data point. It identifies where they live, where they work, and their behavioral patterns. If breached, the consequences for the data subject are severe—ranging from targeted harassment to physical safety risks. For an SME, a leak of precise location history can lead to massive fines and irrevocable reputational damage.
Dr. Ann Cavoukian, former Information and Privacy Commissioner of Ontario, often emphasizes: Privacy is not about hiding; it is about control. When SMEs collect location data without giving users genuine control, they are walking on thin ice.
The Essential Checklist for SMEs Handling Location
To keep your operations secure, use this Checklist for SMEs Handling Location as your foundation. This list is designed to transition your business from reactive data handling to a privacy-first culture.
- Data Minimization: Are you collecting only what is strictly necessary? If you only need a city, do not collect exact GPS coordinates.
- Granular Consent: Do users understand they are sharing location data? Ensure consent is informed, specific, and easy to withdraw.
- Storage Limitation: Do not hoard data. Once the purpose for the location tracking is fulfilled, delete or anonymize the record.
- Encryption in Transit and at Rest: Ensure that location pings are encrypted using industry-standard protocols (e.g., TLS 1.3) to prevent interception.
- Access Controls: Limit internal access to raw location data to only those employees who absolutely require it for their roles.
- Privacy Impact Assessments (PIA): Conduct a formal review before launching any new feature that tracks user movement.
| Risk Level | Data Type | Handling Requirement |
|---|---|---|
| Low | City or Region only | General disclosure in policy |
| Medium | Approximate Postcode | Anonymization after 30 days |
| High | GPS Coordinates | Real-time encryption and strict TTL |
Real-Life Scenario: The Delivery App Trap
Consider an SME running a local courier app. They tracked drivers and customers in real-time. By failing to delete historical logs, they inadvertently created a database showing the exact addresses and movement patterns of hundreds of residents. A simple SQL injection attack exposed this entire archive. This illustrates why the principle of data minimization—as discussed in our guide on data protection—is critical. If the data had been deleted 24 hours after delivery, the breach would have been neutralized.
Actionable Steps for Privacy Teams
To mature your internal processes, follow these three steps immediately:
- Perform a Data Audit: Map out where location data enters your system, where it is stored, and who has access to it.
- Review Third-Party SDKs: Many apps use third-party tools for analytics. Ensure these partners are not siphoning off location data without your knowledge or the user’s consent. Refer to official regulatory guidance on tracking technologies to verify your compliance posture.
- Automated Purge Policies: Implement automated scripts that delete or redact precise location data after a set period.
FAQ Section
Is anonymized location data still personal data?
Often, yes. Studies have shown that even anonymized location datasets can be re-identified by comparing them with public records. Treat all location data with high care, regardless of claims of anonymization.
How often should I update my privacy policy?
Your privacy policy must be a living document. Update it whenever you change how you collect, process, or share location data. Transparency is a key pillar of user trust.
Can I rely on consent for all location tracking?
No. Consent must be freely given. If your core service can function without constant location tracking, do not make the app unusable if the user denies permission.
Conclusion
Managing location data is a significant responsibility for any SME. By strictly adhering to the Checklist for SMEs Handling Location, you can mitigate legal risks while building a relationship of trust with your users. Remember, privacy is not a checkbox exercise; it is an ongoing commitment to the safety of the individuals who rely on your services. Audit your systems, minimize your collection, and prioritize transparency to secure your business’s future.











Leave a Reply