



Unpatched Ubuntu Linux Flaw Enables Container Escape to Host Root

Share
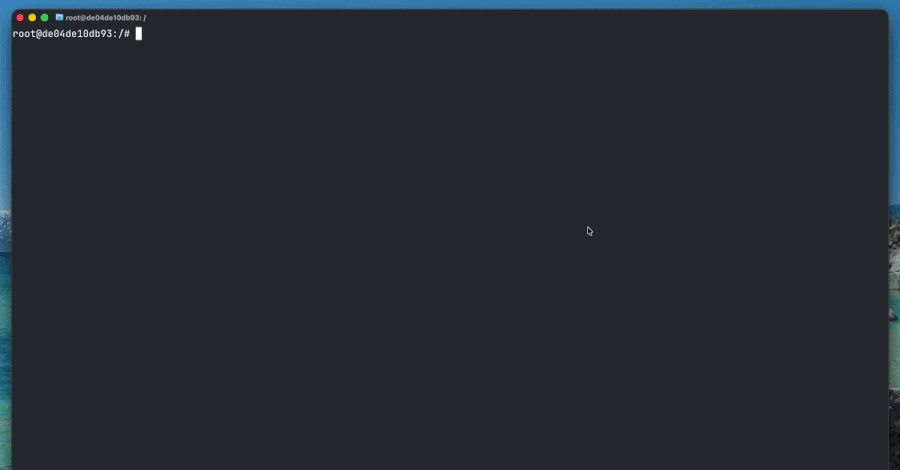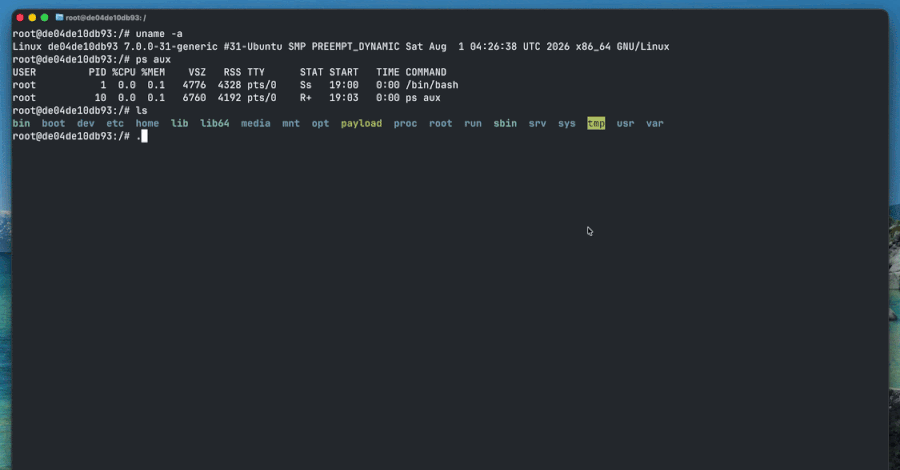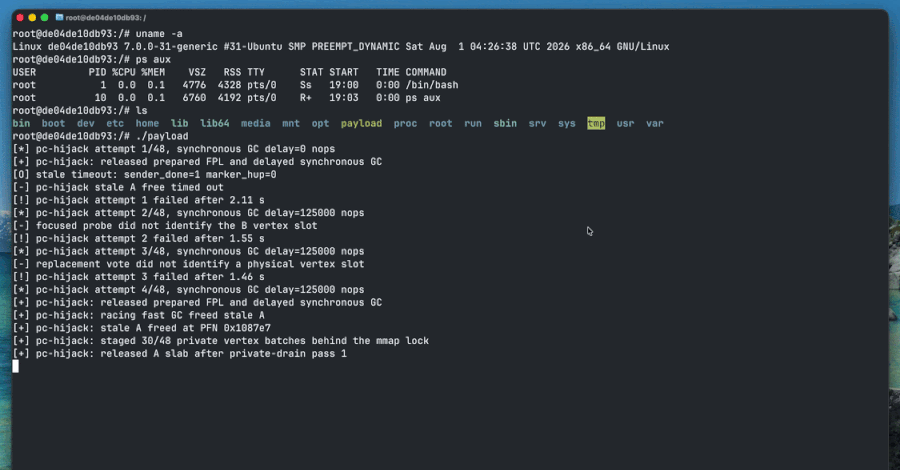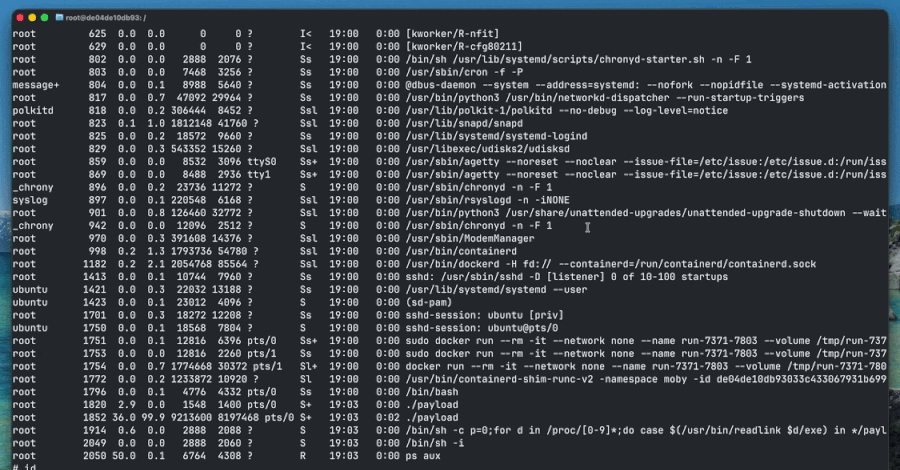
A use-after-free vulnerability in the Linux kernel’s AF_UNIX socket subsystem can be used to escape a container and gain root access on the host system. The flaw, tracked as CVE-2026-80521, affects multiple Ubuntu Long Term Support (LTS) releases, including 22.04, 24.04, and 26.04.
Security firm DepthFirst disclosed the research, which assigns the flaw a CVSS score of 7.8. While the vulnerability was addressed in the upstream Linux kernel on 6 August, Ubuntu has not yet shipped the necessary patches for its affected releases. This includes kernel packages used in AWS, Azure, and GCP workloads.
Technical Details
The vulnerability is located in the kernel’s garbage collector for AF_UNIX sockets. This component manages file descriptors passed between processes through SCM_RIGHTS messages. A race condition in the garbage collector allows it to see new references before the data carrying them has been queued. This can lead the collector to free part of a group of linked sockets without removing a pointer from a persistent internal list, allowing subsequent passes to follow that pointer into freed memory.
The vulnerable code was introduced in kernel 6.10 and backported to stable branches 6.1 and 6.6. Because AF_UNIX sockets are allowed by default in many Docker and Kubernetes seccomp profiles, the exploit can bypass namespace isolation, cgroup limits, and seccomp filtering to reach the kernel through ordinary system calls.
Mitigation and Discovery
Ubuntu’s security tracker currently lists the Linux package for version 26.04 as “vulnerable, work in progress,” with no specific update date provided. As no official workaround has been published by Ubuntu, DepthFirst recommends that organisations move untrusted workloads to microVM isolation environments such as Firecracker or Kata Containers. These solutions provide each workload with its own kernel to prevent host compromise.
The flaw was discovered using the dfs-large1 AI model in conjunction with human-operated testing. The research highlights the increasing role of AI-assisted vulnerability discovery, which experts suggest is lowering the barrier for attackers to breach container security boundaries.









Leave a Reply