



A Step-by-Step Guide to Managing School Records Responsibly

Share
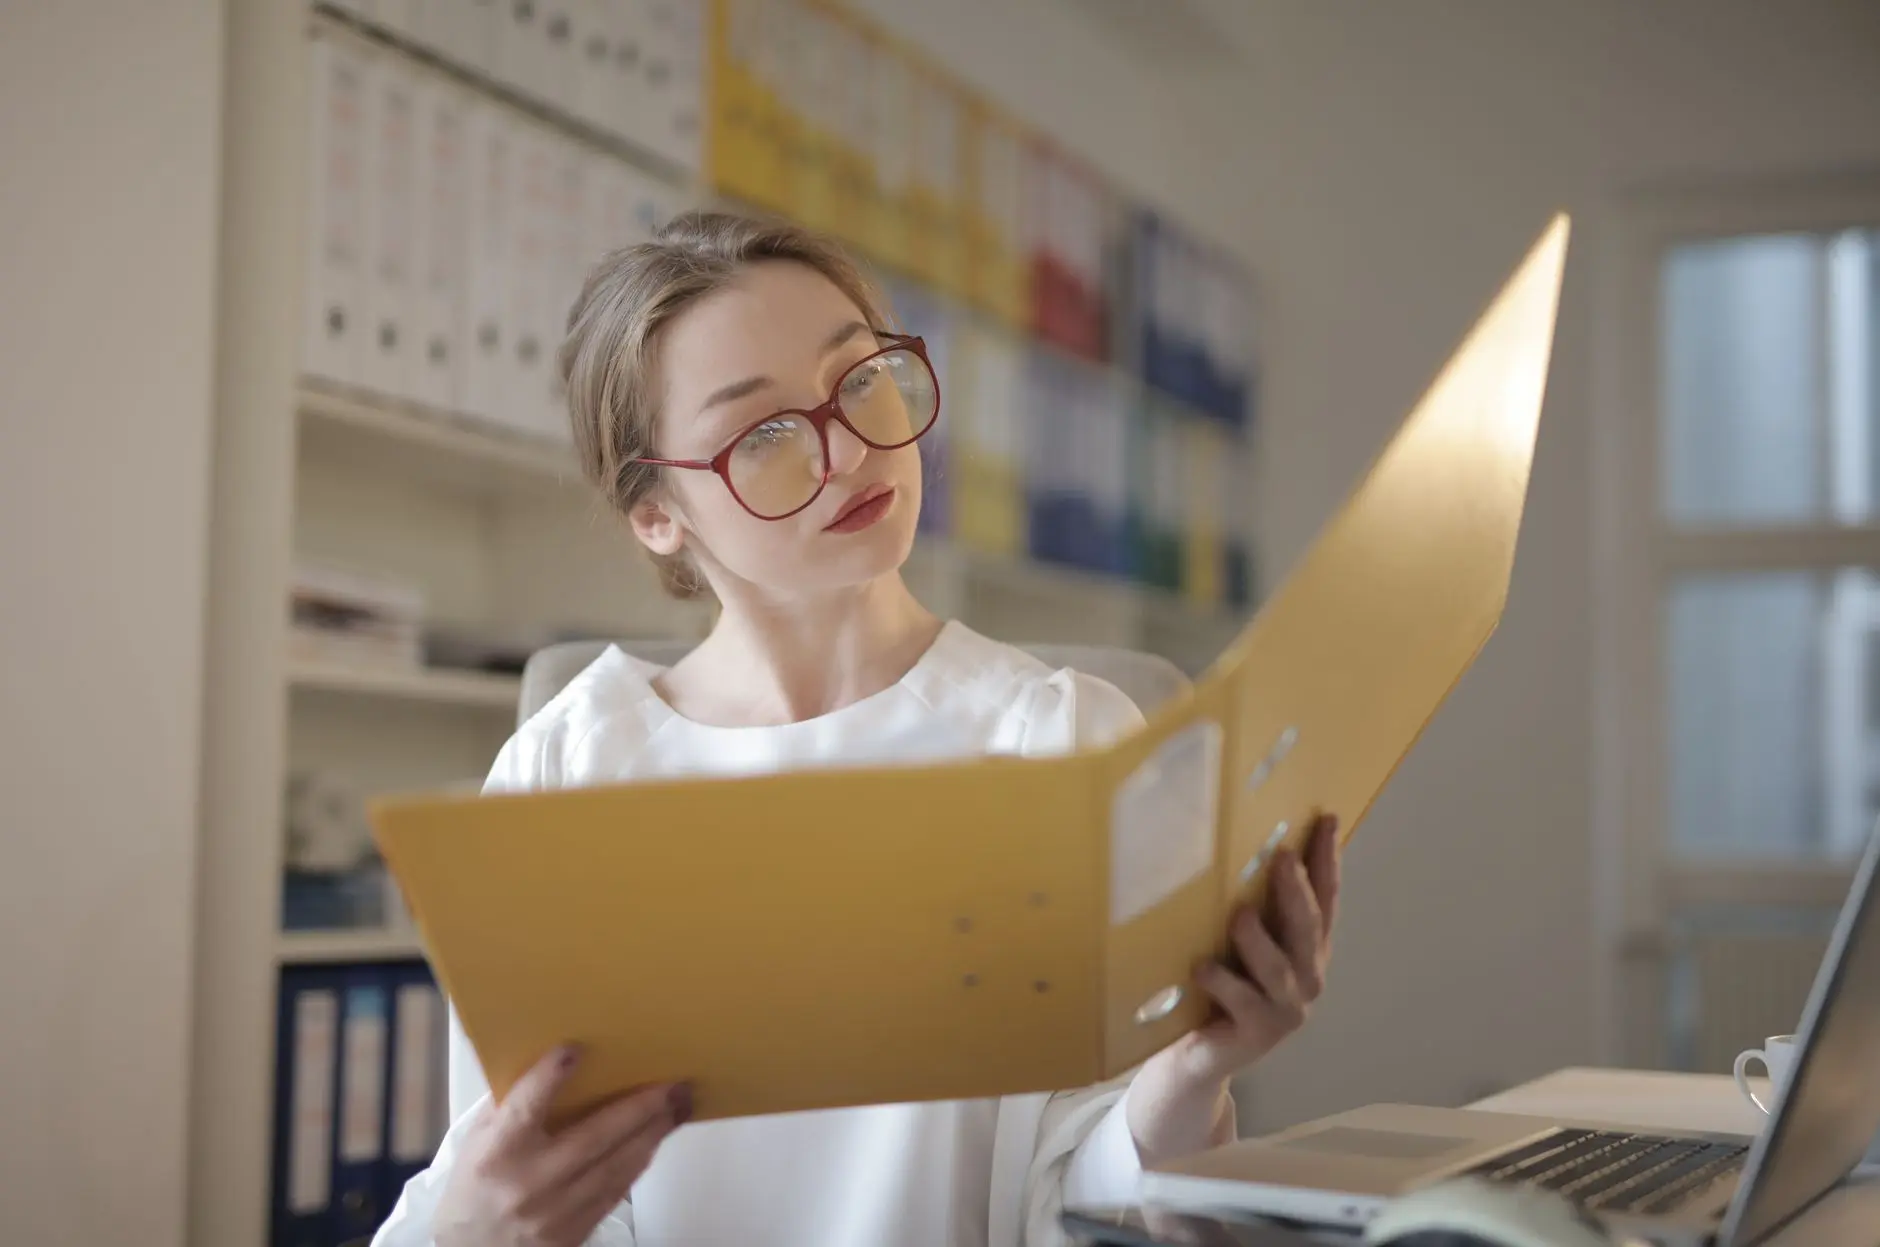
Educational institutions handle vast troves of sensitive data daily. From academic transcripts and psychological evaluations to biometric attendance logs and financial aid details, schools possess a comprehensive digital and physical portrait of every student. Mishandling this information exposes minors to identity theft, schools to severe regulatory penalties, and institutions to devastating cyberattacks. Establishing a rigorous framework is no longer optional. It requires deliberate action and a structured approach to Step Step Managing School Records Responsibly across all administrative departments.
As privacy regulations tighten globally, including stricter interpretations of educational privacy frameworks like FERPA in the United States, GDPR in Europe, and emerging data protection acts worldwide, accountability falls squarely on school administrators, IT directors, and governing boards. This guide provides a clear roadmap to secure student records, streamline retention, and build long-term digital trust.
The Core Principles of Educational Data Governance
Before implementing new workflows, organizations must understand the foundational pillars of educational privacy. Student data is inherently vulnerable because minors lack the legal capacity to manage their own digital footprints, placing an ethical and legal obligation on educators to act as steadfast guardians.
According to the U.S. Department of Education Family Policy Compliance Office, safeguarding student privacy requires continuous training, strict access controls, and transparent communication with parents and eligible students regarding how their data is collected and processed.
To establish an effective data protection program, educational administrators should adhere to these core principles:
- Data Minimization: Only collect information that is strictly necessary for educational, administrative, or safety purposes.
- Purpose Limitation: Use collected records exclusively for the stated educational objective and never sell or monetize student profiles.
- Storage Limitation: Establish clear retention schedules so that records are securely destroyed or anonymized once they are no longer needed.
- Integrity and Confidentiality: Implement robust technical measures, such as encryption and multi-factor authentication, to prevent unauthorized access or accidental leaks.
Step 1: Conduct a Comprehensive Data Inventory
You cannot protect what you do not know you have. The first phase of Step Step Managing School Records Responsibly is creating a complete inventory of all student and staff records across the entire institution. This includes legacy paper files sitting in basement filing cabinets and modern cloud-based learning management systems.
Map every data flow by asking key questions: Where does the information enter the school? Who has access to it? Where is it stored, and which third-party vendors process it? Often, schools discover numerous shadow IT tools deployed by individual teachers without administrative oversight, creating hidden vulnerabilities that must be immediately addressed.
Step 2: Establish Strict Access Controls and Permissions
Not every staff member needs access to every file. A substitute teacher does not require visibility into a student’s medical history or disciplinary record. Applying the principle of least privilege ensures that users only have access to the specific files required to perform their direct duties.
Implement role-based access controls within your database software and secure physical filing rooms with biometric scanners or keyed entry logs. Regularly audit these permissions, especially at the start of each academic term when staff turnover is high.
Step 3: Define and Enforce Retention and Disposal Schedules
Retaining records indefinitely creates unnecessary liability. If a school holds onto old disciplinary notices or redundant test scores for decades, it expands the potential attack surface for cybercriminals. Conversely, destroying records prematurely can violate legal compliance mandates.
Consult local regulatory requirements to establish clear timelines for how long different categories of educational records must be kept. Once that retention period expires, data must be permanently shredded or digitally wiped using Department of Defense standards to ensure it cannot be recovered.
| Record Type | Standard Retention Period | Disposal Method |
|---|---|---|
| Permanent Academic Transcripts | Permanent / 50+ Years | Encrypted Digital Archive / Secure Offsite Storage |
| Disciplinary Actions | 1 to 3 Years Post-Graduation | Secure Digital Shredding or Pulping |
| Attendance and Daily Logs | Current Academic Year + 1 Year | Automated Purge in SIS Software |
| Student Health and Medical Files | Age of Majority + 7 Years | Secure Physical Shredding / Encrypted Deletion |
Step 4: Vet EdTech Vendors and Third-Party Suppliers
Modern classrooms rely heavily on third-party software applications, ranging from digital math games to cloud storage providers. However, external vendors represent one of the most common vectors for data breaches in the education sector. Before integrating any software into the school network, compliance teams must review the vendor’s data processing agreement.
Ensure that third-party suppliers encrypt data both in transit and at rest, prohibit data mining of student accounts for advertising purposes, and agree to notify the school immediately in the event of a security incident. A robust compliance framework must extend beyond school walls to encompass every software partner.
Real-Life Scenario: The Risk of Unmonitored Cloud Storage
Consider the case of a mid-sized regional school district where a well-meaning teacher uploaded student progress reports, including special education accommodations and home addresses, to a public cloud storage folder to easily share files from home. Because the sharing settings were configured incorrectly, search engines indexed the directory, exposing the records of hundreds of minors.
The incident triggered an emergency investigation by state privacy regulators, severe reputational damage, and costly mandatory credit monitoring notifications for affected families. This real-world failure highlights why technical guardrails and ongoing staff training are essential components of Step Step Managing School Records Responsibly.
Frequently Asked Questions
What is the biggest mistake schools make with record management?
The most common error is hoarding data indefinitely without a clear retention policy, which significantly increases exposure during a cyberattack.
Who is ultimately responsible for student data privacy?
While IT teams and compliance officers manage day-to-day security, ultimate legal responsibility rests with school board leadership and institutional executives.
How often should record access policies be reviewed?
Access privileges and vendor agreements should be audited at least bi-annually, or immediately following major staffing changes.
Conclusion
Managing educational records responsibly is an ongoing commitment rather than a one-time project. By conducting thorough data inventories, enforcing strict access controls, adhering to realistic retention schedules, and vetting every piece of classroom software, educational institutions can protect their students and preserve public trust. Prioritizing data privacy ensures that schools remain safe environments where learning can flourish without compromise.










Leave a Reply