



Best Practices for Managing Biometric Data in SMEs

Share
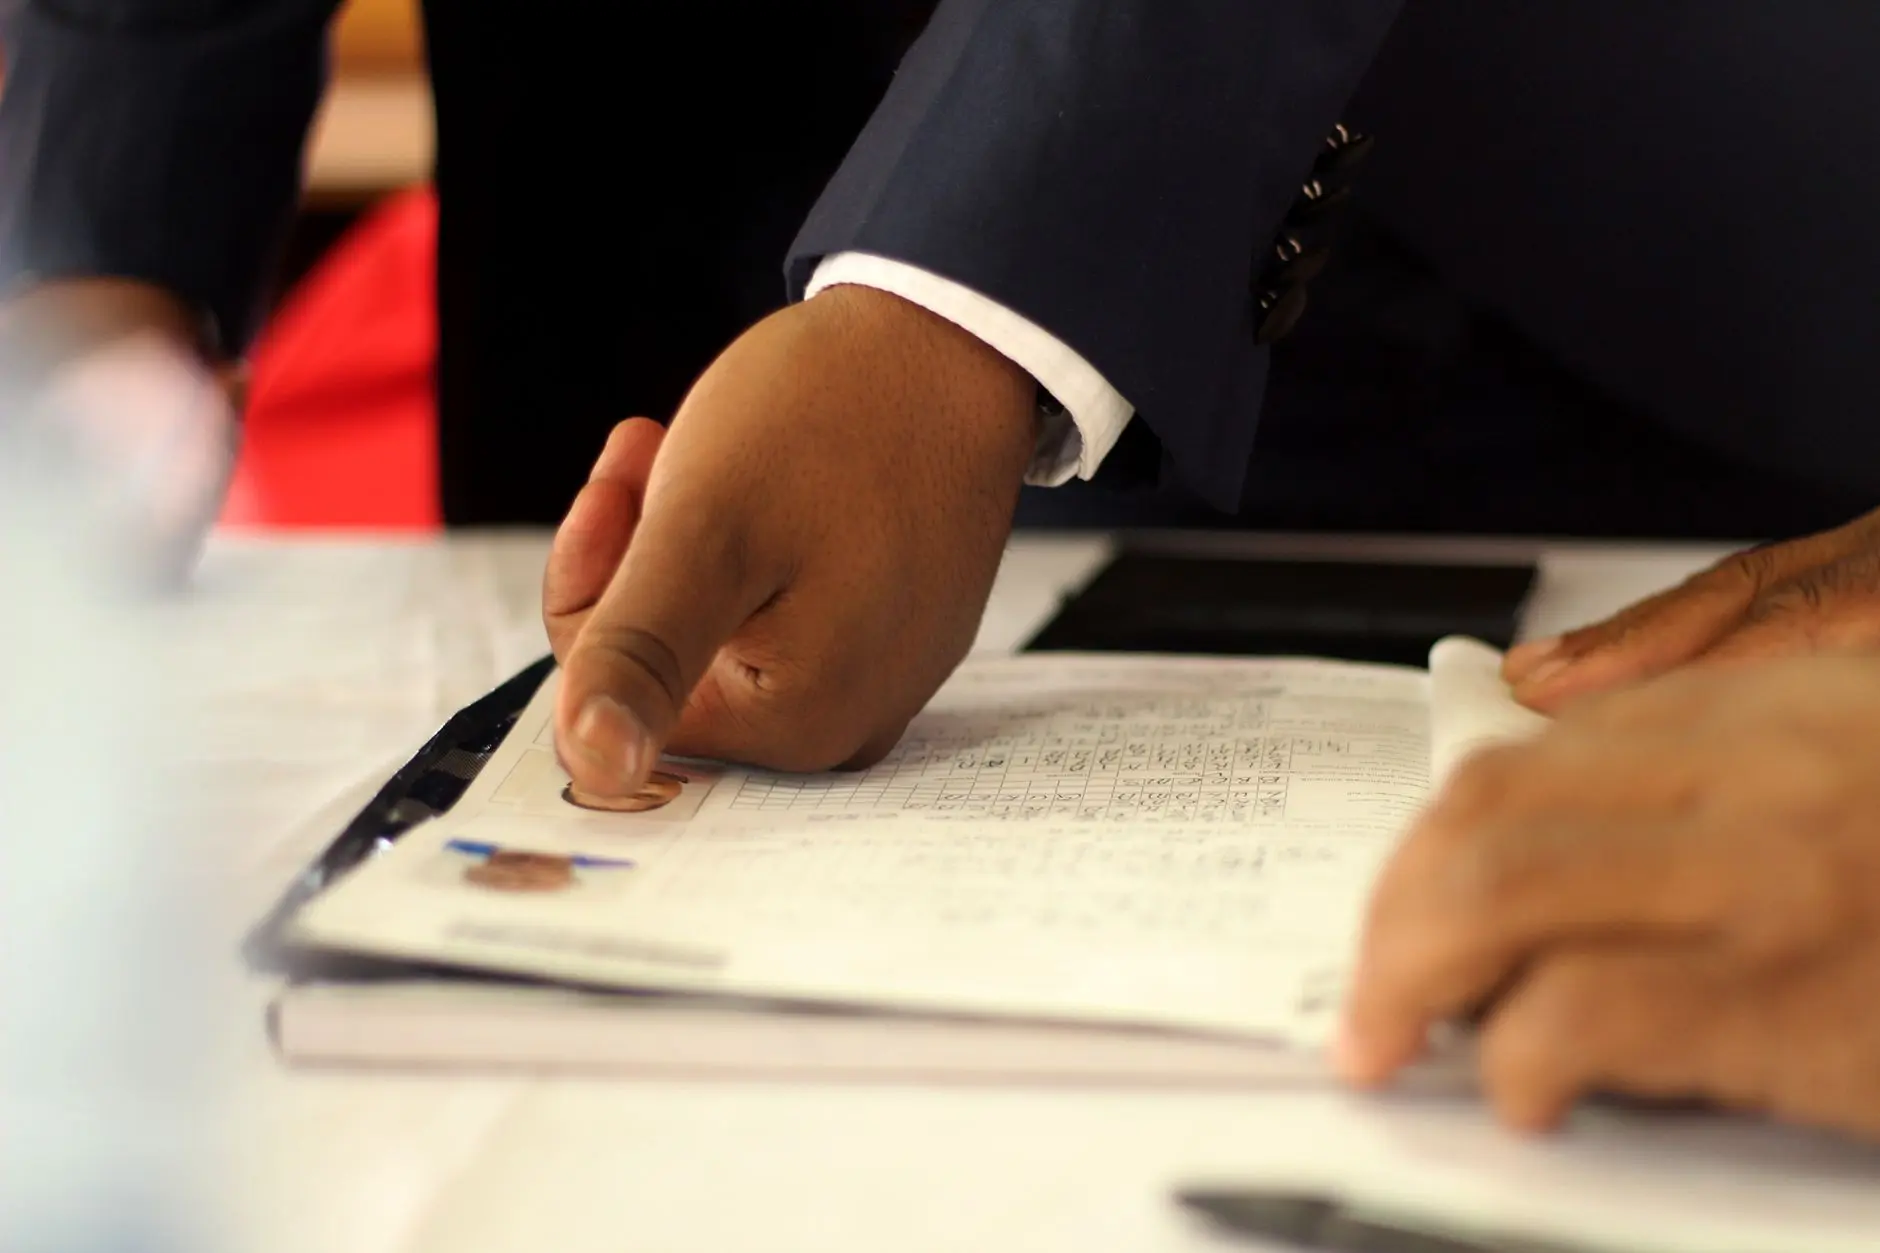
The Risks of Biometric Adoption
Small and Medium-sized Enterprises (SMEs) are increasingly turning to biometric authentication—such as fingerprint readers, facial recognition, and iris scanning—to secure office facilities or manage employee time tracking. Unlike a password, which can be reset if compromised, biometric data is immutable. Once a biometric profile is stolen, it is gone forever. For an SME, the breach of a biometric database is not just a technical failure; it is a permanent loss of trust and a significant regulatory liability.
The Core Principles of Biometric Governance
When implementing these systems, leadership must shift from a ‘convenience-first’ mindset to a ‘privacy-by-design’ approach. The National Institute of Standards and Technology provides foundational frameworks for testing the accuracy and security of these systems. Adopting Best Practices Managing Biometric SMEs requires strict adherence to data minimization and encryption standards.
1. Data Minimization
Never store raw biometric images. Modern systems should convert fingerprints or facial geometry into mathematical ‘hashes’ or templates. Once the template is created, the original image must be securely deleted. This ensures that even if a database is accessed by an unauthorized party, they cannot reconstruct a usable image of an employee’s biometric trait.
2. Encryption at Rest and in Transit
All biometric templates must be encrypted using strong, industry-standard algorithms. Ensure that the data is encrypted not only while stored on the server but also during the transmission from the scanner to the storage point. SMEs often fail here by using legacy systems that transmit data in plain text.
3. Informed Consent
Employees must be fully aware of what data is being collected, why it is needed, and how long it will be stored. Voluntary consent is a legal requirement in many jurisdictions. If an employee is uncomfortable using a biometric scanner, the company should always offer an alternative, such as a secure key card or PIN, without negative professional consequences.
Practical Comparison: Biometric Storage Strategies
| Strategy | Privacy Impact | Security Risk |
|---|---|---|
| Centralized Database | High Risk | Single point of failure |
| Local Device Storage | Low Risk | Hardware-specific risk |
| Template-Only Storage | Minimal Risk | Mathematical abstraction |
Case Study: The Cost of Improper Management
Consider a retail SME that implemented facial recognition for employee time-keeping. The system stored images locally on a tablet without encryption. When the tablet was stolen during a break-in, the attacker gained access to the biometric images of fifty staff members. Because the company failed to use template-based hashing, they faced massive regulatory fines under local compliance laws and had to provide credit monitoring services to every affected employee. This incident serves as a stark reminder that convenience rarely outweighs the duty of care.
Implementing a Compliance Framework
Before deploying any hardware, your team must conduct a Data Protection Impact Assessment (DPIA). This document identifies the necessity of the biometric system and outlines the specific technical controls in place to mitigate potential harm. Following data protection principles means that you have documented the lifecycle of the data, from collection to secure destruction.
Checklist for SME Leaders
- Verify that your biometric vendor does not retain copies of your data.
- Ensure biometric systems are isolated from the main corporate network.
- Establish a clear policy for deleting biometric templates immediately upon employee termination.
- Regularly audit logs to see who is accessing the authentication server.
FAQ: Common Questions on Biometric Data
Is it mandatory for employees to use biometrics?
In most professional settings, employers should offer non-biometric alternatives to respect individual privacy preferences and legal rights.
How long should I keep biometric data?
You should only keep it for as long as the employment contract necessitates. Once an employee leaves, their biometric template should be purged from your systems within a predefined timeframe.
Conclusion
Managing biometric data is not merely a task for the IT department; it is a fundamental pillar of modern organizational ethics. By following these Best Practices Managing Biometric SMEs, you safeguard your staff and fortify your business against the catastrophic impact of identity theft and regulatory scrutiny. Prioritize encryption, practice strict data minimization, and always provide alternatives to biometric collection to build a culture of digital trust.










Leave a Reply